Adversary Fluency
Face the threat actors already active in your industry
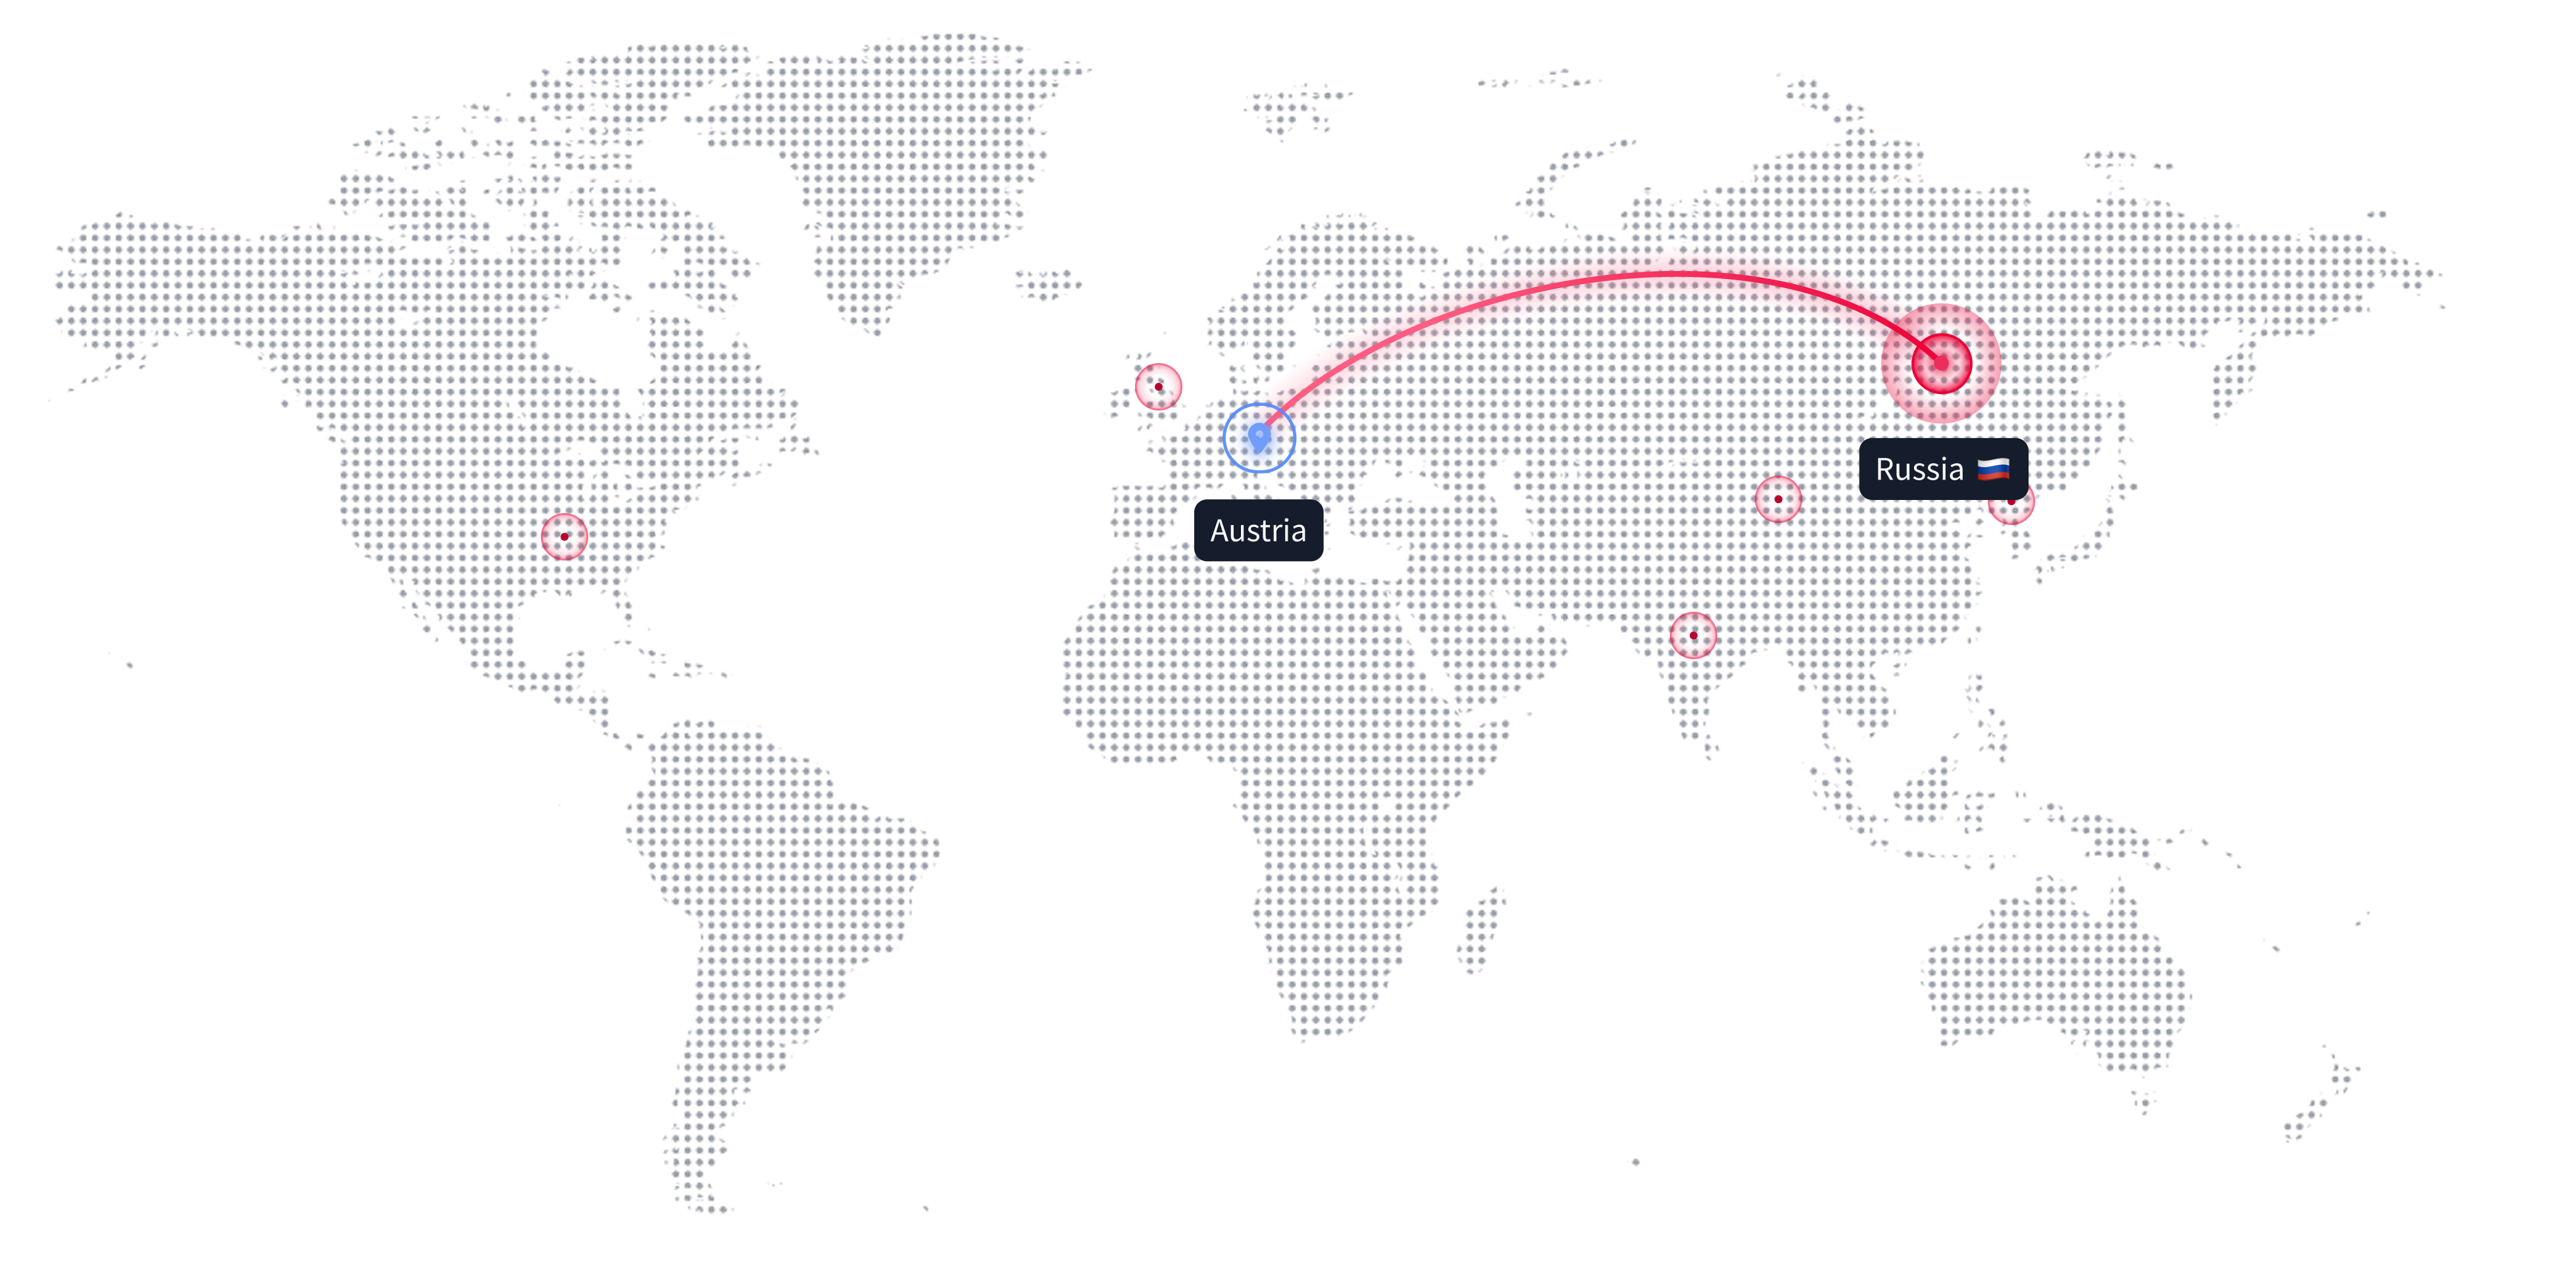
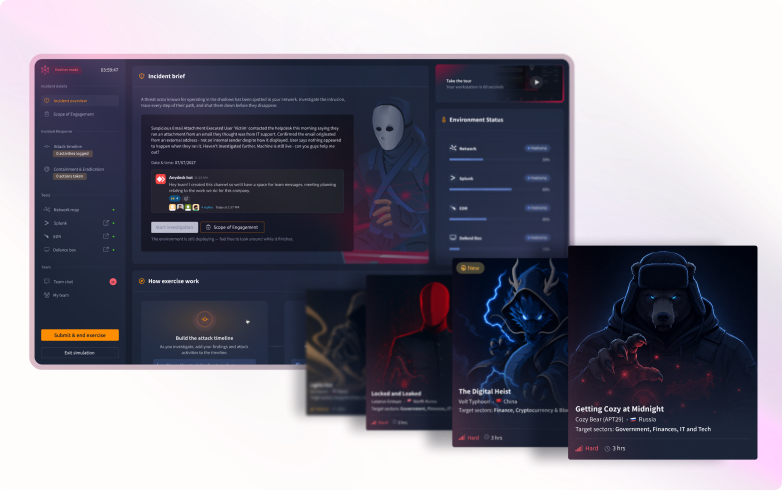
Each range scenario is modeled on a specific, named threat actor, giving the team pattern-recognition for behavior they could genuinely encounter, not a stylized CTF challenge.
Named threat-actor scenarios
Pick a scenario modeled on Lazarus Group, Volt Typhoon, APT29 (Cozy Bear) or DarkGate, real adversaries, not fictional ones.
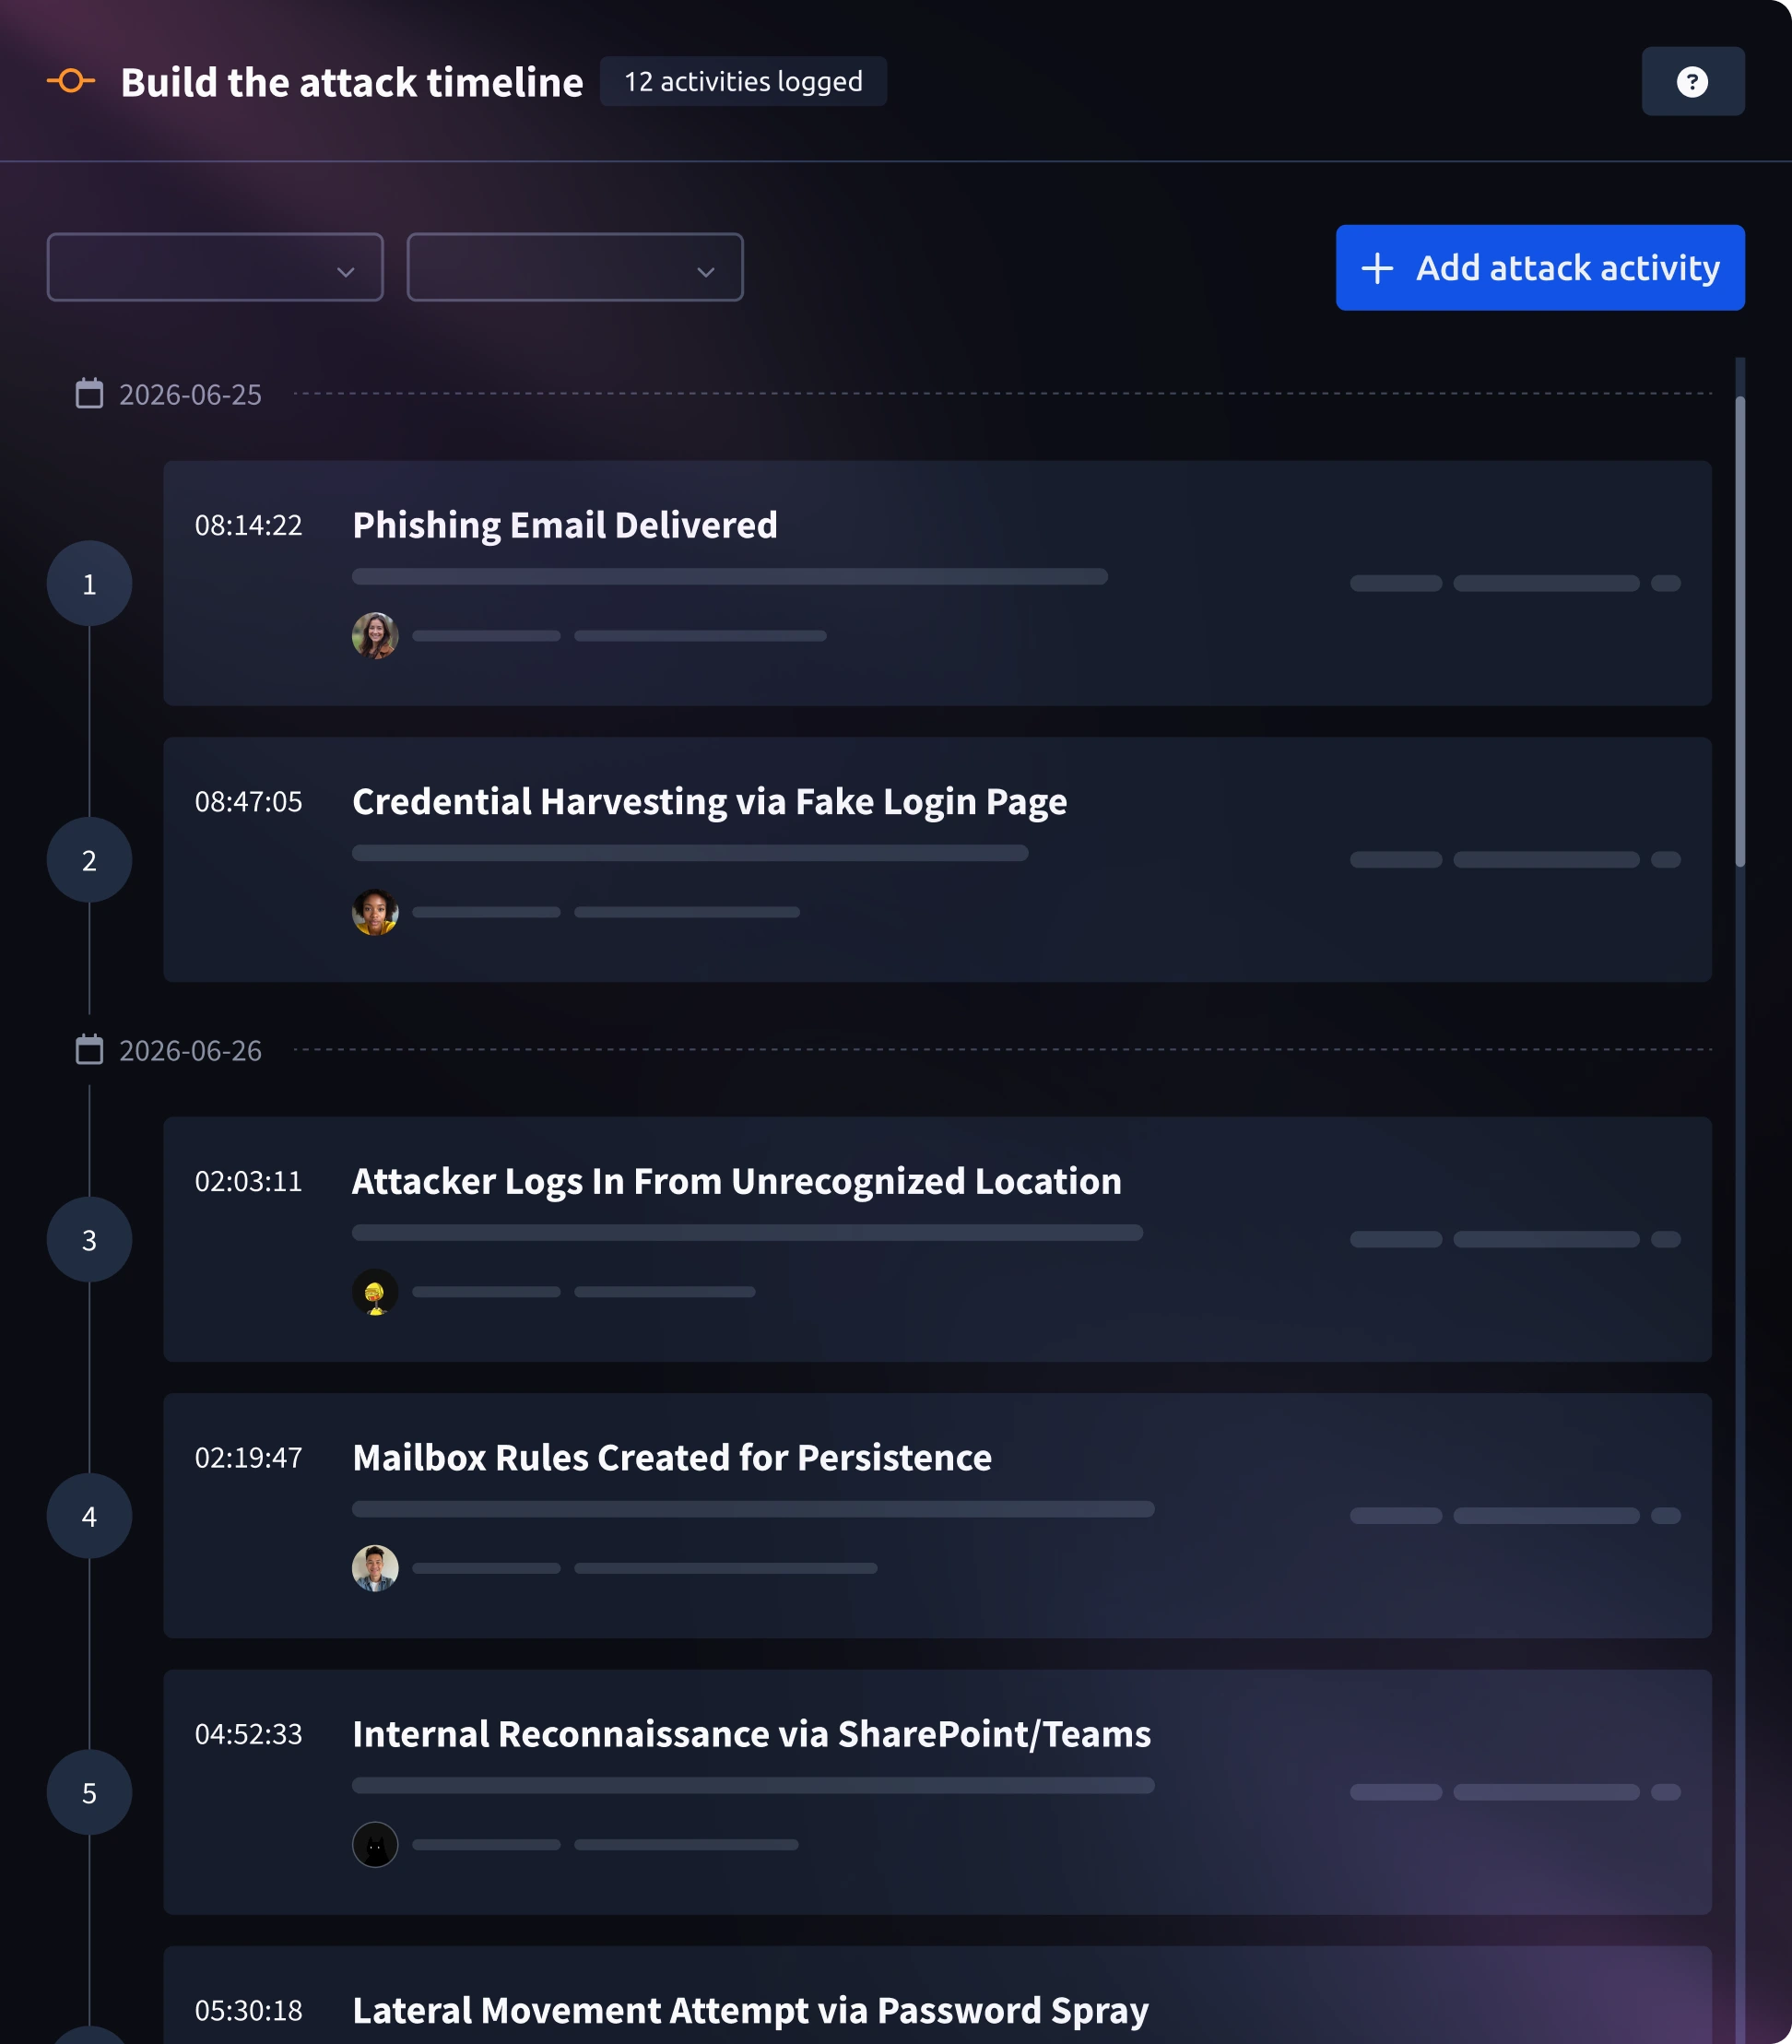
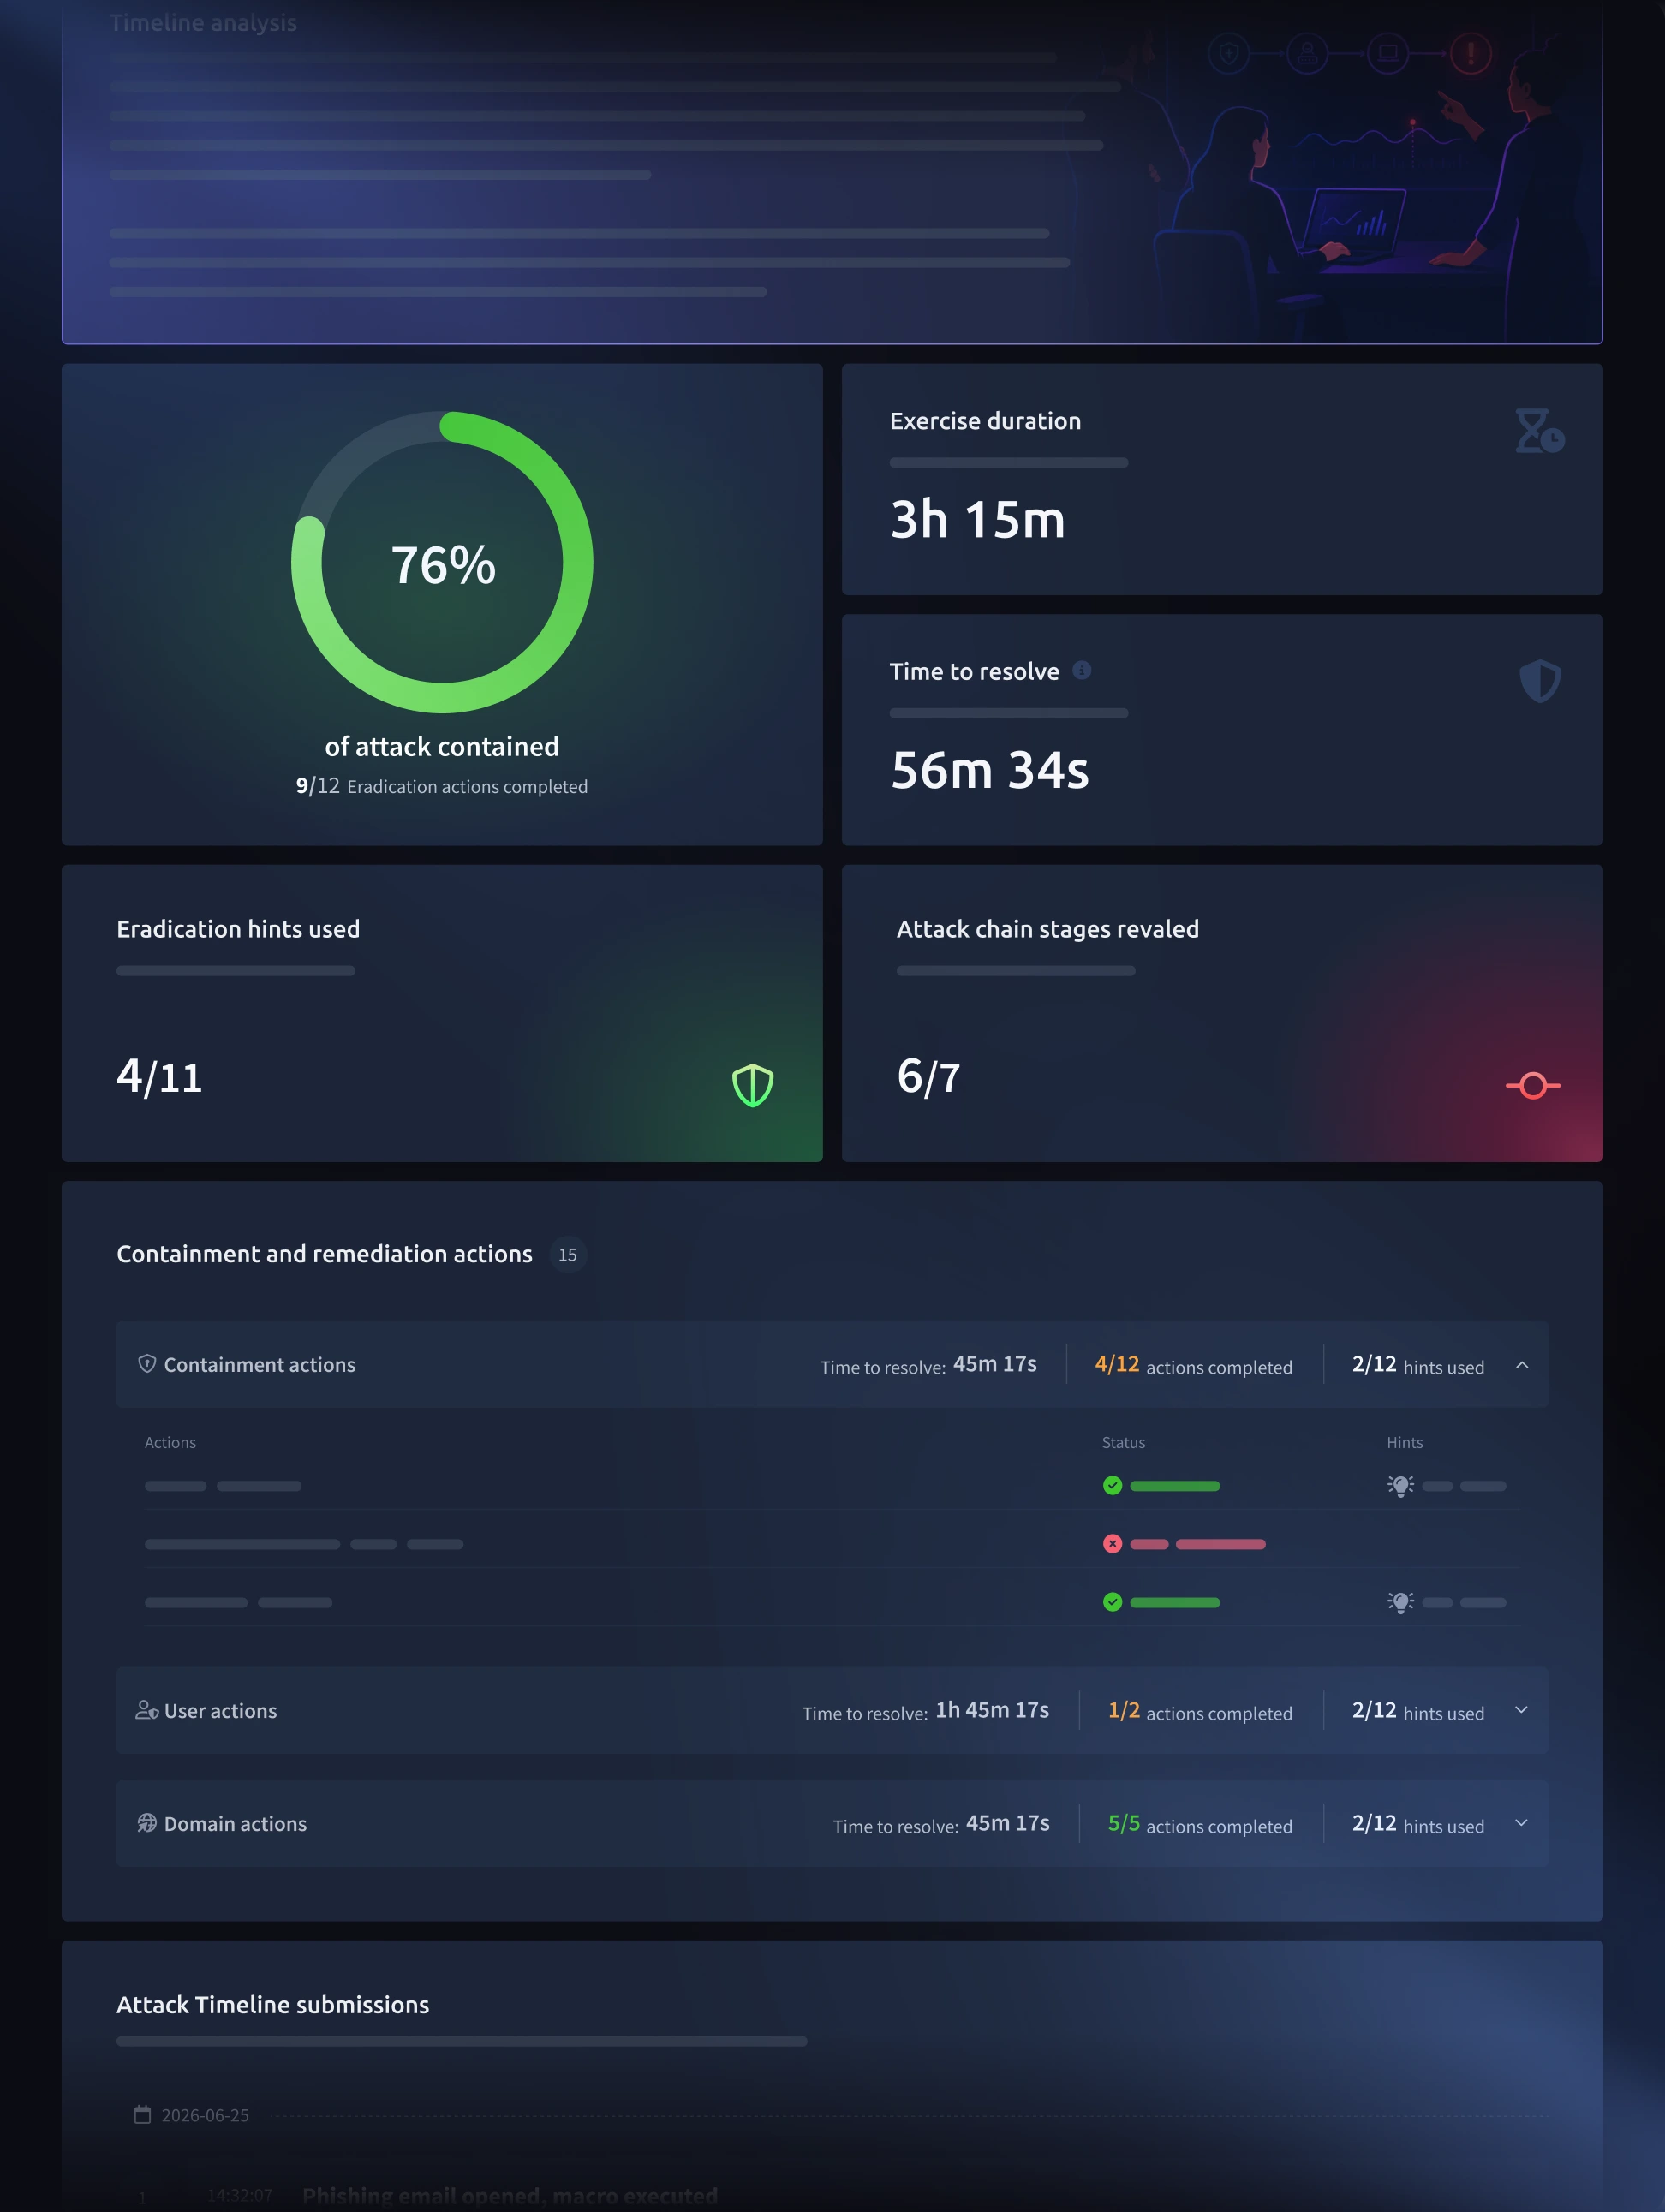
Fully executed attack chain
The team takes real containment actions across a complete incident, not a multiple-choice or Q&A-style walkthrough.
Runs on real tooling
The investigation happens in your own SIEM and EDR stack, not a sandboxed replica.