Windows incident response and forensics

Difficulty: Hard

Train for today’s threatsfrom both sides

Advanced, practical training for seasoned incident response professionals and those building their skills. 170+ real attacker techniques, mapped to MITRE ATT&CK, with the kill chain and the response side by side.
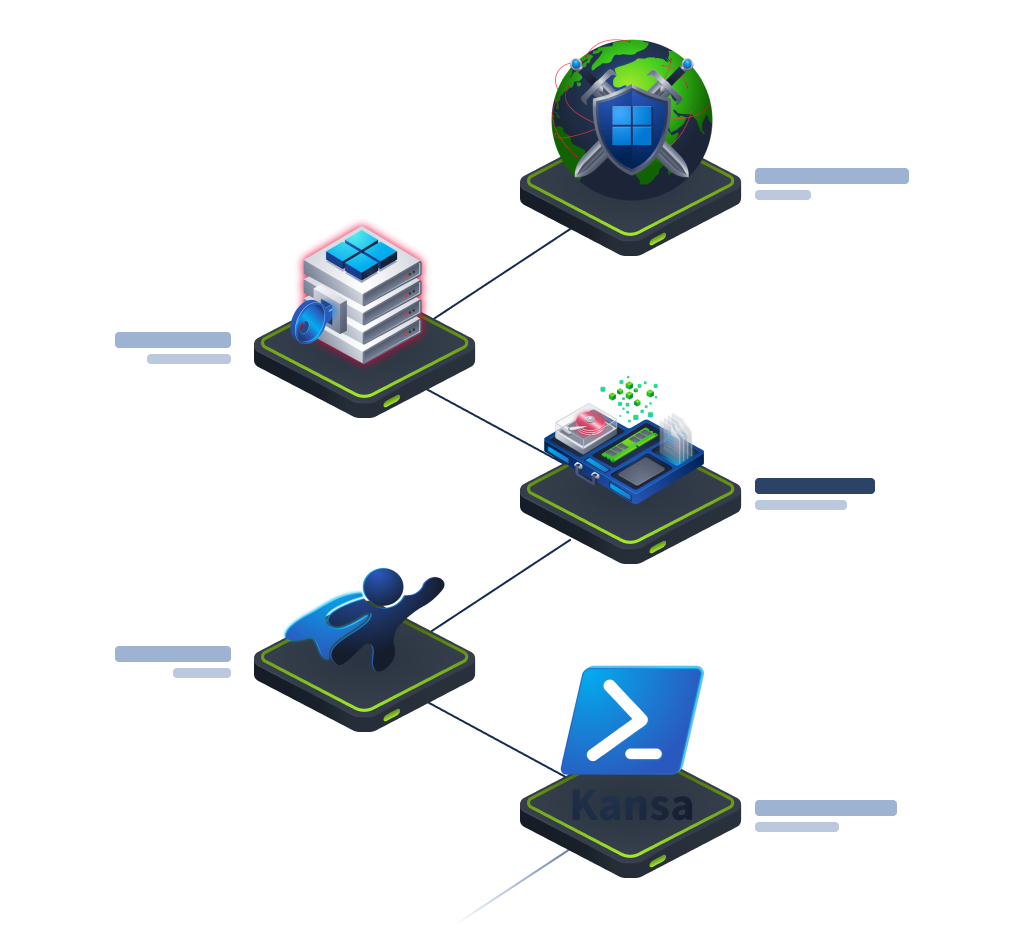
Windows incident response path stages linked from initial access through to remediation.

Trusted by1,000+ security teams and 7M+ users worldwide

Google logo
Case study
KPMG logo
Case study
SS&C logo
Case study
Network Intelligence logoAccenture logo
ARAG logo
Case study
Huntress logo
Case study
DZ Bank logo

Who it’s for

For current andaspiring incident responders

With breakout times down to an average of 29 minutes, there’s no space for hesitation in incident response. Make sure your team has built the capability before they need it, with a resource they can revisit.

  • Incident Responders
  • Forensic Analysts
  • SOC Analysts (L2–L3)
  • Threat Hunters
  • Detection Engineers
  • Security Researchers
  • Red Teamers moving to defense

About the path

Every stage of the investigation,as a Windows incident unfolds

The best defenders think like attackers. This path is designed to put your team in the attacker’s mindset, so the right response becomes second nature.

Built around real TTPs

170+ techniques mapped against leading DFIR vendor reports, designed to cover over 90% of what responders see in the wild.

Both sides of the incident

The kill chain and the response, side by side: every attacker technique paired with how to detect, contain, and remediate it.

Hands-on in DefenseBox

One ready-to-go environment, 100+ DFIR tools pre-installed. Connect, correlate, and build the incident picture with no setup and no production risk.

Self-paced, and always there

69 rooms, across 13 modules, at each responder’s own pace. A path to sharpen tested skills, and to grow new team members into incident response.

The Impact

The individual half of team readiness

The individual half of team readiness

The individual half of team readiness

This path is designed to be followed in order, and revisited to reinforce key skills.

This path is designed to be followed in order, and revisited to reinforce key skills.

This path is designed to be followed in order, and revisited to reinforce key skills.

Practitioners

Deep IR study: developing adversary fluency, closing capability gaps, and a route in from adjacent domains.

Managers

Sharpens the current IR team and opens inroads for others, spreading capability and easing reliance on a few senior specialists.

Leaders

The individual counterpart to live cyber-range exercises, building evidence of capability for clients, partners, and regulators.

Practitioners

Deep IR study: developing adversary fluency, closing capability gaps, and a route in from adjacent domains.

Managers

Sharpens the current IR team and opens inroads for others, spreading capability and easing reliance on a few senior specialists.

Leaders

The individual counterpart to live cyber-range exercises, building evidence of capability for clients, partners, and regulators.

The experience

Build capability before an incident,one practitioner at a time

Explore how Windows Incident Response & Forensics can prepare your team for the modern threat landscape.

Match threat actors to your organisation

Pick the sector and country your team operate in to see how this path maps directly to your risk profile.


32 of 32 groups match

  • Cozy Bear (APT29)

    Russia

    Government, IT and Tech, Healthcare, Defence

    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating Executables Evidence
    • Investigating PowerShell Execution
    • Investigating Script Based Execution
    • Detecting Persistent AutoStart Run Keys
  • Fancy Bear (APT28)

    Russia

    Government, Defence, Energy and Utilities

    • Uncovering Attacker Infrastructure
    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating Executables Evidence
    • Investigating PowerShell Execution
    • Detecting Persistent AutoStart Run Keys
  • Sandworm

    Russia

    Energy and Utilities, Government, Telecoms

    • Uncovering Attacker Infrastructure
    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating Executables Evidence
    • Investigating PowerShell Execution
    • Investigating Script Based Execution
  • Lazarus Group

    North Korea

    Finance, IT and Tech, Defence

    • Investigating Valid Credentials Abuse
    • Investigating Executables Evidence
    • Investigating PowerShell Execution
    • Investigating Script Based Execution
    • Detecting Persistent AutoStart Run Keys
    • Detecting Persistent Malicious Services
  • APT41

    China

    Healthcare, IT and Tech, Telecoms, Government

    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating PowerShell Execution
    • Detecting Persistent AutoStart Run Keys
    • Detecting Persistent Malicious Services
    • Detecting Persistent Accounts Manipulation
  • APT33

    Iran

    Energy and Utilities, Defence

    • Investigating Valid Credentials Abuse
    • Investigating Executables Evidence
    • Investigating PowerShell Execution
    • Investigating Script Based Execution
    • Detecting Persistent AutoStart Run Keys
    • Detecting Persistent WMI Consumers
  • OilRig (APT34)

    Iran

    Government, Finance, Energy and Utilities, Telecoms

    • Uncovering Attacker Infrastructure
    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating Executables Evidence
    • Investigating PowerShell Execution
    • Investigating Script Based Execution
  • Volt Typhoon

    China

    Energy and Utilities, Telecoms

    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating PowerShell Execution
    • Malicious Drivers and Rootkits Analysis
    • Investigating LOLBIN and Fileless
    • FAT32 Analysis
  • Turla

    Russia

    Government, Defence

    • Investigating PowerShell Execution
    • Investigating Script Based Execution
    • Detecting Persistent AutoStart Run Keys
    • Detecting Persistent WMI Consumers
    • Identifying Access Token Escalation
    • Malicious Drivers and Rootkits Analysis
  • FIN7

    Russian-speaking

    Retail and Hospitality, Finance

    • Uncovering Attacker Infrastructure
    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating Executables Evidence
    • Investigating PowerShell Execution
    • Investigating Script Based Execution
  • Scattered Spider

    English-speaking

    Telecoms, IT and Tech, Retail and Hospitality, Finance

    • Investigating Valid Credentials Abuse
    • Investigating PowerShell Execution
    • Detecting Persistent Accounts Manipulation
    • Malicious Drivers and Rootkits Analysis
    • Windows Credentials
    • Detecting NTDS Database Dumping
  • Evil Corp

    Russia

    Finance

    • Investigating Valid Credentials Abuse
    • Detecting Persistent Accounts Manipulation
    • Identifying Ransomware Operations
    • Malicious Drivers and Rootkits Analysis
    • Windows Credentials
    • Detecting LSASS Memory Dumping
  • Conti

    Russian-speaking

    Healthcare, Government, Manufacturing, Education

    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating Executables Evidence
    • Investigating PowerShell Execution
    • Detecting Persistent AutoStart Run Keys
    • Detecting Persistent Malicious Services
  • Black Basta

    Russian-speaking

    Healthcare, Manufacturing

    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating PowerShell Execution
    • Detecting Persistent Malicious Services
    • Detecting Persistent DLL Attacks
    • Malicious Drivers and Rootkits Analysis
  • Akira

    Unattributed

    Manufacturing, Education, Finance, Healthcare

    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating PowerShell Execution
    • Investigating Script Based Execution
    • Detecting Persistent Accounts Manipulation
    • Malicious Drivers and Rootkits Analysis
  • Royal/BlackSuit

    Russian-speaking

    Healthcare, Education, Manufacturing, Government

    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating PowerShell Execution
    • Detecting Persistent AutoStart Run Keys
    • Detecting Persistent Accounts Manipulation
    • Identifying Ransomware Operations
  • Play

    Unattributed

    Government, Manufacturing

    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating PowerShell Execution
    • Malicious Drivers and Rootkits Analysis
    • FAT32 Analysis
    • Advanced NTFS Analysis
  • Qilin

    Russian-speaking

    Healthcare, Manufacturing, Education

    • Investigating Public-Facing Exploitation
    • Investigating Executables Evidence
    • Investigating PowerShell Execution
    • Detecting Persistent AutoStart Run Keys
    • Identifying UAC Escalation Bypass
    • Identifying Ransomware Operations
  • Cl0p

    Russian-speaking

    Finance, IT and Tech, Healthcare, Government

    • Uncovering Attacker Infrastructure
    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating Executables Evidence
    • Investigating PowerShell Execution
    • Investigating Script Based Execution
  • FIN11

    Russian-speaking

    Finance, Retail and Hospitality

    • Investigating Public-Facing Exploitation
    • Investigating Executables Evidence
    • Identifying Ransomware Operations
  • Karakurt

    Russian-speaking

    Healthcare, Manufacturing

    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Windows Credentials
    • Investigating Data Discovery
    • Analysing Data Collection
    • Detecting External Remote Services
  • LockBit

    Russian-speaking

    Manufacturing, Healthcare, Government, Finance

    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Identifying Ransomware Operations
    • Malicious Drivers and Rootkits Analysis
    • FAT32 Analysis
    • Advanced NTFS Analysis
  • ALPHV/BlackCat

    Russian-speaking

    Healthcare, Finance, Retail and Hospitality

    • Identifying UAC Escalation Bypass
    • Delegation Abuse Detection
    • Investigating Data Discovery
    • WMI Lateral Movement Analysis
    • Identifying Ransomware Operations
    • Tracing Impact Actions
  • RansomHub

    Unattributed

    Healthcare, Government, IT and Tech, Manufacturing

    • Investigating Public-Facing Exploitation
    • Investigating PowerShell Execution
    • Detecting Persistent Accounts Manipulation
    • Malicious Drivers and Rootkits Analysis
    • Windows Credentials
    • Investigating Data Discovery
  • Medusa

    Unattributed

    Education, Healthcare, Manufacturing, IT and Tech

    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating PowerShell Execution
    • Detecting Persistent Malicious Services
    • Detecting Persistent DLL Attacks
    • Identifying UAC Escalation Bypass
  • Rhysida

    Unattributed

    Education, Healthcare, Government, Manufacturing

    • Investigating Valid Credentials Abuse
    • Investigating PowerShell Execution
    • FAT32 Analysis
    • Advanced NTFS Analysis
    • Detecting NTDS Database Dumping
    • Investigating Data Discovery
  • BianLian

    Unattributed

    Healthcare, Manufacturing

    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating PowerShell Execution
    • Detecting Persistent Accounts Manipulation
    • Malicious Drivers and Rootkits Analysis
    • Detecting LSASS Memory Dumping
  • LAPSUS$

    Unattributed

    IT and Tech, Telecoms

    • Uncovering Attacker Infrastructure
    • Investigating Valid Credentials Abuse
    • Detecting Persistent Accounts Manipulation
    • Malicious Drivers and Rootkits Analysis
    • Windows Credentials
    • Detecting NTDS Database Dumping
  • Kimsuky

    North Korea

    Government, Education, Defence

    • Uncovering Attacker Infrastructure
    • Investigating Valid Credentials Abuse
    • Investigating Public-Facing Exploitation
    • Investigating Executables Evidence
    • Investigating PowerShell Execution
    • Investigating Script Based Execution
  • MuddyWater

    Iran

    Government, Telecoms, Defence, Energy and Utilities

    • Investigating Public-Facing Exploitation
    • Investigating Executables Evidence
    • Investigating PowerShell Execution
    • Investigating Script Based Execution
    • Detecting Persistent AutoStart Run Keys
    • Identifying UAC Escalation Bypass
  • Mustang Panda

    China

    Government, Defence

    • Uncovering Attacker Infrastructure
    • Investigating Public-Facing Exploitation
    • Investigating Executables Evidence
    • Investigating PowerShell Execution
    • Investigating Script Based Execution
    • Detecting Persistent AutoStart Run Keys
  • FIN8

    Unattributed

    Retail and Hospitality, Finance

    • Investigating Valid Credentials Abuse
    • Investigating Executables Evidence
    • Investigating PowerShell Execution
    • Detecting Persistent WMI Consumers
    • Identifying Access Token Escalation
    • Malicious Drivers and Rootkits Analysis

Builds Windows IR masterybefore the incident

Give your team the depth to respond to real Windows attacks end to end, one practitioner at a time.

Explore the path

Available now on the TryHackMe for Business platform.

  • Google
  • KPMG
  • Huntress
  • ThreatLocker