Advanced ELK (Legacy)


0%
Elastic: Using Logstash
Learn how to collect, process, and transform data with Logstash.
0%
Custom Alert Rules in Wazuh
Learn how to create rules in Wazuh for your environment.
0%
Elastic: Query Languages
Search large datasets efficiently with advanced queries in Kibana.
0%
Slingshot
Can you retrace an attacker's steps after they enumerate and compromise a web server?
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
Learn about the main components of the ELK stack by going through the installation and configuring process and linking them together to form an effective log analysis utility.
This module has been replaced by our updated "Advanced Elastic" module, so we'd recommend completing that one instead! You'll still gain plenty of hands-on knowledge here, but keep in mind that some topics might be out of date.


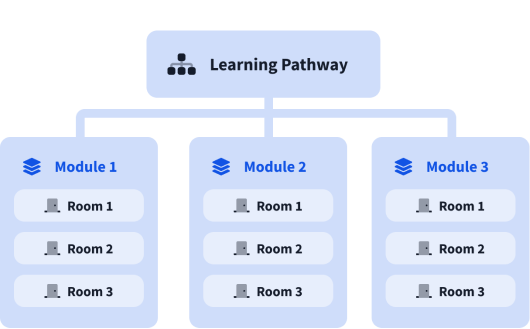
What are modules?
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).