Disk Image Analysis

0%
Intro to Cold System Forensics
A look into the concepts of cold system forensics and how DFIR teams examine offline systems.
0%
Forensic Imaging
Learn the basic concepts of forensic imaging.
0%
Autopsy
Learn how to use Autopsy to investigate artefacts from a disk image. Use your knowledge to investigate an employee who is being accused of leaking private company data.
0%
DiskFiltration
Test your Windows investigation skills on a critical data exfiltration case.
0%
ExfilNode
Continue hunting for the exfiltration footprints in the ex-employee's personal workstation.
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
The disk holds the key to almost everything on a system. Learn disk image acquisition and analysis, then dive deep into a data exfiltration case covering Windows and Linux systems.
This module dives into the significance of cold system forensics, focusing primarily on disk-based evidence. You will learn how to acquire a disk image and explore a popular tool for disk image analysis. At the end of this module, you will use your knowledge of Windows and Linux Endpoint Investigations to solve a high-stakes data exfiltration case.
Need to know

Windows Endpoint Investigation
Understand various aspects of Windows forensics and learn how to investigate the footprints of an attack on the Windows Endpoint.

Linux Endpoint Investigation
Unravel the mysteries of Linux forensics with a deep dive into live analysis, process scrutiny, and log investigations.

File System Analysis
From dissecting boot sectors and analysing key file system artefacts to carving files and solving a real-world challenge, this module will take your file system analysis skills to the next level.
What are modules?
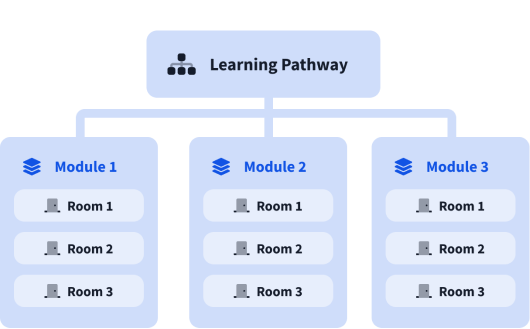
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).