SIEM Triage for SOC

0%
Log Analysis with SIEM
Learn how SIEM solutions can be used to detect and analyse malicious behaviour.
0%
Alert Triage With Splunk
Use Splunk to triage alerts and investigate malicious activity efficiently.
0%
Alert Triage With Elastic
Investigate alerts with Elastic by analyzing logs and spotting threats.
0%
ItsyBitsy
Put your ELK knowledge together and investigate an incident.
0%
Benign
Challenge room to investigate a compromised host.
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
Explore how SIEM solutions help detect early signs of attacks, investigate SOC alerts, and correlate logs to build an incident timeline.
In this module, you will learn to apply a systematic approach to SIEM investigations: where to focus your attention, and which queries to run to get the answers quickly. You will investigate various scenarios in Splunk and Elastic across web, Linux, and Windows environments, sharpening the triage skills, which every SOC analyst needs to succeed.

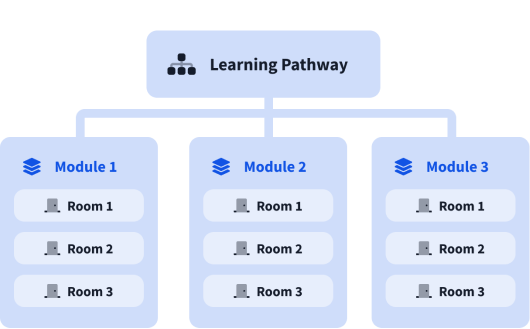
What are modules?
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).