Snort


0%
Snort
Learn how to use Snort to detect real-time threats, analyse recorded traffic files and identify anomalies.
0%
Snort Challenge - The Basics
Put your snort skills into practice and write snort rules to analyse live capture network traffic.
0%
Snort Challenge - Live Attacks
Put your snort skills into practice and defend against a live attack
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
Snort is the most widely used Open Source Intrusion Detection & Prevention System and is essential in defining malicious network activity.
This module will cover the need-to-know functionalities of Snort for any security analyst: Traffic Sniffing, Traffic Logging, Traffic Blocking, PCAP investigation, and creating IDS/IPS rules. You will learn how to use Snort for different purposes and create IDS/IPS rules for different threat scenarios. By the End of the module, you will master your Snort skills and be able to detect anomalies and threats and stop malicious activities.

What are modules?
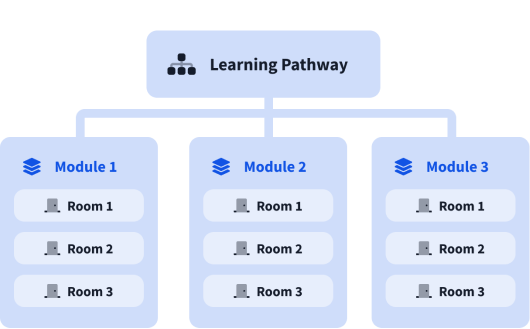
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).