Task 1: Detect the compromise using Brim.
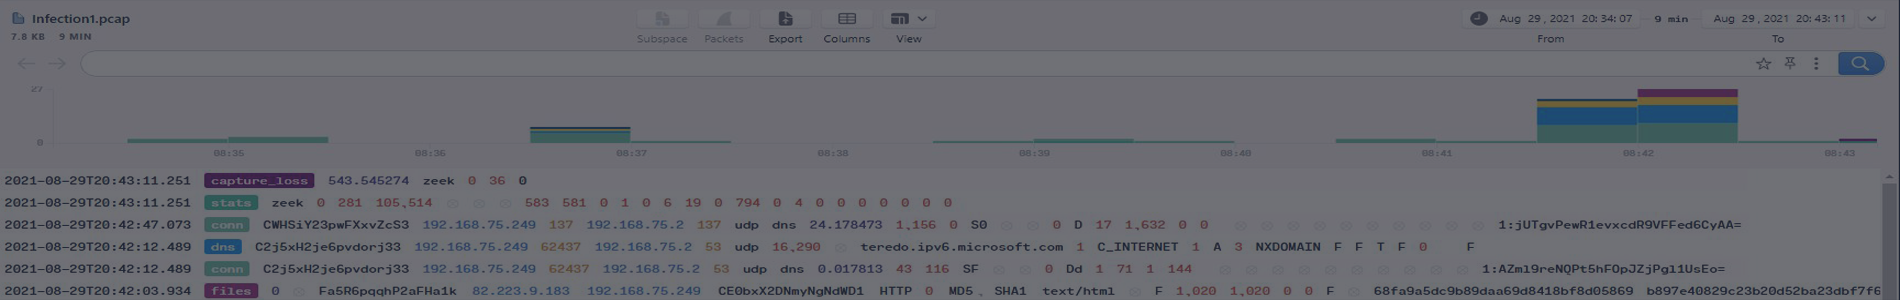
Three machines in the Finance department at Pfeffer PLC were compromised. We suspect the initial source of the compromise happened through a phishing attempt and by an infected USB drive. The Incident Response team managed to pull the network traffic logs from the endpoints. Use Brim to investigate the network traffic for any indicators of an attack and determine who stands behind the attacks.
NOTE: DO NOT directly interact with any domains and IP addresses in this challenge.
Deploy the machine attached to this task; it will be visible in the split-screen view once it is ready.
If you don't see a lab machine load then click the Show Split View button.
Answer the questions below
- Read the above.