Task 1: Pre-Reqs
Why TShark?
Bored with trying to extract packets by hand? Need to get info from a pcap file that doesn't extract easily from Wireshark? Are GUIs for losers but now you realized you can't open Wireshark? Well my friend, TShark is the solution to all your problems.
Installation
Before beginning, we need to make sure we have tshark installed on our host - If you are using the AttackBox you can skip this, as it already has tshark installed.
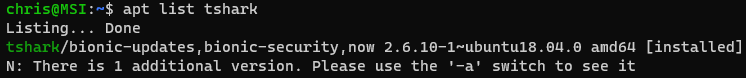
Generally, tshark is installed with Wireshark. But let's verify it's installed anyway. Run the command below to determine if it's installed or not.
apt list tshark
In my output above, we can see that it is installed. If it's not installed, sudo apt install tshark will do the trick.
The tshark program is also available in a Windows installation as tshark.exe in the Wireshark install directory.
Try running tshark -h to get the help output to make sure we can access the program properly.
Answer the questions below
Mark complete once installed/verified