Topics covered


Unlock elite skills before you enter the CTF arena.
Investigate real-world endpoints with memory dumps & disk images
Hunt attacker behavior across OS-specific artifacts
Train with hands-on labs & challenge rooms to stay sharp under pressure
DeceptiTech thought it was just another ordinary morning—until every critical system flatlined. In minutes, their network crumbled. Backups? Corrupted. Logs? Wiped clean. SIEM? Gone. You’re the last hope.
As part of an elite external DFIR unit, you’ve been called in to uncover what happened—fast. Trace the attacker’s footsteps, expose their methods, and reconstruct the breach before the damage spreads further.
This is no red team drill. No teammates. Just you, your forensic instincts, and six escalating scenarios packed with twists, artifacts, and digital debris.
Anyone can enter. Only the sharpest blue teamers will rise to the top.
Event details
Start Time: July 26th at 17:00 BST
End Time: July 28th at 18:00 BST
Single-player only
6 equally-sized scenarios
How to participate?
Complete the path
To increase your chances of winning, complete the newly released Advanced Endpoint Investigations Learning Path.
Join the Room
Enter the Honeynet Collapse room to access the challenges when they go live.
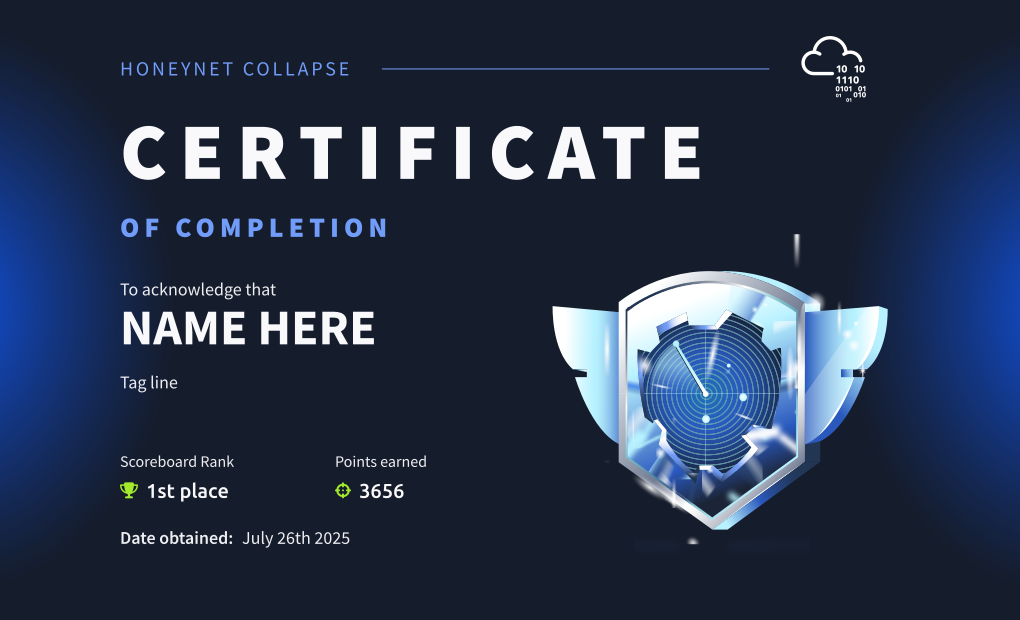
Certificate of completion
All players who complete the entire challenge will receive a certificate of completion. Showcase your skills, validate your effort and prove you have got what it takes.
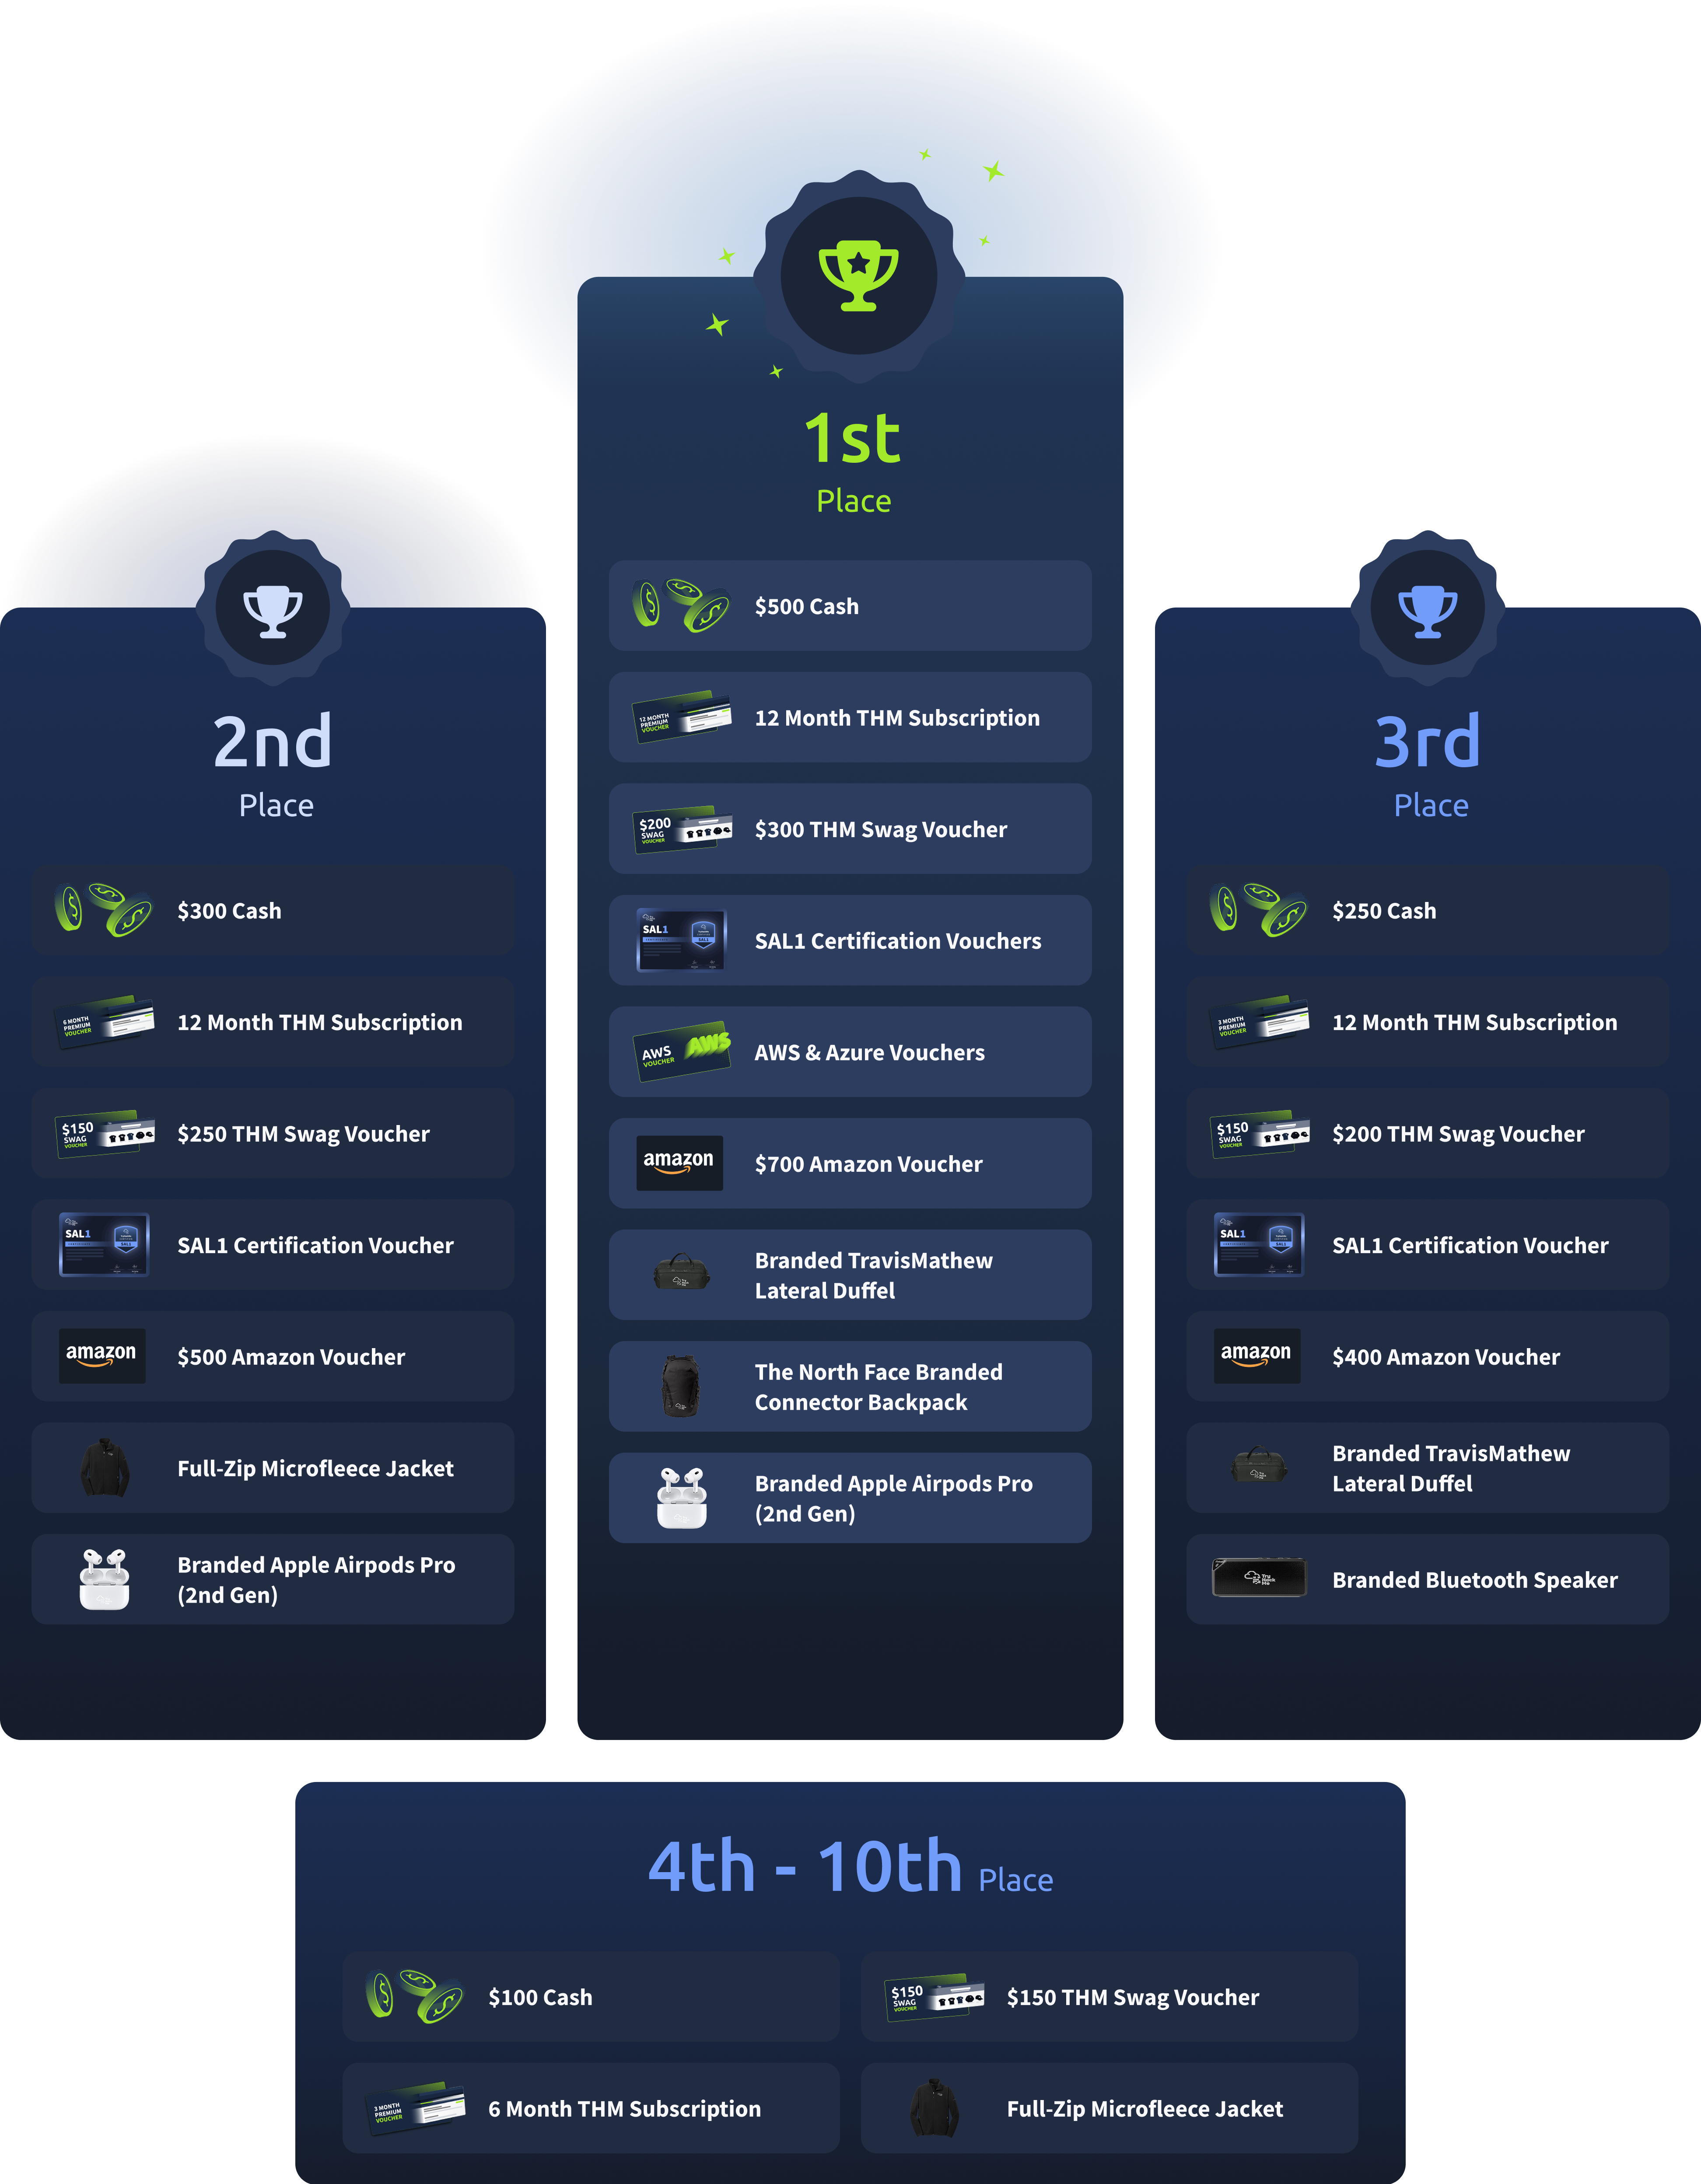
Prizes
Top players on the leaderboard will win prizes!
This is a single-player CTF. No teams, no student verification, just you and your skills. Everyone competes in the same open leaderboard.
Total prize pool value: over $10,000!
Ready to Play?
The countdown begins