Advanced Server-Side Attacks


0%
Insecure Deserialisation
Get in-depth knowledge of the deserialisation process and how it poses a vulnerability in a web app.
0%
SSRF
Discover the inner workings of SSRF and explore multiple exploitation techniques.
0%
File Inclusion, Path Traversal
Exploit File Inclusion and Path Traversal vulnerabilities.
0%
Race Conditions
Learn about race conditions and how they affect web application security.
0%
Prototype Pollution
Explore the concept of prototype pollution and its implications during pentesting.
0%
Include
Use your server exploitation skills to take control of a web app.
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
Master the skills of advanced server-side attacks, covering SSRF, File Inclusions, Deserialization, Race Conditions, and Prototype Pollution.
This module will focus on advanced server-side attack techniques an attacker uses to compromise a web app. We will learn to detect and mitigate SSRF vulnerabilities, followed by threats posed by prototype pollution and how attackers can exploit them. We will cover a range of topics, including file inclusion vulnerabilities through PHP wrappers, session files, and log poisoning. We will also learn about particular attack vectors like race conditions where simultaneous access to shared resources can lead to unpredictable behaviour. Finally, we will understand attack techniques during the deserialisation process that may allow attackers to execute malicious code on servers. Upon completing the module, you will have the skills to understand advanced server-side attack techniques attackers utilise to weaken web app security. All the rooms are equipped with realistic scenarios and real-world application examples that provide practical insights into the exploitation and mitigation of server-side vulnerabilities.


What are modules?
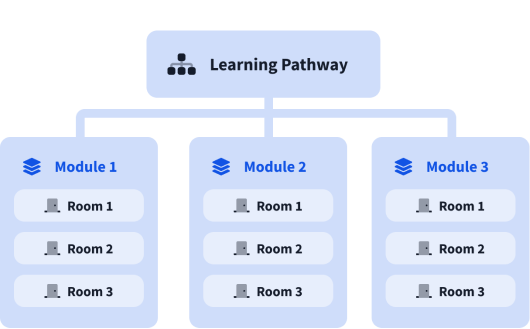
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).