Breaking Windows

0%
Blue
Deploy & hack into a Windows machine, leveraging common misconfigurations issues.
0%
Active Directory Basics
This room will introduce the basic concepts and functionality provided by Active Directory.
0%
Attacktive Directory
99% of Corporate networks run off of AD. But can you exploit a vulnerable Domain Controller?
0%
Attacking Kerberos
Learn how to abuse the Kerberos Ticket Granting Service inside of a Windows Domain Controller
0%
Post-Exploitation Basics
Learn the basics of post-exploitation and maintaining access with mimikatz, bloodhound, powerview and msfvenom
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
Almost all corporate networks use Windows, use this series to practice compromising Windows machines and Active Directory networks.
This module is designed to simulate real-world attack scenarios on Windows-based corporate environments. It provides a hands-on, structured path to learning how to compromise Windows machines and Active Directory (AD) networks. This is an essential skill set for penetration testers and blue teamers alike.
What are modules?
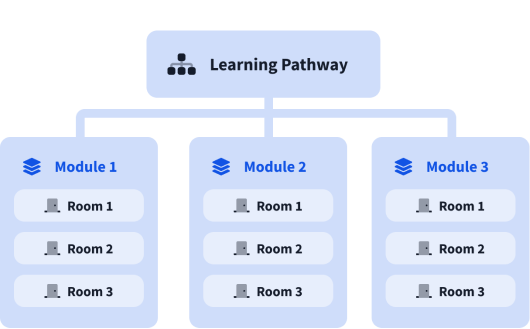
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).