
Custom Tooling


0%
Custom Tooling Using Python
Creating custom tooling for application testing using Python.
0%
Custom Tooling using Burp
Creating custom tooling for application testing using Burp Plugins.
0%
Tooling via Browser Automation
Creating custom tooling for application testing using Selenium and Playwright.
0%
NoScope: Finding RCE
NoScope found an Alf.io RCE zero-day (CVE-2026-35482). Exploit it manually and watch AI solve it.
0%
CAPTCHApocalypse
When crypto interferes, automate.
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
Build and automate custom tools (including AI-driven) using Python, Burp Suite, and browser automation to exploit and test web applications efficiently.
In real-world engagements, off-the-shelf tools can fall short. This module focuses on developing custom tooling to extend your offensive capabilities. You’ll start with Python to automate requests, manage sessions, and script around protections. Then, you’ll write custom Burp Suite extensions to inspect and manipulate encrypted or obfuscated traffic. Finally, you’ll use browser automation to simulate user actions, bypass client-side controls, and exploit dynamic applications. By the end of this module, you’ll know how to build targeted, reusable tools tailored for complex web application scenarios.
Need to know
Cryptographic Failures
Learn to exploit cryptographic vulnerabilities, including ECB Oracles, Padding Oracles, Insecure Randomness, and Length Extension Attacks.

Authentication
Master exploiting authentication mechanisms through real-world scenarios, covering enumeration and brute force, session management, OAuth, MFA/2FA and JWT vulnerabilities.
What are modules?
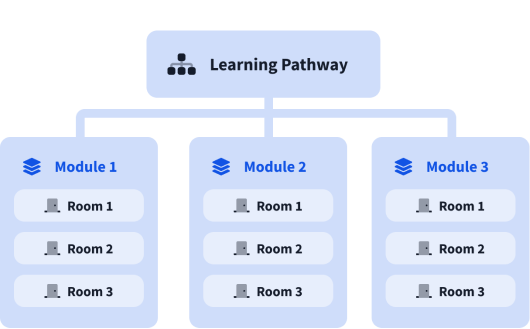
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).