Introduction to Web Hacking


0%
Walking An Application
Manually review a web application for security issues using only your browsers developer tools. Hacking with just your browser, no tools or scripts.
0%
Content Discovery
Learn the various ways of discovering hidden or private content on a webserver that could lead to new vulnerabilities.
0%
Subdomain Enumeration
Learn the various ways of discovering subdomains to expand your attack surface of a target.
0%
Authentication Bypass
Learn how to defeat logins and other authentication mechanisms to allow you access to unpermitted areas.
0%
IDOR
Learn how to find and exploit IDOR vulnerabilities in a web application giving you access to data that you shouldn't have.
0%
File Inclusion
This room introduces file inclusion vulnerabilities, including Local File Inclusion (LFI), Remote File Inclusion (RFI), and directory traversal.
0%
Intro to SSRF
Learn how to exploit Server-Side Request Forgery (SSRF) vulnerabilities, allowing you to access internal server resources.
0%
Intro to Cross-site Scripting
Learn how to detect and exploit XSS vulnerabilities, giving you control of other visitors' browsers.
0%
Race Conditions
Learn about race conditions and how they affect web application security.
0%
Command Injection
Learn about a vulnerability allowing you to execute commands through a vulnerable app, and its remediations.
0%
SQL Injection
Learn how to detect and exploit SQL Injection vulnerabilities
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
Get hands-on, learn about and exploit some of the most popular web application vulnerabilities seen in the industry today.
In this module you will learn about the most common web application vulnerabilities, understanding what makes it vulnerable and putting theory into practice by hacking website simulations. You will also be taught how to identify, exploit and prevent each vulnerability.

What are modules?
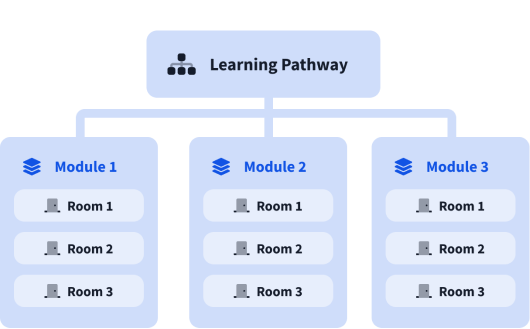
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).