Network Reconnaissance

0%
Passive Reconnaissance
Learn about the essential tools for passive reconnaissance, such as whois, nslookup, and dig.
0%
Active Reconnaissance
Learn how to use simple tools such as traceroute, ping, telnet, and a web browser to gather information.
0%
Protocols and Servers
Learn about common protocols such as HTTP, FTP, POP3, SMTP and IMAP, along with related insecurities.
0%
Protocols and Servers 2
Learn about attacks against passwords and cleartext traffic; explore options for mitigation via SSH and SSL/TLS.
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
Gather intelligence on a target through passive and active reconnaissance, then probe the network services that keep modern infrastructure running.
Reconnaissance is where every engagement begins, and this module covers both halves. You’ll start with passive techniques that mine public records, search engines, and DNS data without ever touching the target, then move into active probing with classic network utilities to map live systems. From there, you’ll work through the everyday protocols and services that keep networks running, learning how each one behaves and how attackers turn its quirks against it.


What are modules?
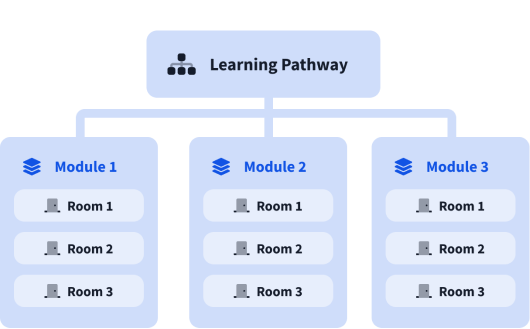
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).