Vulnerability Knowledge

0%
Understanding Vulnerability Databases
Explore vulnerability databases, their importance, and practical usage during pentesting.
0%
Vulnerability Scanning Tools
Learn about scanning tools such as Nmap, OpenVAS, and Nikto, and explore the world of pentesting.
0%
Basic Vulnerability Identification Techniques
Learn the basics of vulnerability identification techniques.
0%
NoScope: Finding RCE
NoScope found an Alf.io RCE zero-day (CVE-2026-35482). Exploit it manually and watch AI solve it.
0%
n8n: CVE-2025-68613
Learn how adversaries can exploit the CVE-2025-68613 vulnerability in n8n.
0%
AD: BadSuccessor
Use the BadSuccessor attack for privilege escalation in an Active Directory environment.
0%
CVE-2026-46300: Fragnesia
Exploit Fragnesia, an LPE that surfaced due to dirtyfrag's patch.
0%
CVE-2026-42945: Nginx Rift
Exploit NGINX Rift, an unauthenticated heap overflow RCE in NGINX's rewrite module since 2008.
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
Learn how to research vulnerabilities in public databases, scan for them with industry tools, and identify them in real systems.
This module is about how penetration testers stay ahead of the curve, starting with the public vulnerability databases (CVE, NVD, vendor advisories) that catalog every known weakness in modern software. You’ll then move into the scanning tools that do the heavy lifting at scale, before picking up the manual identification techniques that turn raw scanner output into reliable, actionable findings. By the end, you’ll know how to research a CVE from first principles and validate whether it actually applies to a target.
Need to know

Networking
Learn about the OSI model and TCP/IP networking layers. Explore the different plaintext and secure networking protocols that we use every day.

Nmap
Learn how to leverage the Nmap network scanner to discover live hosts and open ports using basic and advanced scan options.

Burp Suite
Burp Suite is the industry standard tool for web application hacking, and is essential in any web penetration test.
Next steps

Metasploit and Exploitation
Master Metasploit and the manual exploitation skills behind it, from scanning and post-exploitation to building your own shells and payloads.

OWASP Top 10 (2025)
Explore, exploit, and learn how to remediate the most critical web application security risks listed in the OWASP Top 10 (2025) list through interactive labs and practical recommendations.
What are modules?
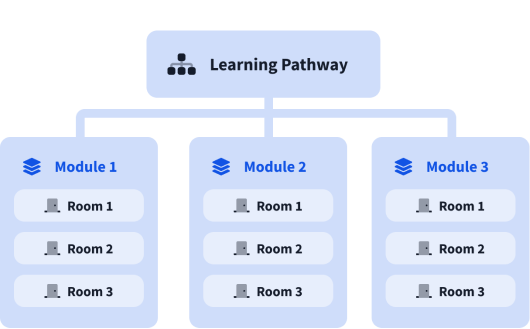
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).