Task 1: Scenario
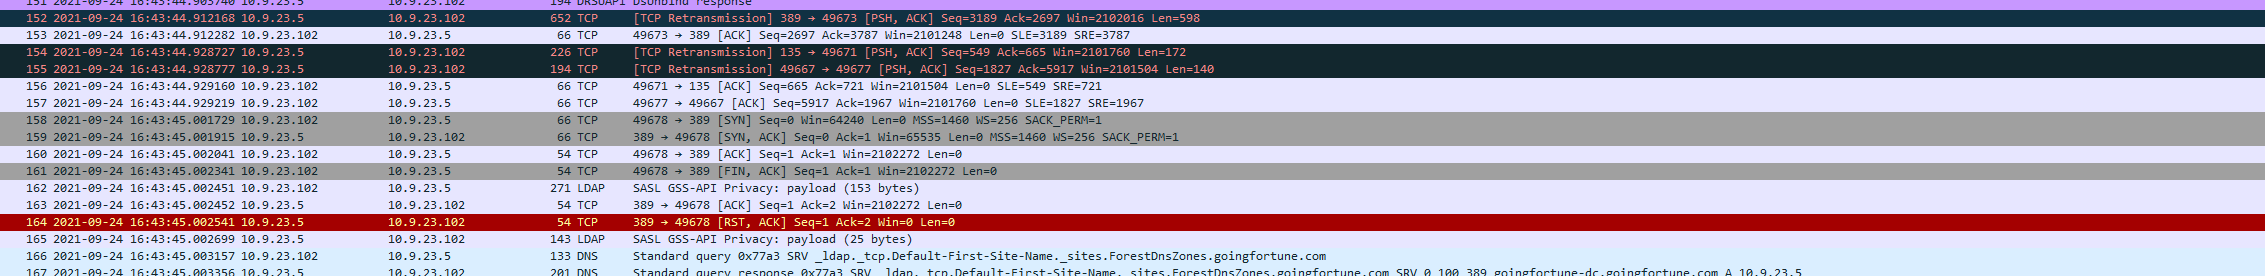
Eric Fischer from the Purchasing Department at Bartell Ltd has received an email from a known contact with a Word document attachment. Upon opening the document, he accidentally clicked on "Enable Content." The SOC Department immediately received an alert from the endpoint agent that Eric's workstation was making suspicious connections outbound. The pcap was retrieved from the network sensor and handed to you for analysis.
Task: Investigate the packet capture and uncover the malicious activities.
*Credit goes to Brad Duncan for capturing the traffic and sharing the pcap packet capture with InfoSec community.
NOTE: DO NOT directly interact with any domains and IP addresses in this challenge.
Deploy the machine attached to this task; it will be visible in the split-screen view once it is ready.
If you don't see a lab machine load, then click the Show Split View button.
Answer the questions below
- Read the above.