Task 1: Introduction
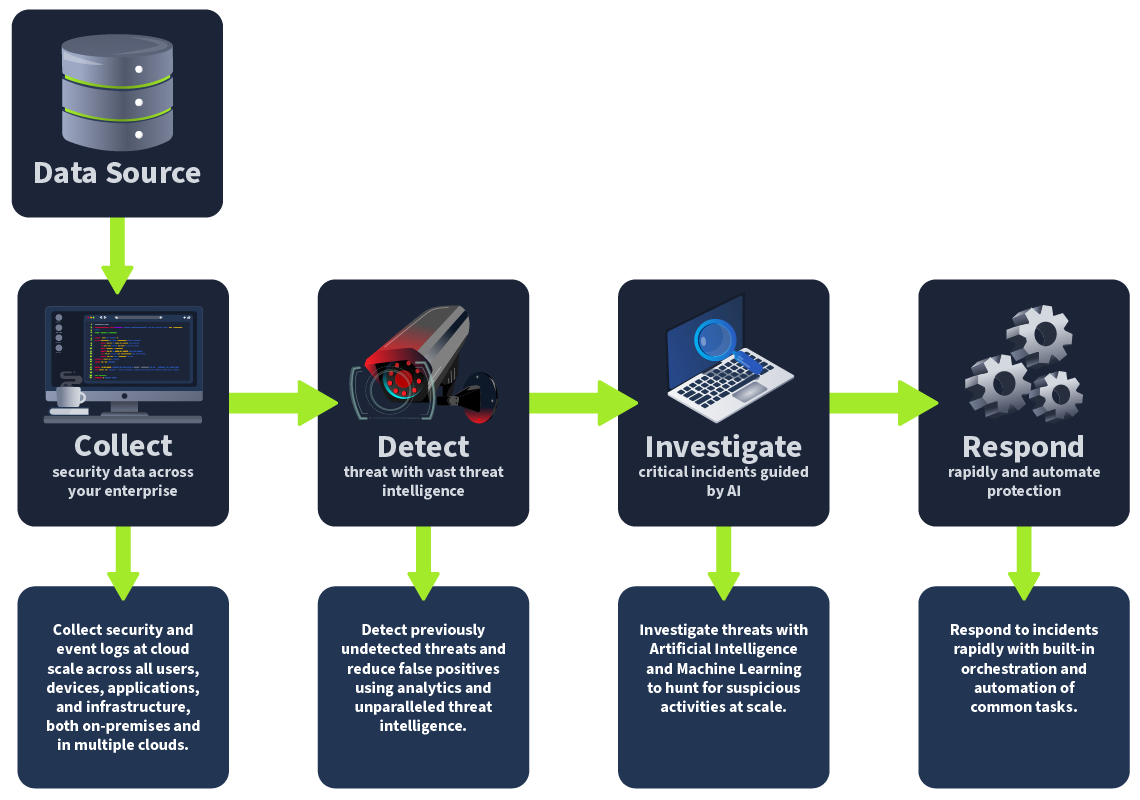
This room introduces you to the analysis of security logs with Microsoft Sentinel KQL. As security engineers, we think of security logs as treasures because they can help us discover the hidden activities within our infrastructure. A quick background intro: Microsoft Sentinel is a cloud-native security information and event management (SIEM) product that utilizes ingested logs to provide better visibility into your environment. On the other hand, Kusto Query Language (KQL) is the tool used to proactively reveal the hidden secrets within those logs if you are the curious and hands-on type.
Imagine being able to:
- Track down rogue user activities accurately and identify potential breaches before they happen.
- Unravel complex security incidents by correlating events and figuring out every attacker's moves.
- Automating repeated tasks to focus on more serious threats and investigations.
The focus of this room is Kusto Query Language (KQL), which empowers you, the security analyst/engineer, to become a security sleuth, proactively hunting for threats to ensure your organization's digital infrastructure is safe from attackers. Let's dive into the world of KQL to discover the power of security logs analysis.
Learning Objectives
This room aims to provide you with the fundamental knowledge and skills necessary to use Kusto Query Language (KQL) for security analysis within MS Sentinel Log Analytics workspace. Upon completion, you will be able to:
- Better understand the core concepts and functionalities of Microsoft Sentinel as a Security Information and Event Management (SIEM) solution.
- Easily understand the benefits of using Kusto Query Language (KQL) in Microsoft Sentinel for day-to-day security operations.
- Understand how KQL interacts with data stored within MS Sentinel Log Analytics workspaces and its uses in querying and analyzing them.
Prerequisites
- Having completed the Microsoft Sentinel module.
Answer the questions below
- Let's go!