Back to all networks



SQL Server Trust Exploitation
Exploit SQL Server permissions, linked trusts, NTLM coercion and relay in a Windows domain.
medium
To access material, start machines and answer questions login.
Press 'Start' to begin
Please join this room to start the network
This will be enabled once the network is live. Please wait.
Can't reconnect? Try regenerating your VPN config.
When there are enough votes, the network will reset to its default state
Microsoft Server (MSSQL) is a relational database management system used to store, query, and protect structured business data. Applications normally talk to its Database Engine over the Tabular Data Stream () protocol, commonly on port 1433. A SQL Server can accept SQL logins or Windows identities, run under a Windows service account, expose extended procedures such as xp_cmdshell, and connect to other data sources through linked servers. Each of those components creates a security boundary that is important during an assessment.
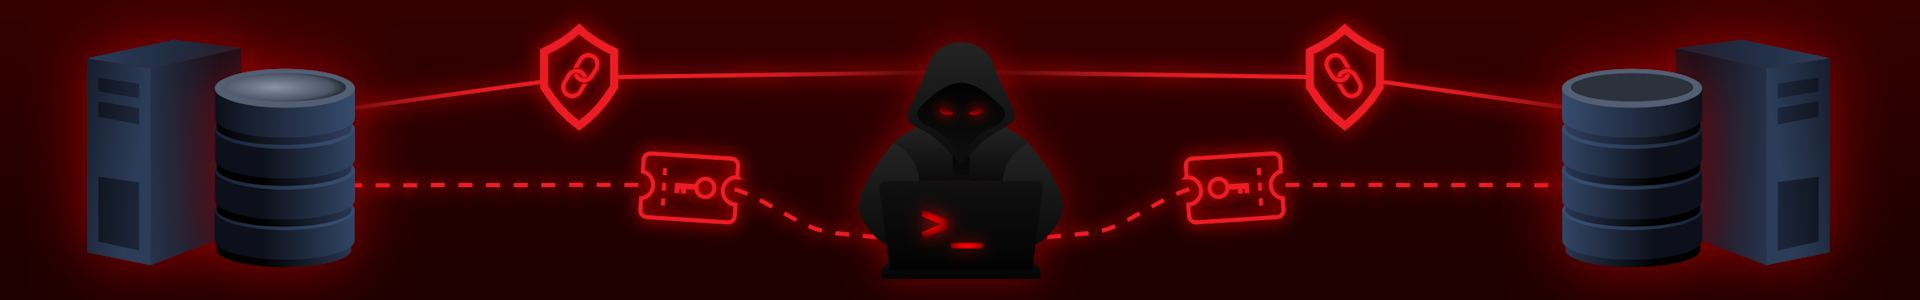
In this walkthrough, you'll attack a deliberately vulnerable pair of domain-joined SQL Servers. You will begin with a restricted SQL login, identify an unsafe linked-server mapping, cross from SQL into Windows command execution, coerce a service account to authenticate to your AttackBox, and relay that live authentication back to SQL Server. The room is intentionally guided so you can see how separate database and Windows identities combine into one attack chain.
Learning Objectives
- Enumerate an MSSQL login's effective identity, permissions, and trust paths
- Explain the difference between configuring, invoking, and executing
xp_cmdshell - Obtain an operating-system callback through a download cradle
- Exploit a privileged linked-server mapping and run commands on the remote host
- Capture and relay outbound authentication to MSSQL
Prerequisites
- Basic SQL query syntax
- Familiarity with Windows accounts and NTLM
- Basic command-line experience
Lab Access
Start the room network with the Start button underneath the network diagram, as well as your AttackBox by pressing the Start AttackBox button at the top of the page. Then use the credentials below to connect to SQL01 on TCP port 1433.
Credentials
Only needed if you are using your own machine.
Username
analyst
Password
AnalystAccess!24
IP address
192.168.13.111
Connection via
Impacket
mssqlclient 'analyst:AnalystAccess!24@192.168.13.111' -port 1433
Ready to learn Cyber Security?
The SQL Server Trust Exploitation room is only available for Premium or Max subscribers. Signup now to access more than 500 free rooms and learn cyber security through a fun, interactive learning environment.
Already have an account? Log in