Operation Reroute

Can you intercept traffic from another ISP?

Task 1: Taking Over the Network

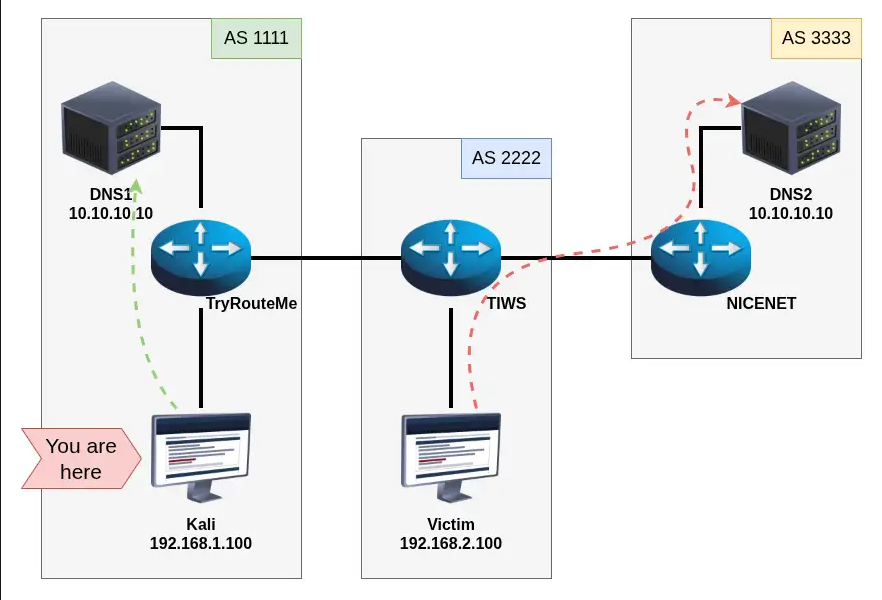
We've gained access to one of TryRouteMe's (TRM) core network devices through a Kali implant. We should now be able to hijack traffic for any of their users! One of our main objectives while hacking TRM was to spy on one of their VIP users. But wait... It seems our initial research was wrong and our target isn't even a client of TRM!

We know for a fact that the victim uses Doogle's DNS at 10.10.10.10. Strangely enough, it seems there's more than one server with such an IP in the world... What does this even mean? And how are we supposed to hijack the victim's traffic if we only have access to TTM's router?

Your Kali jumpbox can be reached via:

telnet MACHINE_IP 6001

From the Kali machine, you can SSH into the TTM router at IP 192.168.1.1 with the following credentials:

Credentials


Username
 
ttm
 
Password
 
ttm2024
 
IP address
 
MACHINE_IP
 
Connection via
 
SSH
ssh user@MACHINE_IP
 

Note: The domain name for this challenge is contained in the DNS requests made by the victim to the 10.10.10.10 server.

Answer the questions below

  1. After hijacking the route, DNS1 starts receiving queries from the victim. What is the internal domain name the victim is trying to resolve?

Room Icon

Operation Reroute

Can you intercept traffic from another ISP?

hard

60 min

33

User profile photo.
User profile photo.

To access material, start machines and answer questions login.

Score updated
Score updated

Set up your virtual environment

To successfully complete this room, you'll need to set up your virtual environment. This involves starting both your AttackBox (if you're not using your VPN) and Lab Machines, ensuring you're equipped with the necessary tools and access to tackle the challenges ahead.
Attacker machine
Status:Off
Lab machine
Status:Off

Network diagram of three autonomous systems connected in a line. AS 1111 contains the Kali machine (192.168.1.100, marked 'You are here'), the TryRouteMe router and DNS1 (10.10.10.10). AS 2222 contains the TIWS router and the Victim machine (192.168.2.100). AS 3333 contains the NICENET router and DNS2, which also has the address 10.10.10.10. A green dashed arrow shows Kali's traffic reaching DNS1. A red dashed arrow shows the Victim's traffic being routed through NICENET to DNS2.

We've gained access to one of TryRouteMe's (TRM) core network devices through a Kali implant. We should now be able to hijack traffic for any of their users! One of our main objectives while hacking TRM was to spy on one of their VIP users. But wait... It seems our initial research was wrong and our target isn't even a client of TRM!

We know for a fact that the victim uses Doogle's at 10.10.10.10. Strangely enough, it seems there's more than one server with such an IP in the world... What does this even mean? And how are we supposed to hijack the victim's traffic if we only have access to TTM's router?

Your Kali jumpbox can be reached via:

telnet MACHINE_IP 6001

From the Kali machine, you can into the TTM router at IP 192.168.1.1 with the following credentials:

Credentials


Username
 
ttm
 
Password
 
ttm2024
 
IP address
 
MACHINE_IP
 
Connection via
 
SSH
ssh user@MACHINE_IP
 

Note: The domain name for this challenge is contained in the DNS requests made by the victim to the 10.10.10.10 server.

Answer the questions below

After hijacking the route, DNS1 starts receiving queries from the victim. What is the internal domain name the victim is trying to resolve?