Advanced Splunk

0%
Splunk: Exploring SPL
Learn and explore the Splunk's Search Processing Language.
0%
Splunk: Setting up a SOC Lab
Set up a Splunk lab and ingest logs with the Universal Forwarder.
0%
Splunk: Dashboards and Reports
Explore reports, alerts, and dashboards with Splunk.
0%
Splunk: Data Manipulation
Learn how to parse and manipulate data in Splunk.
0%
Fixit
Fix the log parsing issue and analyze the logs in Splunk.
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
Understand advanced Splunk capabilities to search data for anomalies by creating complex search queries, applying regex, and creating presentable reports and dashboards.
In this module, we will install a Splunk instance and set up a forwarder to ingest logs from different log sources. We will learn how to create complex search queries and use regex to parse logs to improve incident investigation and threat hunting capabilities. Additionally, we will learn how to create presentable reports and dashboards to assist with the analysis.
Need to know

Security Information and Event Management
Understand how SIEM works and get comfortable creating simple and advanced search queries to look for specific answers from the ingested logs.
Log Analysis
Log analysis is collecting, parsing and processing log files and turning data into actionable knowledge to detect security threats and anomalies and identify system performance issues.
What are modules?
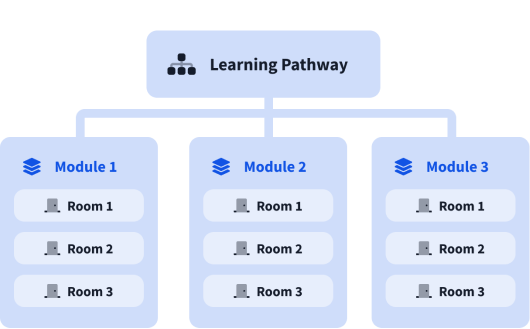
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).