Web Application Vulnerabilities II

0%
Session Management
Learn about session management and the different attacks that can be performed against insecure implementations.
0%
Broken Authentication
Learn how to defeat logins and other authentication mechanisms to allow you access to unpermitted areas.
0%
File Inclusion
This room introduces file inclusion vulnerabilities, including Local File Inclusion (LFI), Remote File Inclusion (RFI), and directory traversal.
0%
Command Injection
Learn about a vulnerability allowing you to execute commands through a vulnerable app, and its remediations.
0%
API Pentesting
Explore how to identify and exploit common API security vulnerabilities.
0%
Support
Pentest the Support Ops platform to exploit vulnerabilities and achieve RCE.
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
Tackle deeper web vulnerabilities like broken authentication, command injection, and API flaws, then prove yourself in a live challenge.
This module takes your web hacking beyond the classics into the vulnerabilities that turn small oversights into full-system compromises. You’ll begin with the mechanics of session management and authentication, then move on to server-side attacks such as directory traversal and command injection, and finish with the rapidly expanding attack surface of modern APIs. A live security challenge closes the module, so the techniques are battle-tested before you carry them into the rest of the path.


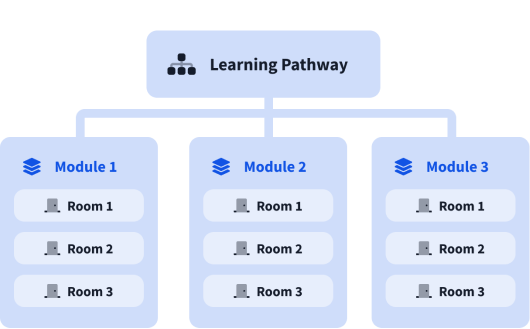
What are modules?
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).