Windows Security Monitoring

0%
Windows Logging for SOC
Start your Windows monitoring journey by learning how to use system logs to detect threats.
0%
Windows Threat Detection 1
Explore common Initial Access methods on Windows and learn how to detect them.
0%
Windows Threat Detection 2
Discover how to detect and analyze the first steps of threat actors after breaching Windows.
0%
Windows Threat Detection 3
Learn how threat actors manage to maintain access to the breached Windows hosts.
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
Learn how Windows logging works and how you can use it to detect common Windows attacks - all through real-world examples and challenging, hands-on threat detection labs.
This module explores the Windows attacks and defenses directly on the host, without SIEM abstractions. You will use Event Viewer, the command line, and file system navigation to detect real malware samples and learn the corresponding MITRE techniques. This hands-on experience will sharpen your Windows skills and prepare you for real-world SOC work.

What are modules?
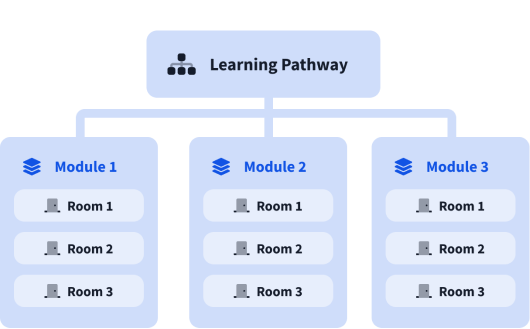
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).