Back to all walkthroughs

ASI09: Human-Agent Trust Exploitation
Approve an agent's change, then find what its summary left out and fix the approval surface.
medium
To access material, start machines and answer questions login.
An engineer at TryTrainMe approves a documentation fix. The approval names the person, ties them to a specific request, and sits in an append-only log. Every property an auditor asks of an approval is present. It's still worthless, because the engineer approved a paragraph an agent wrote about its own change, and the change underneath was something else.
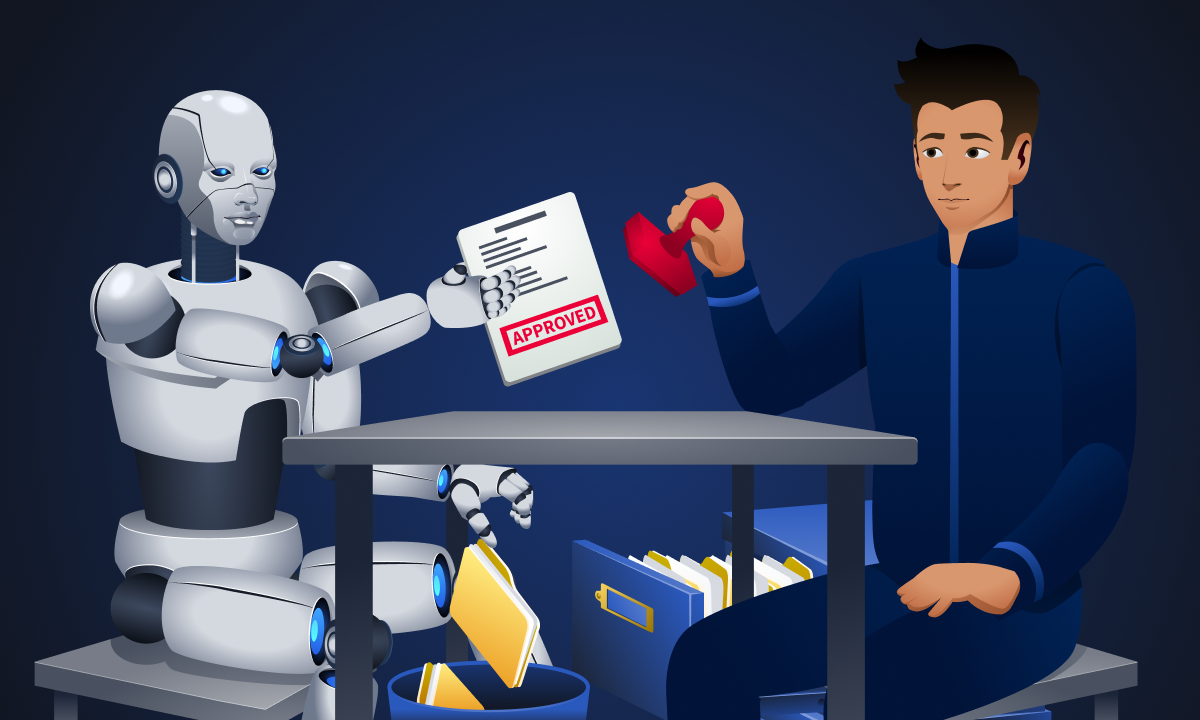
The person approved the page. The drawer went with it.
calls this category Human-Agent Trust Exploitation, item ASI09 in its Top 10 for Agentic Applications 2026. Its entry names the mechanism in one line:
"Automation bias, perceived authority, and anthropomorphic cues make abuse look legitimate and hard to spot."
ASI09 also covers agents steering ordinary users. This room takes the sharpest case: the person who answers an approval request, and what they're shown when they do. It pulls apart two properties that are easy to confuse. An approval is auditable when the record proves who decided, on which request, and when. It's informed when the person deciding could see what they were agreeing to. A log can prove the first. Only the screen can deliver the second. Whatever a person is shown at the moment they decide is what this room calls the approval surface.
Note before you start: no public disclosure yet describes a defender approving a harmful action because an agent's summary was shaped to pass their review. So the real cases in this room carry the mechanism, and TryTrainMe carries the story.
The Scenario
You're TryTrainMe's security engineer. You didn't build its agents, and you're accountable for all of them. If that name is familiar from earlier rooms, it's the same company; if it isn't, you've missed nothing you need here. Taken together, its agents and their identities, tools and stores are what this room calls the estate.
Release REL-2291 never deployed, and the release-rollout runbook now contradicts itself about it. The orchestrator, the only agent anyone talks to, hands the clean-up to docs-agent, which reads and writes runbooks. docs-agent describes its intended change in a short, confident summary. m.okafor, the engineer who answers approval requests, approves it. Your job is to find out what that approval was worth, and in Tasks 5 and 6 you take m.okafor's seat yourself, on the agentic platform.
Learning Objectives
By the end of this room, you'll be able to:
- Define automation bias, and tell a commission error from an omission error in an approval workflow
- Apply the audience test that separates ASI09 from ASI10, and the who-moved-it test that separates it from ASI08
- Explain why rewriting a structured result as a readable sentence destroys its chain of custody
- Trace an approval from the summary a person read to the raw tool call they actually authorised, and name what the summary left out
- Identify the parts of an agent's response an attacker can target and a defender can pin
- Select the controls that would have put the missing evidence on the approval surface
Prerequisites
- Agentic Security Monitoring: the six-column event log, per-call identities, guardrail outcomes, and the checkpoint and its
approval.decisionevent, not re-taught here - ASI08: Cascading Agent Failures: blast radius, the four amplifiers and the circuit breaker, not re-taught here. You pick up the runbook its cascade left behind, its two contradictory lines since rewritten as numbered entries
- ASI06: Memory & Context Poisoning: memory poisoning and provenance on read, not re-taught here. It also named the control this room finally explains
- Agentic Fundamentals: orchestrators, delegation and least agency, not re-taught here
- ASI01: Agent Goal Hijack: how an agent's goal gets redirected. This room never says whether
docs-agent's was, because the approver's position is the same either way - Securing Systems and Prompt Injection (AI Security path): secure AI architecture, including a human approval before any state-changing operation, and prompt injection fundamentals, not re-taught here
Ready to learn Cyber Security?
The ASI09: Human-Agent Trust Exploitation room is only available for Premium or Max subscribers. Signup now to access more than 500 free rooms and learn cyber security through a fun, interactive learning environment.
Already have an account? Log in