Task 1: Welcome to Windows IR
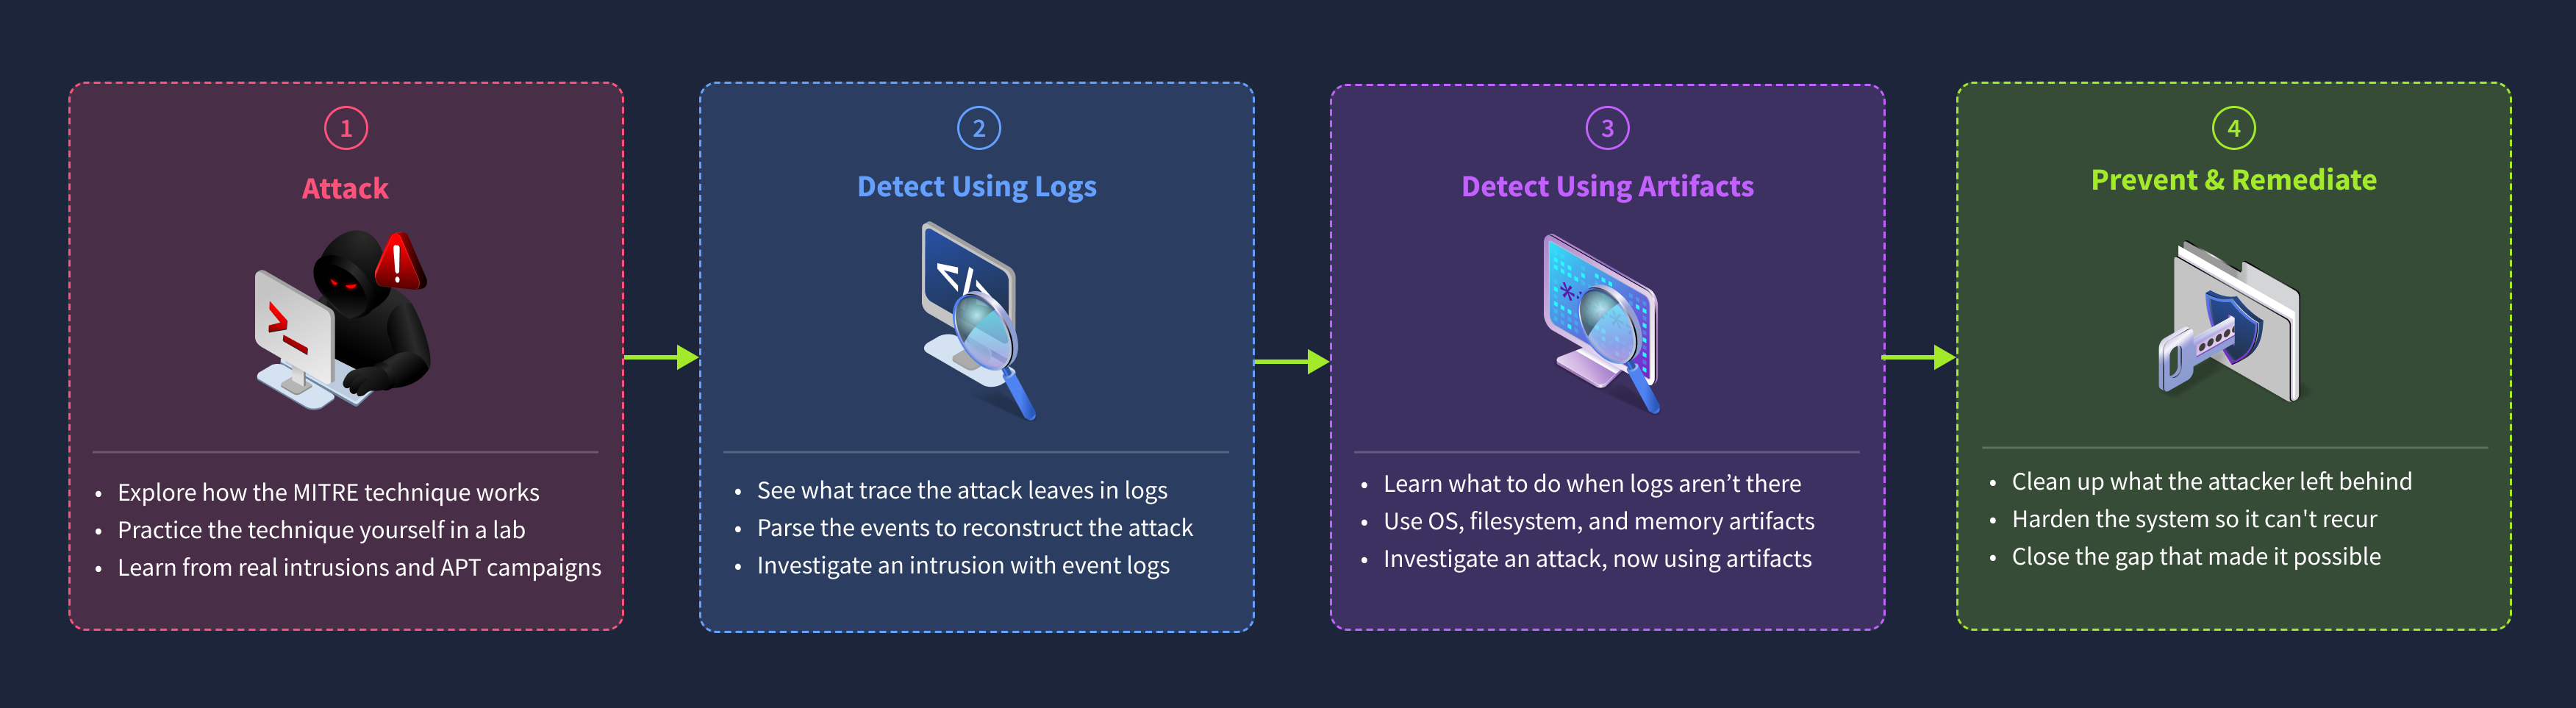
Active Directory remains a core technology for enterprises; by most estimates, around 95% of Fortune 500 companies use it. As a result, most ransomware attacks target AD environments, and you must know AD and Windows internals to respond properly. Throughout the path, you'll see how AD attacks occur from the adversary's point of view and gain technical skills to detect them, using both logs and forensic artifacts.
Path Structure
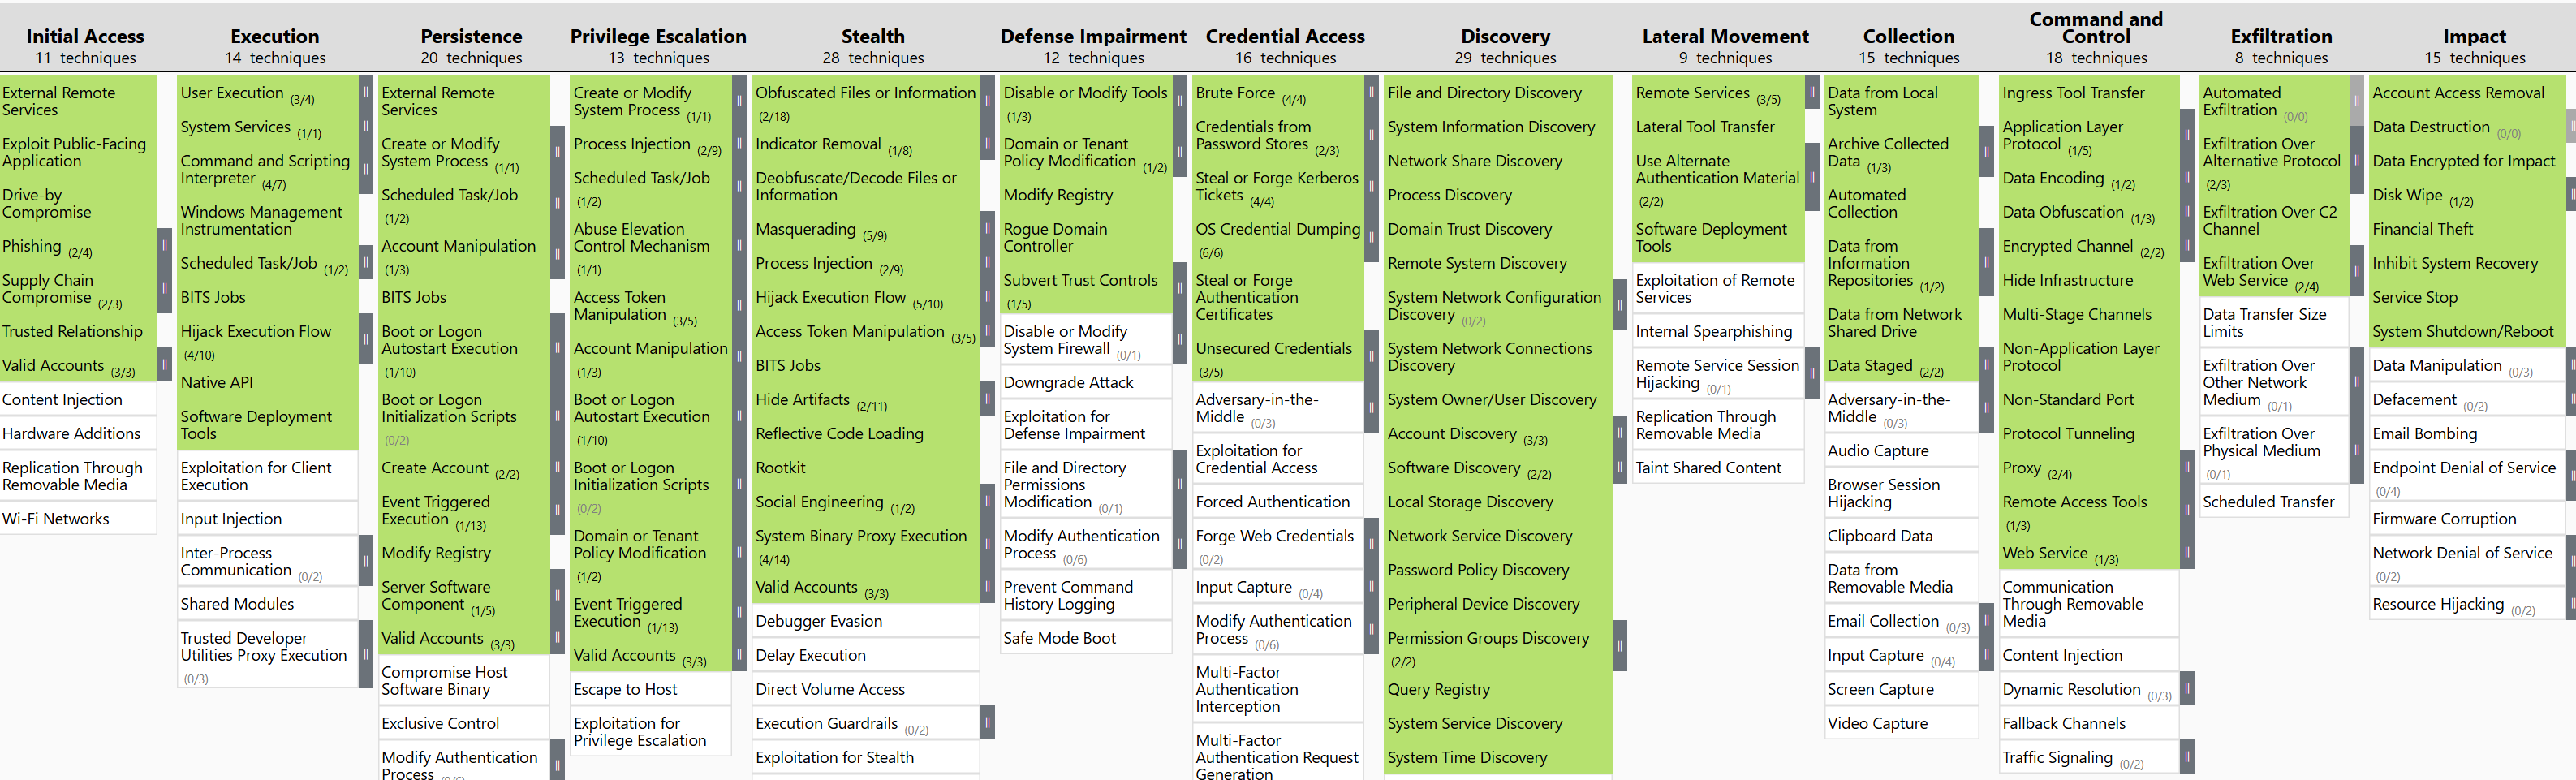
This path is mapped to MITRE ATT&CK and focuses on the most common techniques observed in real-world intrusions. By the end, you'll know how to detect, investigate, and defend against roughly 100 techniques shown below. Note that the SOC L2 path isn't a strict prerequisite, but it's a great addition and covers most gaps in this path.
MITRE techniques covered in the Windows IR path (in green)
Who Is It For
- DFIR professionals seeking practice with real-world incidents
- Security experts preparing for advanced blue-team certifications
- SOC analysts and engineers expanding into the DFIR world
- Red teamers wanting a defensive view of their engagements
- Other roles may still find some of the rooms valuable to:
- See how the Windows OS works behind the scenes
- Learn the mindset of attackers and defenders
- Explore mitigations against attacks on Windows
Answer the questions below
Let's go!