Memory Analysis

0%
Memory Analysis Introduction
Learn how memory analysis helps detect threats during live investigations.
0%
Memory Acquisition
Learn the techniques and best practices to acquire digitally sound memory.
0%
Volatility Essentials
Learn how to perform memory forensics with Volatility!
0%
Windows Memory & Processes
Analyze a memory dump of a Windows host and uncover malicious processes.
0%
Windows Memory & User Activity
Trace user behavior, command execution, file access, and macro-based payload delivery from memory.
0%
Windows Memory & Network
Identify C2 traffic & post-exploit activity in Windows memory.
0%
Linux Memory Analysis
Learn how to investigate and find the footprints of a threat actor in the Linux memory.
0%
Supplemental Memory
Investigate lateral movement, credential theft, and additional adversary actions in a memory dump.
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
Learn how to analyse volatile memory to detect suspicious activity, track user behaviour, and investigate network threats through hands-on labs.
In this module, we'll learn how to investigate volatile memory to uncover signs of suspicious behaviour, hidden programs, user activity, and potential security threats. We will explore how memory stores valuable information about running programs, system usage, and network interactions that often disappear after shutdown. Through guided practice and real scenarios, we'll develop the skills to identify unusual patterns, trace actions taken on a system, and connect the dots to understand what happened. Each step combines clear explanations with practical exercises using the Volatility Framework to build confidence and prepare us for real investigation work.

What are modules?
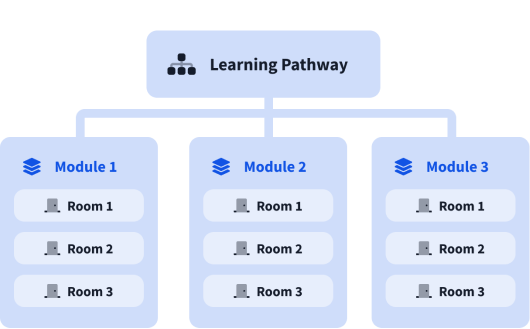
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).