Web Application Vulnerabilities I

0%
SQL Injection Introduction
Learn how to detect and exploit SQL Injection vulnerabilities.
0%
CSRF Introduction
Understand CSRF vulnerability and practice exploiting insecure state-changing requests.
0%
XSS Introduction
Learn to detect and exploit XSS to control visitors’ browsers.
0%
Intro to SSRF
Learn how to exploit Server-Side Request Forgery (SSRF) vulnerabilities, allowing you to access internal server resources.
0%
IDOR
Learn how to find and exploit IDOR vulnerabilities in a web application giving you access to data that you shouldn't have.
0%
Recruit
Infiltrate Recruit's new portal. Map the site, hunt for flaws, and gain unauthorised access
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
Exploit five of the most impactful web vulnerabilities, from SQL injection to IDOR, and prove your skills in a hands-on challenge.
This module walks you through five of the most impactful vulnerabilities in modern web applications, examining how each works, why it persists, and how attackers exploit it in the wild. You’ll start with the classics, SQL injection and cross-site scripting, before moving to subtler bugs like CSRF, SSRF, and IDOR that often slip past even experienced developers. A final hands-on challenge brings all the techniques together, so you finish the module able to spot these issues quickly and exploit them with confidence.


What are modules?
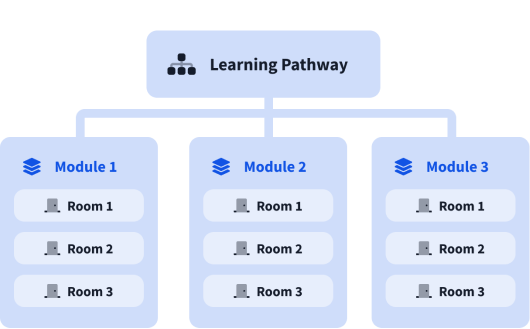
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).