Task 1: Introduction
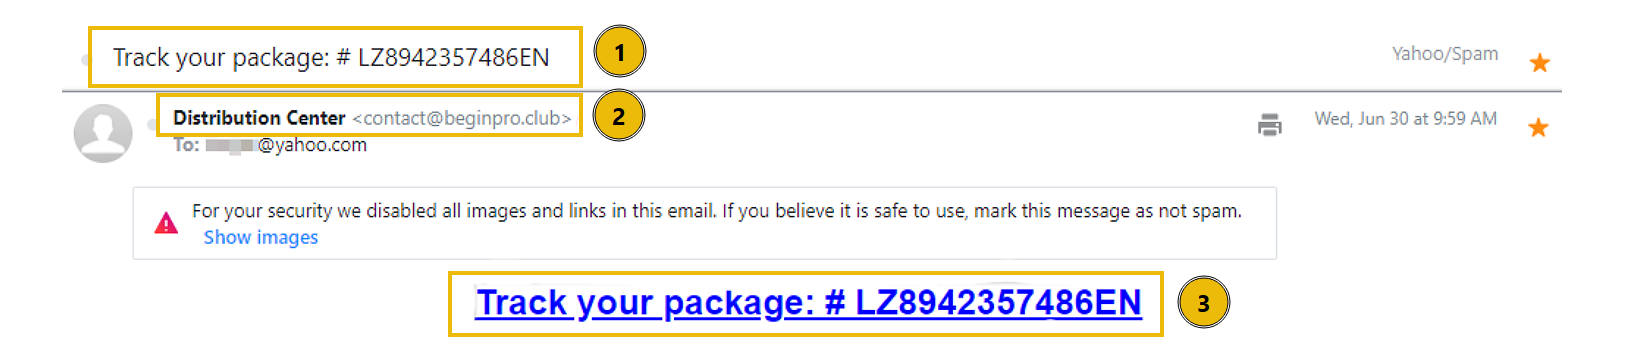
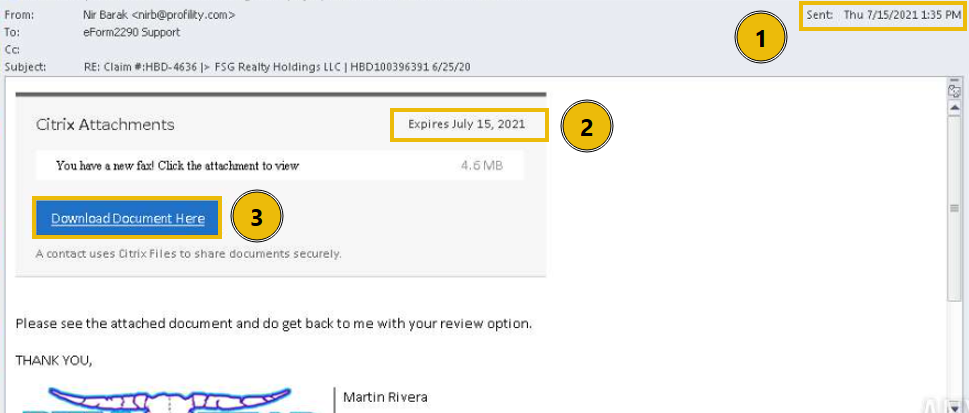
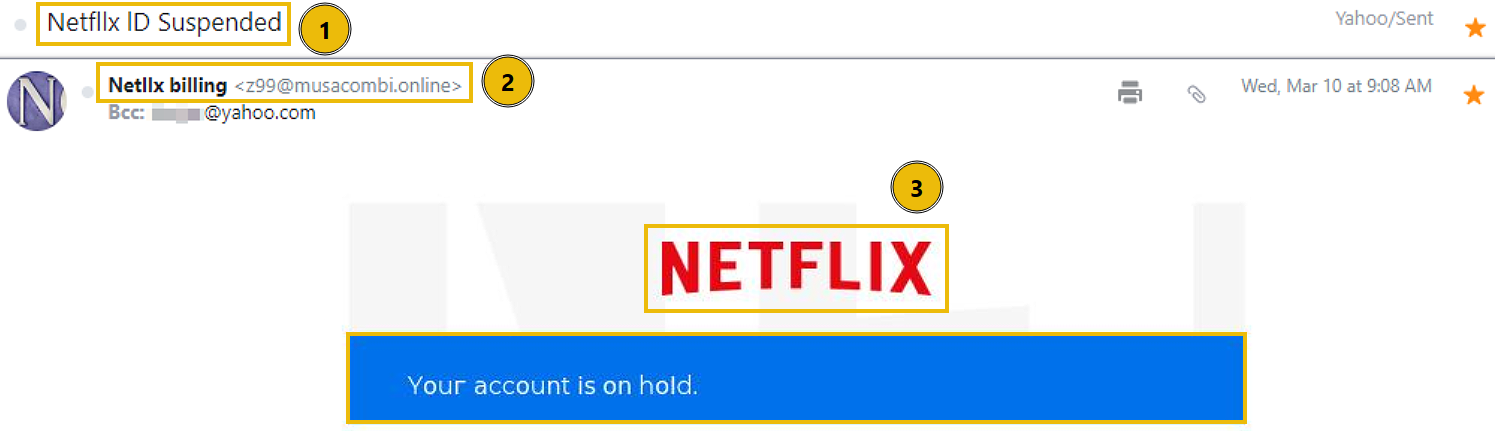
In the first room of the Phishing Analysis module, Phishing Analysis Fundamentals, you learned how to investigate email headers and bodies to identify common red flags. Now, we transition to practice by examining real phishing email samples. This room focuses on the tactics attackers use to mirror legitimate communications. By analyzing real samples, you will learn to identify the subtle nuances that distinguish a routine notification from a sophisticated credential harvesting attempt. Note: The samples throughout this room contain information from actual emails. Proceed with caution if you attempt to interact with any IP, domain, or attachment.
Objectives
- Identify common social engineering tactics used in phishing
- Analyze red flags contained within phishing emails
- Detect link manipulation and tracking pixels
- Deconstruct credential harvesting and attachment manipulation
Prerequisites
- Check out Phishing Analysis Fundamentals for an overview of email communications and analysis
Answer the questions below
I am ready to analyze phishing emails!