Microsoft 365 for SOC

0%
M365 Monitoring Basics
Learn the importance of Entra ID and M365 in modern SOC environments and explore their logs.
0%
Entra ID Monitoring
Learn the main threats and defenses in Entra ID environments and how to detect them.
0%
Exchange Online Monitoring
Learn about attacks leveraging Exchange Online and how to detect them in a SOC.
0%
SharePoint Online Monitoring
Explore attacks on SharePoint and learn detection strategies from a SOC perspective.
0%
Microsoft Intune Monitoring
Learn how to monitor Intune and protect yourself from mass wiper attacks.
Topic Rewind Recap
Lock in what you learned with a recap. Earn points and keep your streak.
Explore core concepts of Entra ID and M365, the threats targeting them, and how to monitor their logs and activity as a SOC analyst.
This module covers the core concepts and security relevance of Microsoft Entra ID and Microsoft 365 in enterprise environments. You'll build a foundational understanding of how these platforms work, then explore the biggest threats and attack techniques that target them. From there, the module moves into monitoring, walking through the key logs, events, and signals from Entra ID, Exchange, SharePoint, and Intune that matter most from a SOC perspective. Throughout, you'll work hands-on with a Splunk instance loaded with real platform logs, putting theory into practice as you investigate suspicious activity across these environments.

What are modules?
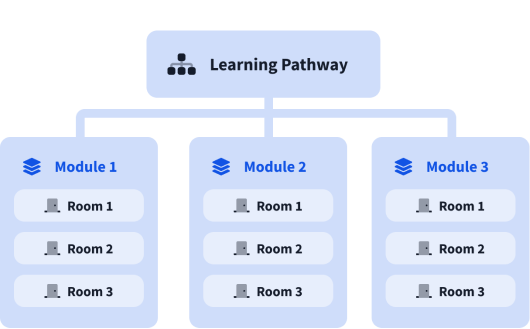
A learning pathway is made up of modules, and a module is made of bite-sized rooms (think of a room like a mini security lab).